Inside the developer workflow
Findings arrive where code is reviewed, while the change is still fresh.
- Scans on pull requests and in CI
- Findings inline in the review
- Fix guidance with every finding
HashGo · Static application security testing
 HashGo SAST
Live
HashGo SAST reads your source code without running it, follows data from input to where it is used, and points to the exact line that needs to change.
Product tour
What your team sees after sign-in: every repository, every finding and the proof behind it.
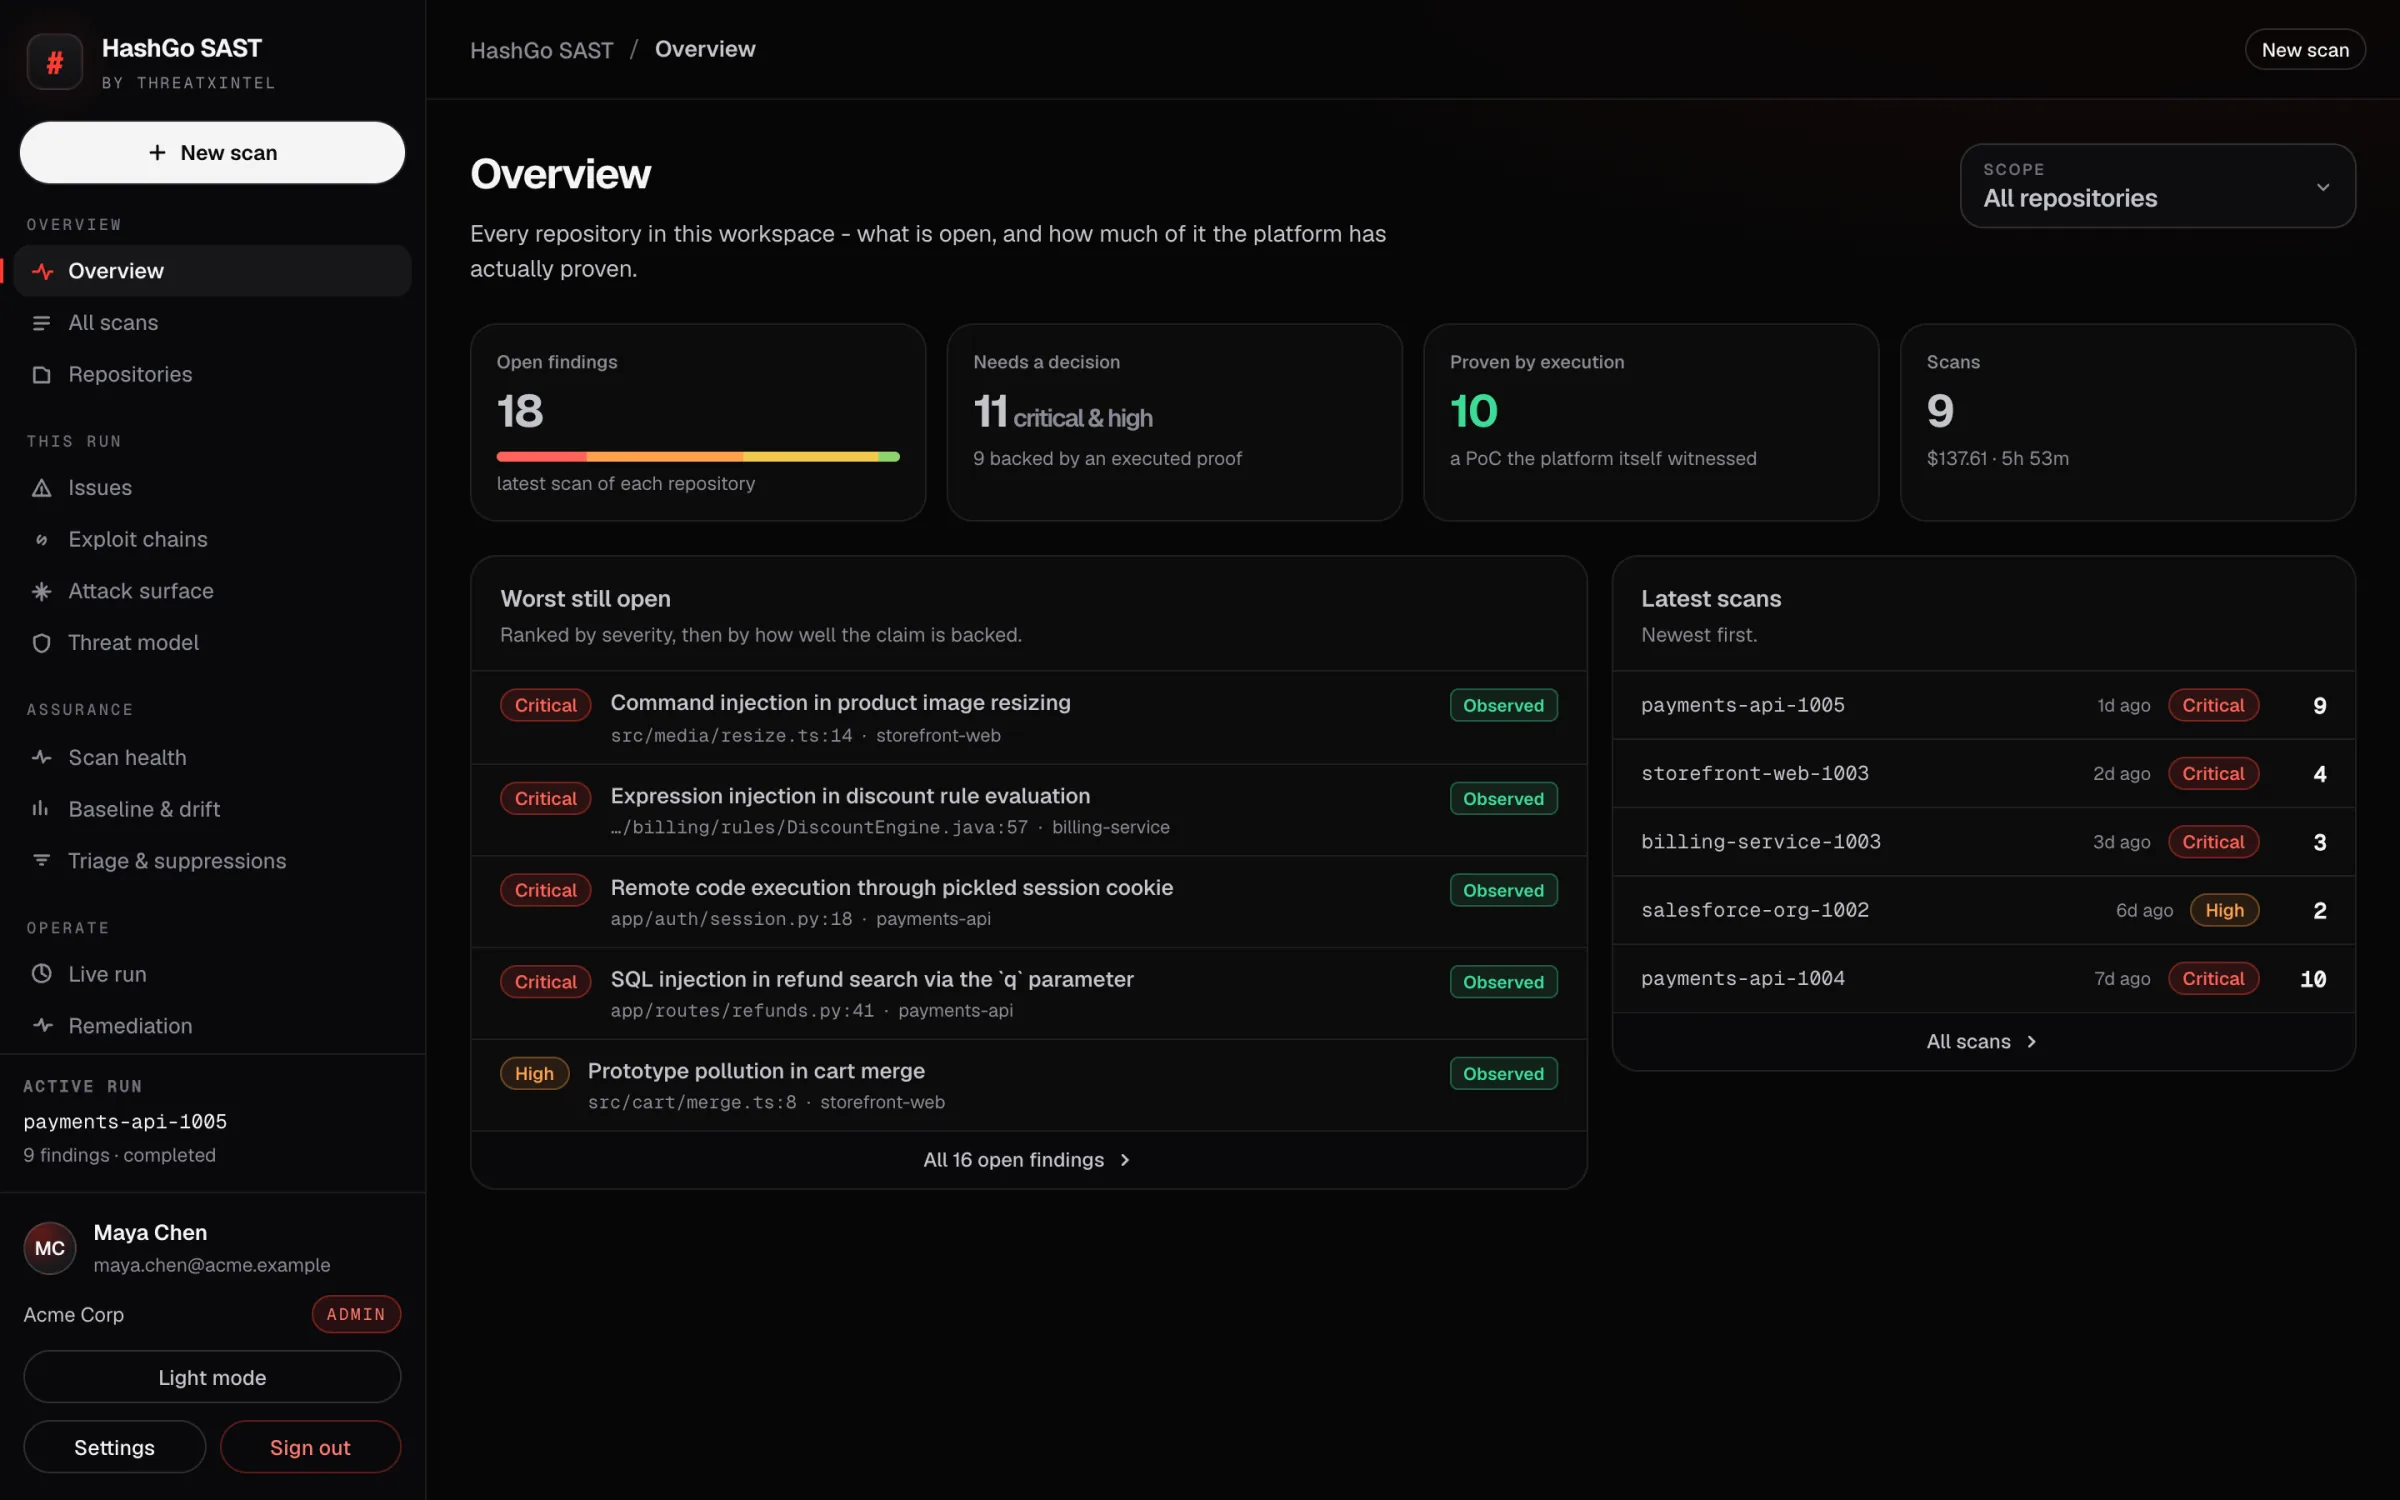
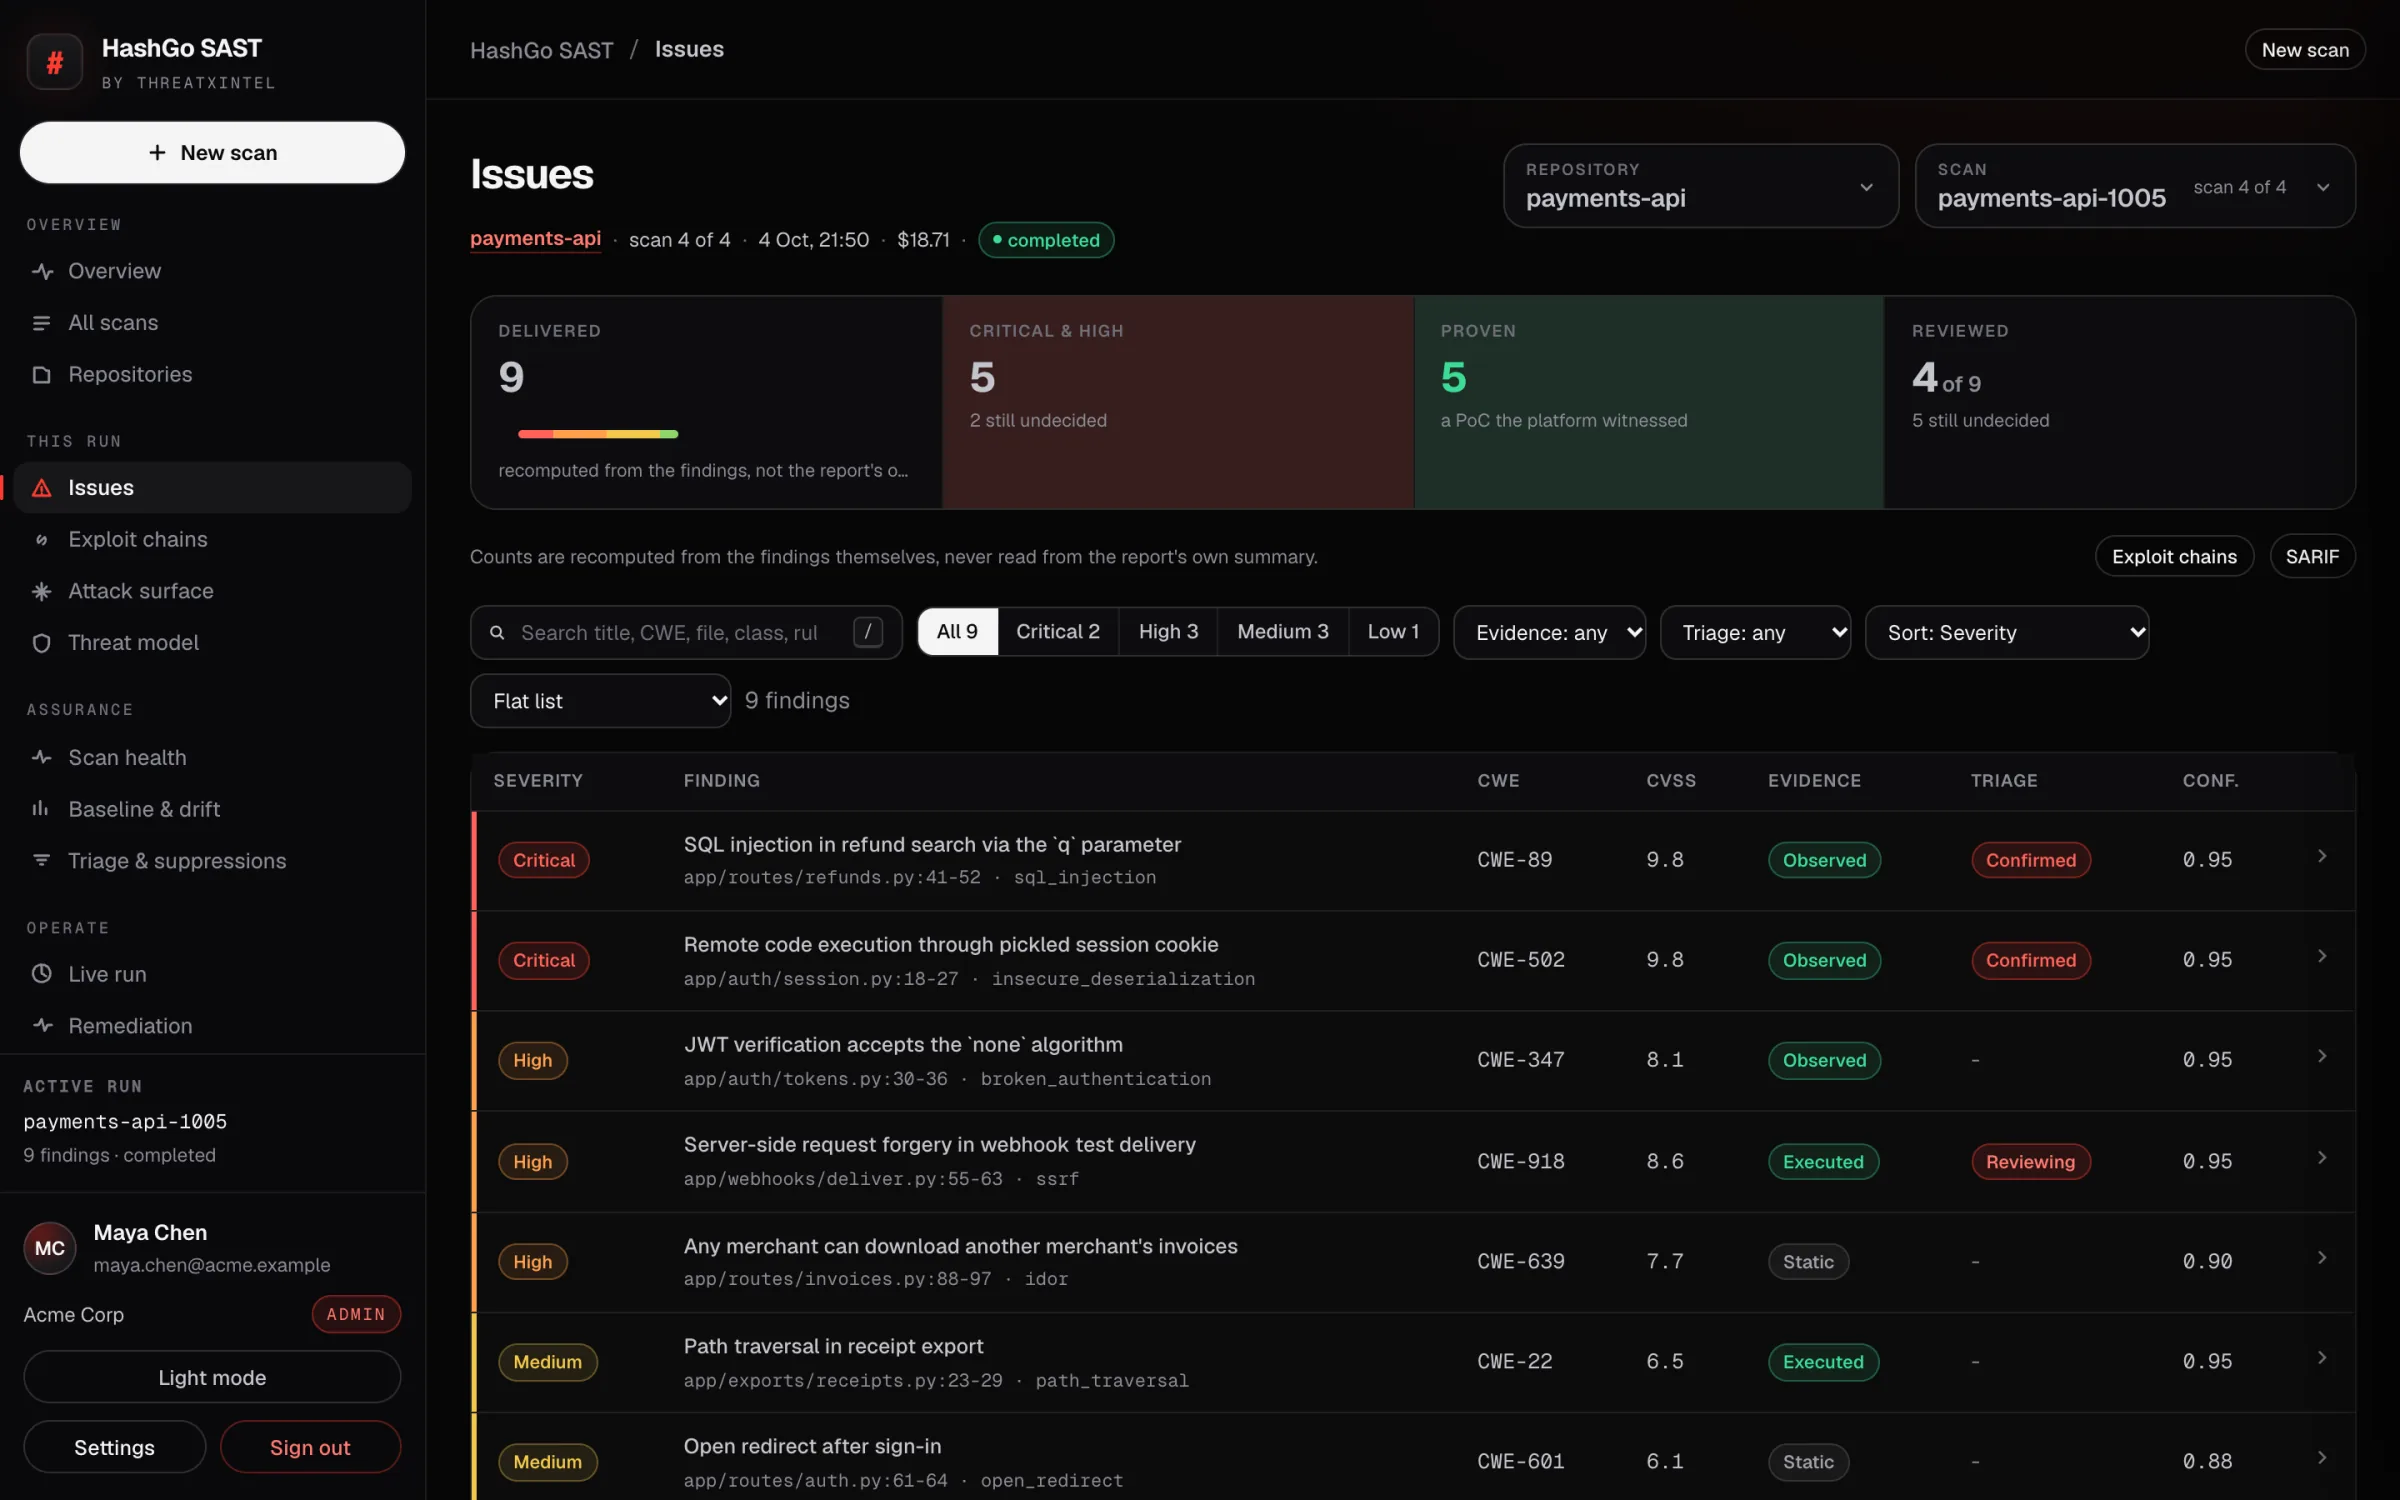
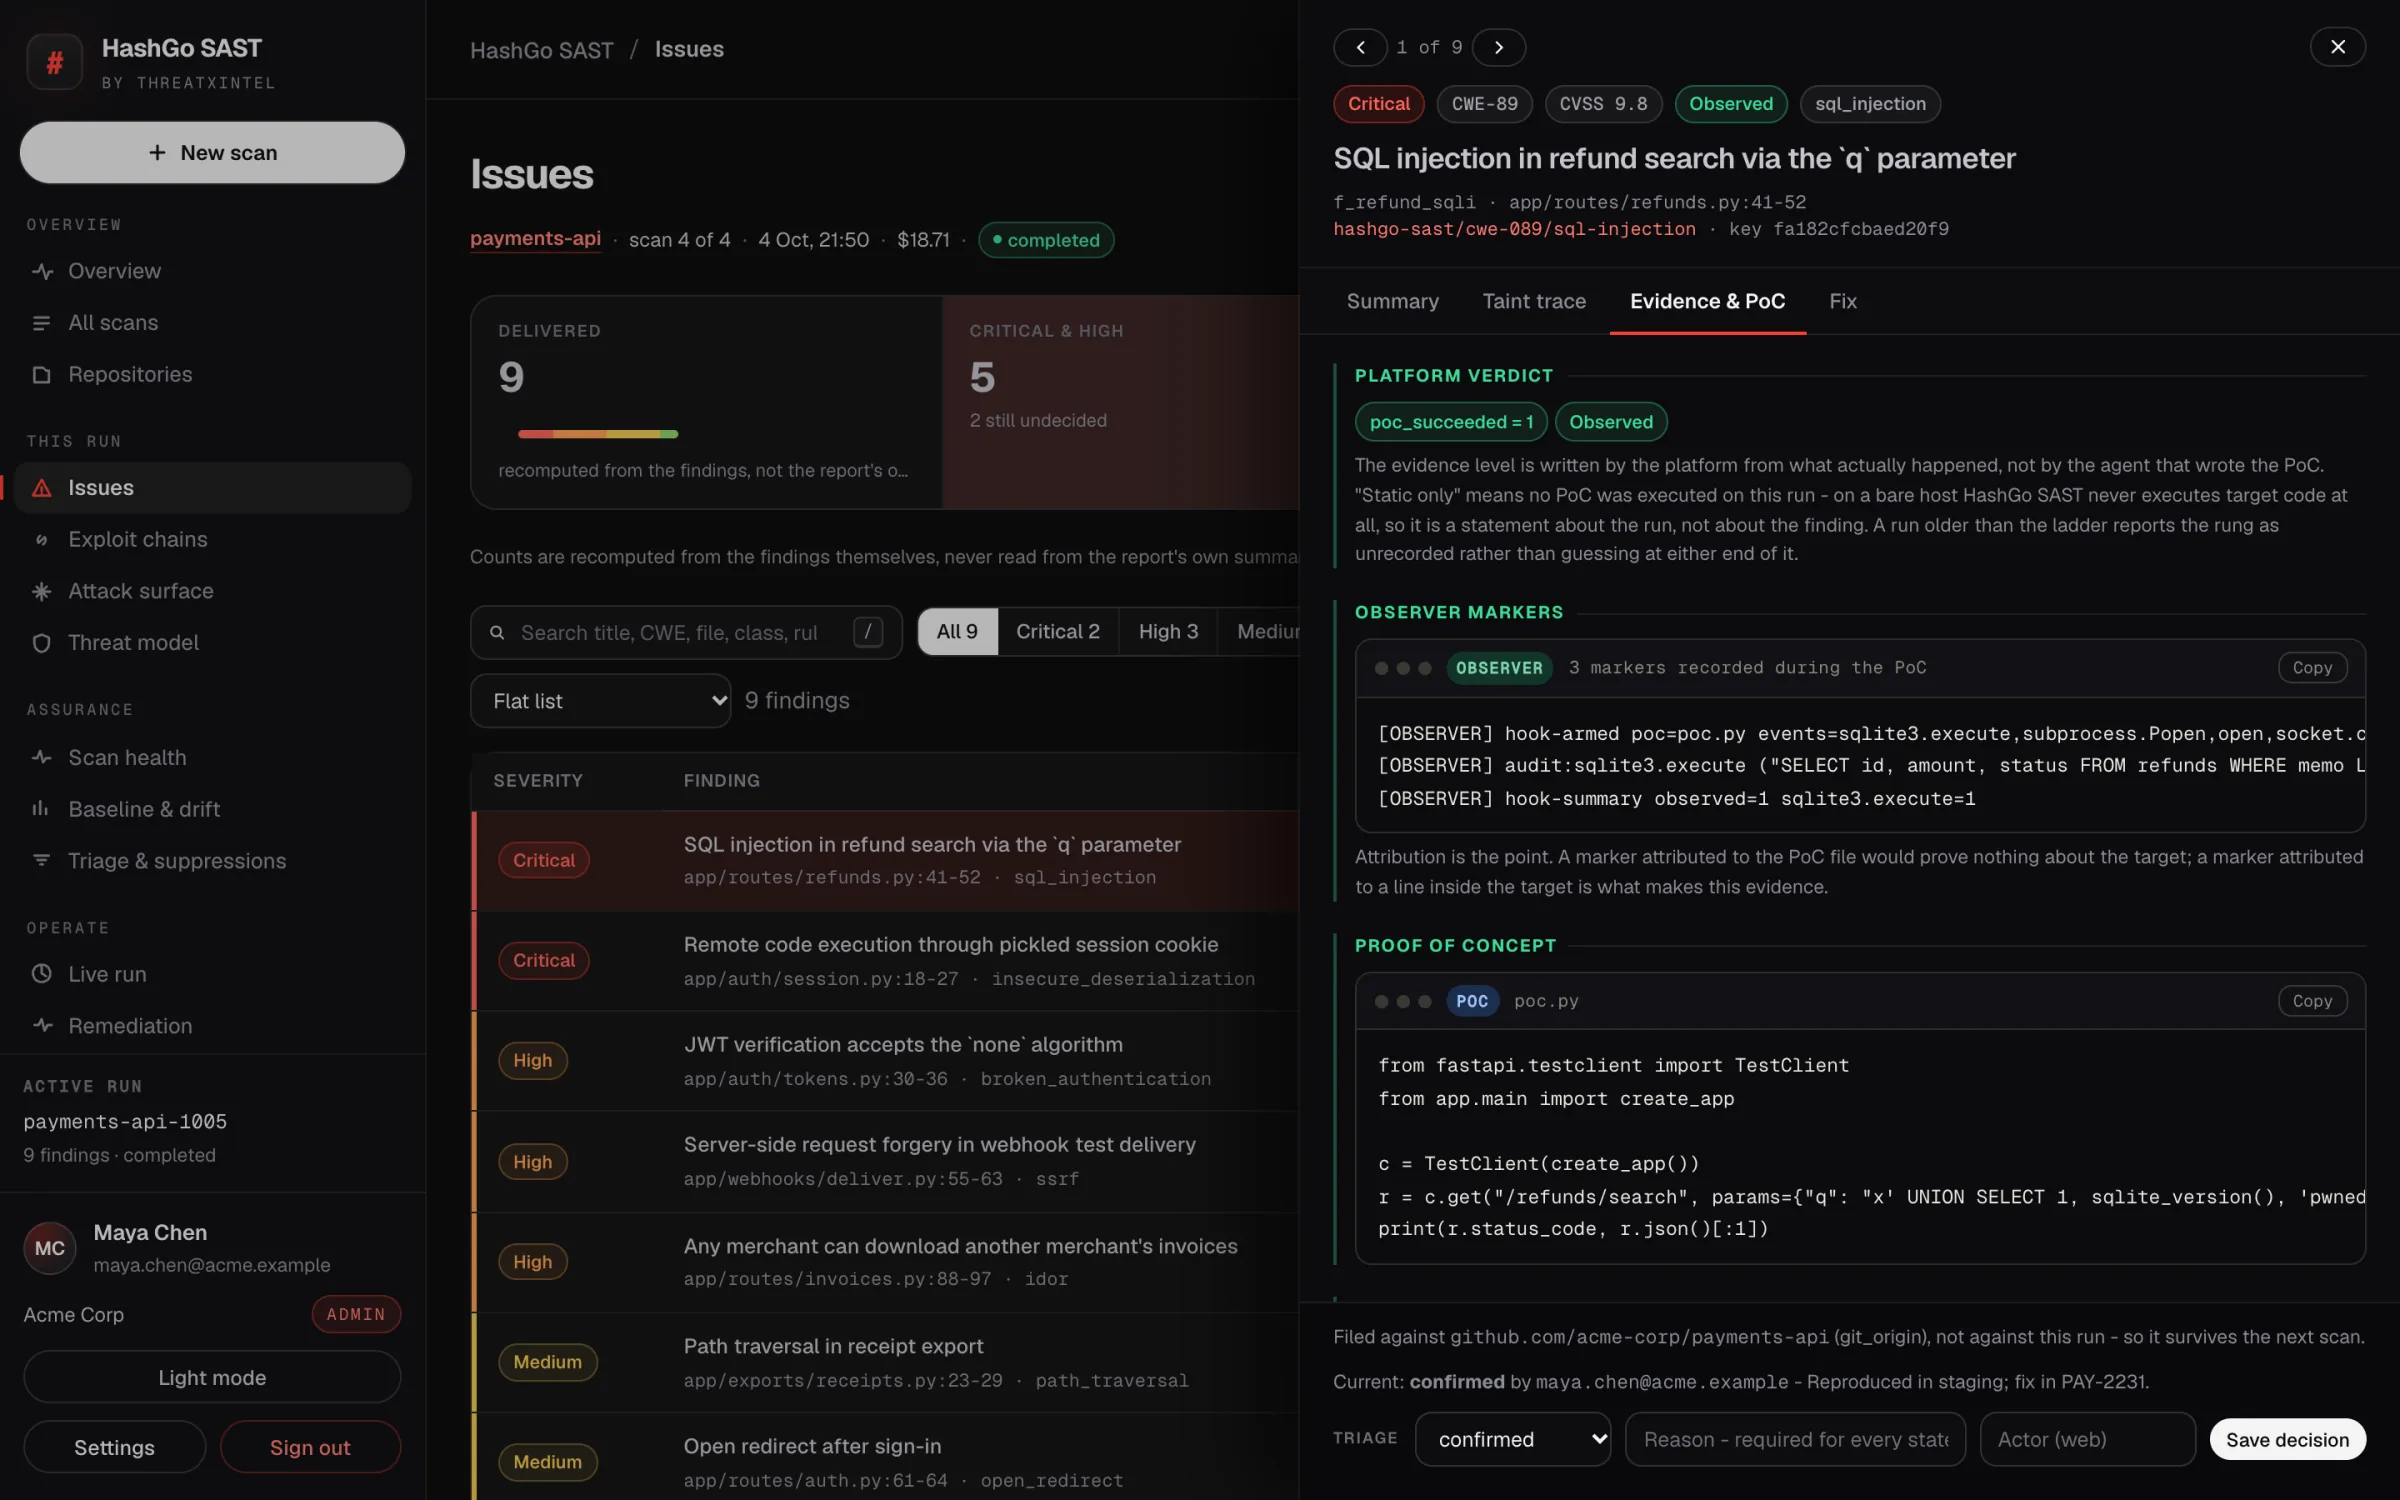
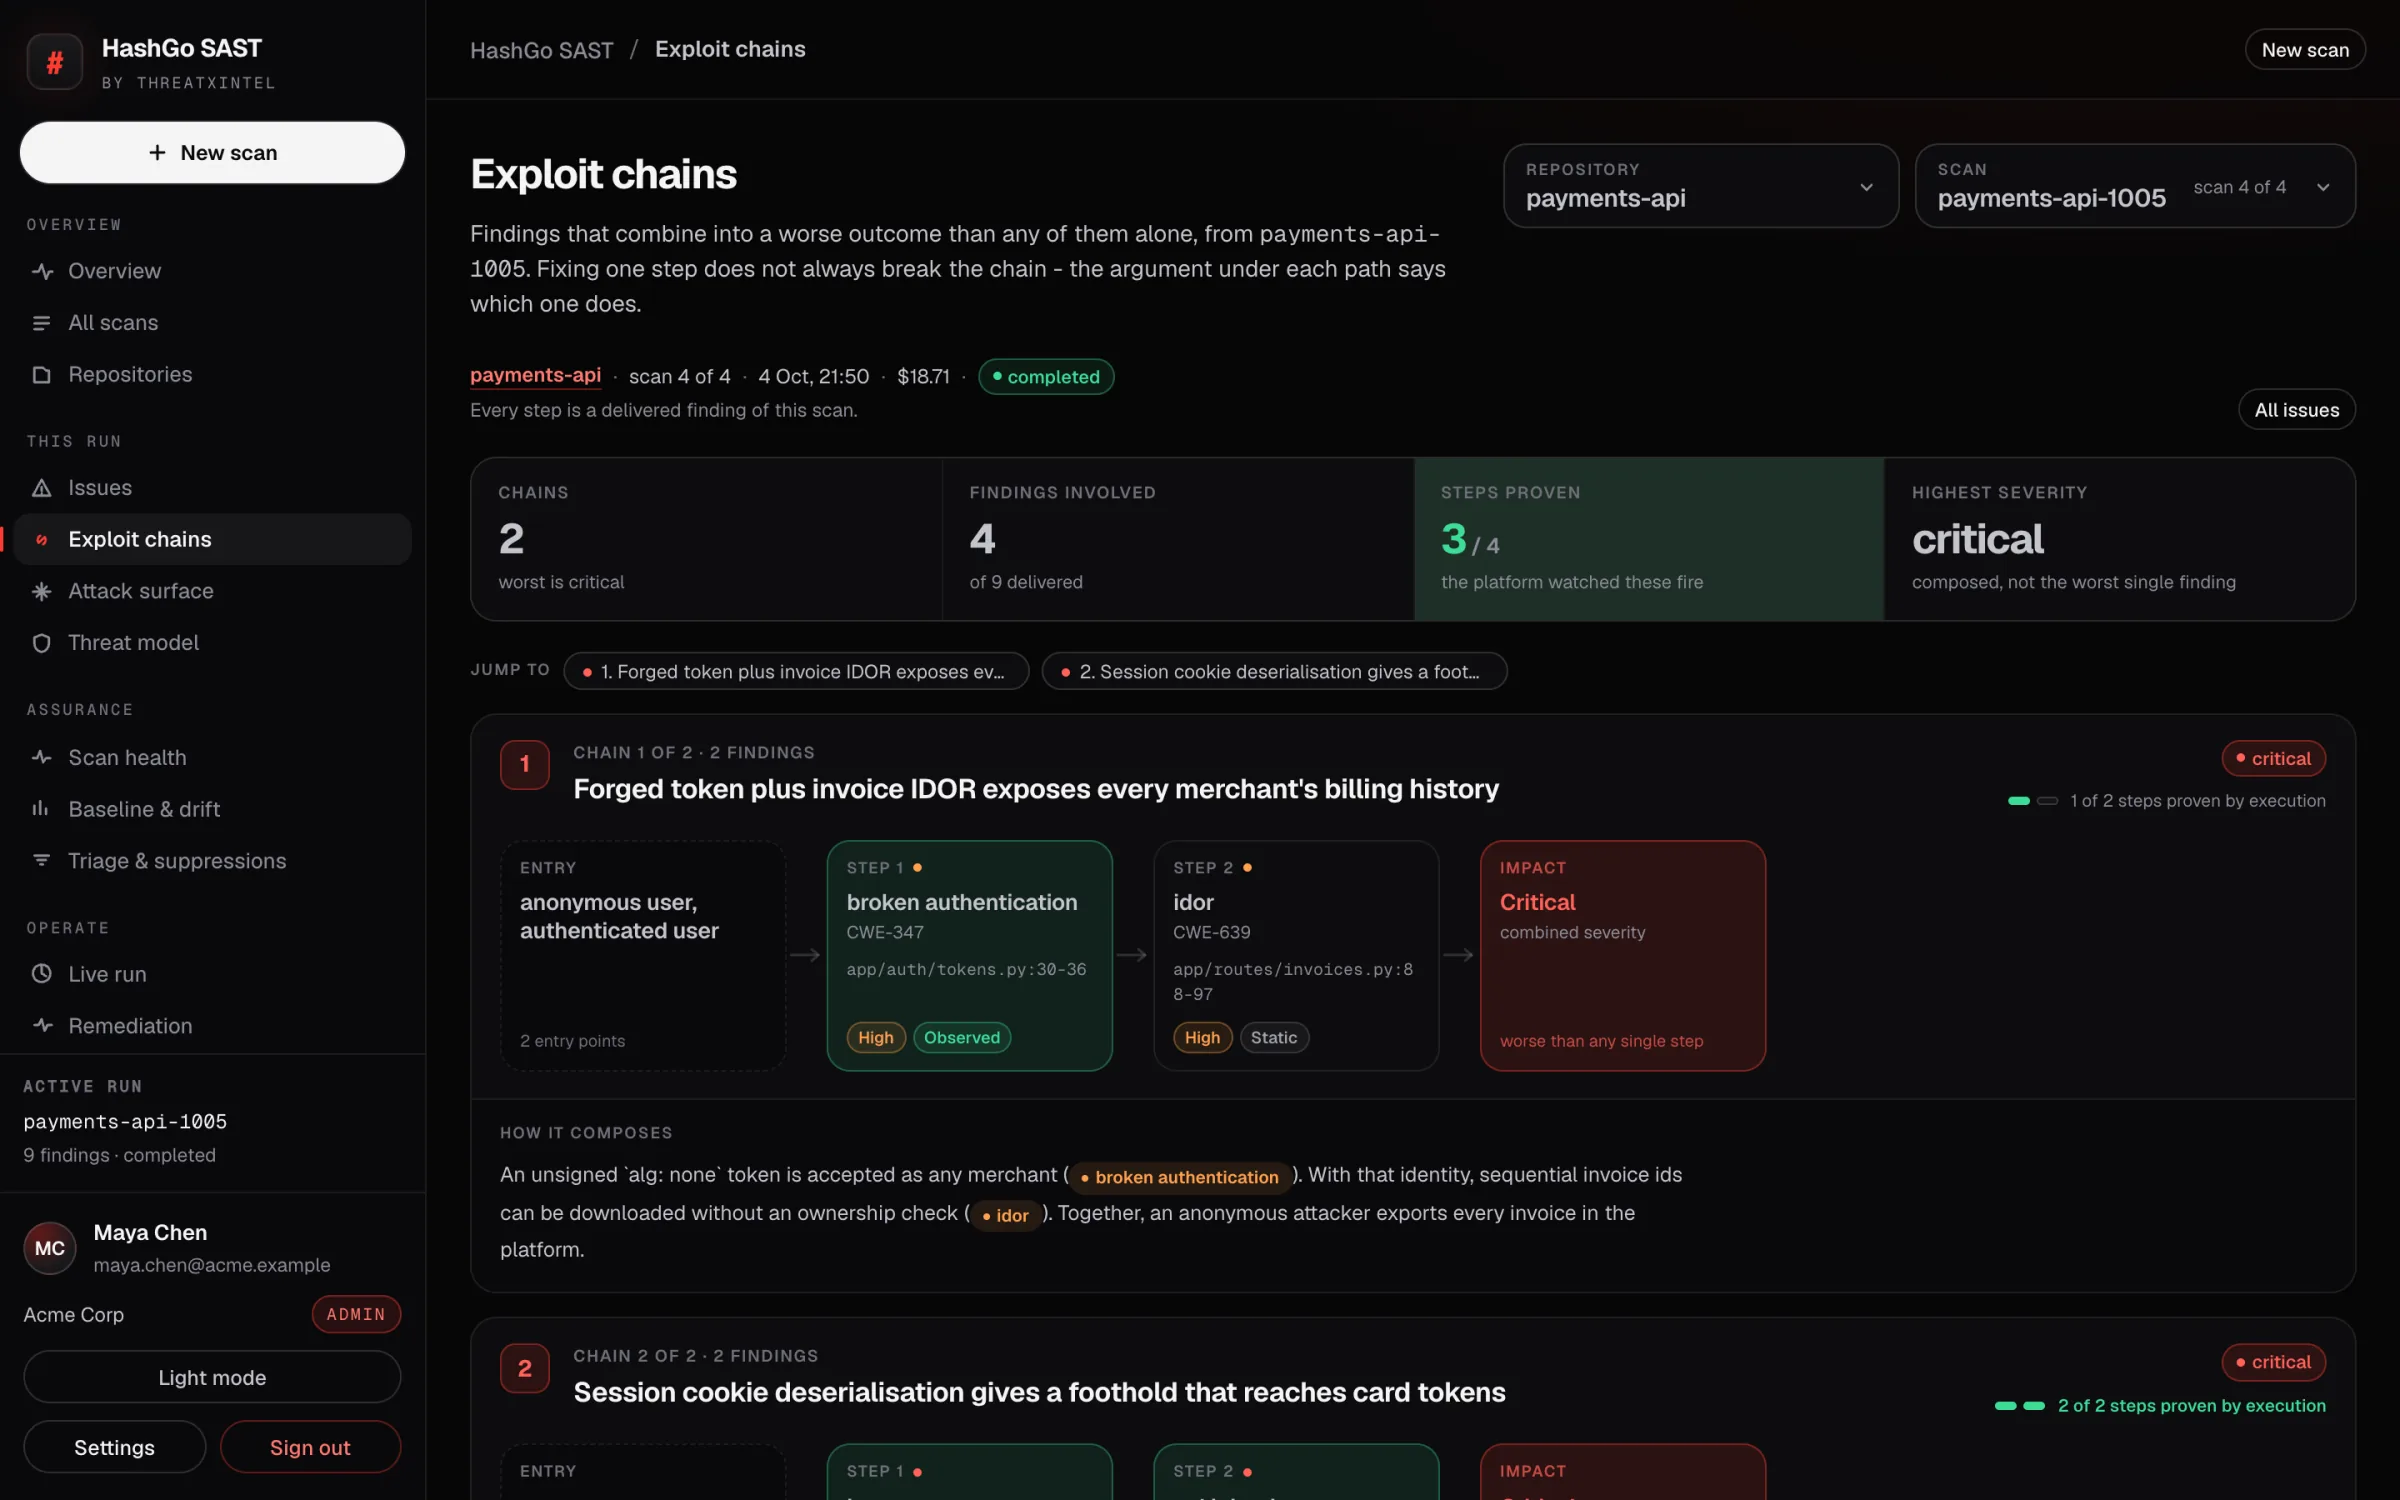
Screens from the live platform, shown with sample data from a fictional company.
Capabilities
Source analysis on every pull request, with data-flow checks and fix guidance at the exact line.
Findings arrive where code is reviewed, while the change is still fresh.
Fewer alerts, each one worth reading.
Start with built-in coverage, then teach it your own patterns.
How it works
Link your source control and choose the branches to scan.
Each pull request is checked before it merges.
Reachable, high-risk findings rise to the top.
Apply the guidance and confirm the finding is closed.
Coverage
SAST and DAST
HashGo SAST reads the code. HashGo DAST tests what is deployed. Most teams need both.
| HashGo SAST | HashGo DAST | |
|---|---|---|
| What it examines | Source code, without running it | The running application, from the outside |
| When it runs | On pull requests and in CI | Against staging or production |
| Typical findings | Injection, unsafe input handling, hardcoded secrets | Auth and session flaws, runtime injection, misconfiguration |
| Needs a deployed app | No | Yes |
Pricing
HashGo SAST finds vulnerabilities in your source code and proves which ones are exploitable. Pricing has two parts: a per-developer licence for the platform, and AI usage, which you pay through your own AI provider or through HashGo credits.
Prices are per contributing developer per month, billed yearly.
Trials and open source
₹0
$0
Startups and SMB teams
₹1,499/dev/month
$19/dev/month
SaaS, fintech, product companies
₹2,999/dev/month
$39/dev/month
Teams wanting one predictable bill
₹5,999/dev/month
$69/dev/month
BFSI, defence, government, large enterprises
From₹25 lakh/year
From $30,000/year
Professional + AI includes every Professional feature.
| Feature | Free | Starter | Professional | Enterprise |
|---|---|---|---|---|
| Scanning | ||||
| AI static analysis, 35+ languages, IaC, web templates | Included | Included | Included | Included |
| Independent AI validation + reachability tracing | Included | Included | Included | Included |
| Secrets scanning (code and Git history) | Included | Included | Included | Included |
| Open-source dependency scanning (SCA) with reachability | Not included | Included | Included | Included |
| SBOM export (CycloneDX / SPDX) | Not included | Included | Included | Included |
| API spec scanning (OpenAPI / Swagger) | Not included | Not included | Included | Included |
| Salesforce Apex, Visualforce, Aura | Not included | Not included | Included | Included |
| COBOL, JCL, ABAP, PL/SQL, mainframe | Not included | Not included | Not included | Included |
| Scans per month | 20 | Unlimited (fair use) | Unlimited (fair use) | Unlimited |
| Proof and fixes | ||||
| Executed proof-of-concept in an isolated sandbox | Not included | Not included | Included | Included |
| Evidence levels on every finding (Observed to Not attempted) | Included | Included | Included | Included |
| Attack chains + threat model | Not included | Not included | Included | Included |
| AI fix patches | Not included | Included | Included | Included |
| Test-verified fixes + one-click pull request | Not included | Not included | Included | Included |
| AI chat on findings | Not included | Included | Included | Included |
| Developer workflow | ||||
| GitHub, GitLab, Bitbucket, Azure DevOps, self-hosted Git | Included | Included | Included | Included |
| CLI, zip upload, VS Code and JetBrains plugins | Included | Included | Included | Included |
| Fast pull-request scans, inline comments, build gating | Not included | Included | Included | Included |
| Jira, Slack, Microsoft Teams | Not included | Included | Included | Included |
| ServiceNow, Azure Boards (two-way sync) | Not included | Not included | Included | Included |
| SARIF 2.1.0, JSON, Markdown, HTML, PDF reports | Included | Included | Included | Included |
| Compliance and reporting | ||||
| OWASP Top 10, CWE and CVSS 3.1 on every finding | Included | Included | Included | Included |
| PCI DSS 4.0, ISO 27001, OWASP ASVS, SANS 25 mapping | Not included | Not included | Included | Included |
| RBI, SEBI CSCRF, CERT-In, SAMA, NCA ECC, UAE IA mapping | Not included | Not included | Included | Included |
| Audit mode: pinned model, signed and hashed reports | Not included | Not included | Included | Included |
| Executive dashboard: risk trend, time to fix, SLA | Not included | Not included | Included | Included |
| Hand-off to DAST and manual penetration testing | Not included | Not included | Included | Included |
| White-label reports | Not included | Not included | Not included | Included |
| Security and deployment | ||||
| Email sign-in with two-factor authentication, roles | Included | Included | Included | Included |
| Audit log | Not included | Not included | Included | Included |
| Single sign-on (OIDC, SAML) and just-in-time provisioning | Not included | Not included | Not included | Included |
| Private or self-hosted AI model | Not included | Not included | Not included | Included |
| India, UAE or KSA data region | Not included | Not included | Not included | Included |
| On-premises / air-gapped installation | Not included | Not included | Not included | Add-on |
| Support | Community | Email, next business day | Priority, business hours IST / GST | 24x7, named manager, 99.9% uptime SLA |
AI usage
HashGo SAST uses AI models to read, test and validate your code, and each scan consumes model tokens.
| Option | How it works | Price |
|---|---|---|
| Bring your own key | Connect your Anthropic, Amazon Bedrock, Google Vertex AI or Microsoft Foundry account. Your provider bills you directly. | Licence only |
| HashGo credits | Prepaid credits; 1 credit = $1 of model usage at the provider's list price. | ₹120 / $1.25 per credit |
| Professional + AI | Professional plan with 25 credits per developer per month, pooled across your team. | ₹5,999 / $69 per developer per month |
| Pack | Credits | India (INR) | International (USD) | Saving |
|---|---|---|---|---|
| Small | 100 | ₹12,000 | $125 | None |
| Medium | 500 | ₹57,000 | $595 | 5% |
| Large | 2,000 | ₹2,16,000 | $2,250 | 10% |
| Scan type | Code size | Typical credits per scan |
|---|---|---|
| Pull-request scan | Under 500 changed lines | 0.5 |
| Full scan, small application | Under 50,000 lines | 5 |
| Full scan, medium application | 50,000 to 200,000 lines | 20 |
| Full scan, large application | 200,000 to 500,000 lines | 60 |
A typical developer uses about 18 credits a month: around 20 pull-request scans plus a share of weekly full scans. Actual usage depends on code size, language and the number of issues found, and is shown per scan in your portal.
Add-ons and services
| Add-on | India (INR) | International (USD) | What you get |
|---|---|---|---|
| On-premises / air-gapped installation | +30% on Enterprise licence + ₹3 lakh one-time | +30% on Enterprise licence + $4,000 one-time | Docker / Kubernetes install inside your network, offline updates |
| Application security assessment, up to 50,000 lines | ₹75,000 | $1,500 | One-time HashGo scan, expert review by ThreatXIntel, report and one retest |
| Application security assessment, 50,000 to 200,000 lines | ₹1.5 lakh | $3,000 | Same scope |
| Application security assessment, 200,000 to 500,000 lines | ₹2.5 lakh | $5,000 | Same scope; larger applications quoted |
| Secure-coding workshop (per day) | ₹50,000 | $750 | Training built on your own findings |
| Onboarding and CI/CD setup | Free on Professional and Enterprise | Free on Professional and Enterprise | Guided setup of repositories, pipelines and integrations |
Partners (MSSPs, VAPT firms, resellers): 30% off list price, rising to 40% at 100 or more committed developers, with white-label reports included.
Discounts and terms
| Offer | Discount | Applies to |
|---|---|---|
| Launch offer | 30% off the first year | First 20 paying customers who agree to a published case study; ends 31 Dec 2026 |
| Multi-year | 10% off for 2 years; 15% off for 3 years | All paid plans, billed yearly |
| Volume | 10% off for 50 to 99 developers; 15% off for 100+ | Starter, Professional, Professional + AI |
| Startups | 50% off Starter for the first year | Companies under 2 years old with fewer than 20 developers |
| Education and non-profit | Starter free | Verified institutions and registered non-profits |
Discounts do not combine, except multi-year with volume.
| Term | Detail |
|---|---|
| Free trial | 14 days of Professional on 2 repositories, no card required |
| Billing cycle | Yearly in advance by default; monthly available at +20% |
| Adding developers | Added developers are billed pro rata for the rest of the term |
| Payment in India | Bank transfer, UPI or card, with a GST tax invoice |
| International payment | Wire transfer or card in USD |
| Enterprise payment terms | Net 30 days from invoice |
| Renewal | Price increase capped at 7% a year |
| Billing entity | Threatxintel Cyber Labs LLP, Bengaluru, India |
Sales and Enterprise quotes: info@threatxintel.com
Prices are valid from 7 October 2026 and may change with notice. Existing customers keep their price until renewal.
Static application security testing examines source code without executing it, looking for flaws such as injection, unsafe handling of input and hardcoded secrets.
SQL injection, cross-site scripting, hardcoded credentials, insecure deserialisation, weak cryptography and broken authentication logic, among others.
On every pull request for fast feedback, and in the pipeline for a full scan. Policies decide which findings fail a build and which are tracked.
SAST reads the code before it runs. DAST tests the running application from the outside. Together they cover what each misses alone.
Anyone who committed code to a scanned repository in the last 90 days. Viewers, managers and auditors are free.
Scan cost depends on the size of your code. Paying for usage means small teams do not subsidise large ones, and you can use AI credits you already have with your cloud provider.
On Free, Starter and Professional, code is sent to the AI provider you configure, under that provider's terms. On Enterprise, you can use a private or self-hosted model, an India, UAE or KSA data region, or a fully on-premises installation.
On Professional and Enterprise, HashGo builds your application in an isolated sandbox, runs a real proof-of-concept exploit and records the dangerous operation against the exact line of code. Each finding shows whether it was observed, executed or not attempted.
Yes. Upgrades take effect immediately and are charged pro rata. Downgrades take effect at renewal.
Purchased credit packs stay valid for 12 months. Credits included in Professional + AI reset each month.
Yes. Enterprise prospects get a guided 30-day proof of concept on their own repositories.
HashGo SAST is live. Sign in at hashgosast.threatxintel.ai, or book a demo and we will set up your organization.
Open the platform, or book a demo and we will set up your organization.


