HashGo · Brand protection

HashGo Brand Monitoring Live

Know when someone pretends to be you.

HashGo Brand Monitoring is a supervised team of AI agents that watches every place your brand can be copied or attacked: lookalike domains, phishing sites, social profiles, app stores, marketplaces, the dark web and the answers AI assistants give about you. It shows what it found and why, ranks what matters, and files the takedown once a person approves.

27threat classes, from lookalike domains to UPI fraud, each with its own autonomy rule
11agents under one supervisor, with every step and tool call recorded
68connectors for SIEM, SOAR, ticketing, block lists, chat and data warehouses

Product tour

Inside HashGo Brand Monitoring.

What your team sees after sign-in: findings ranked by risk, the evidence behind each one, and a person in front of every irreversible action. Click any screen to enlarge it.

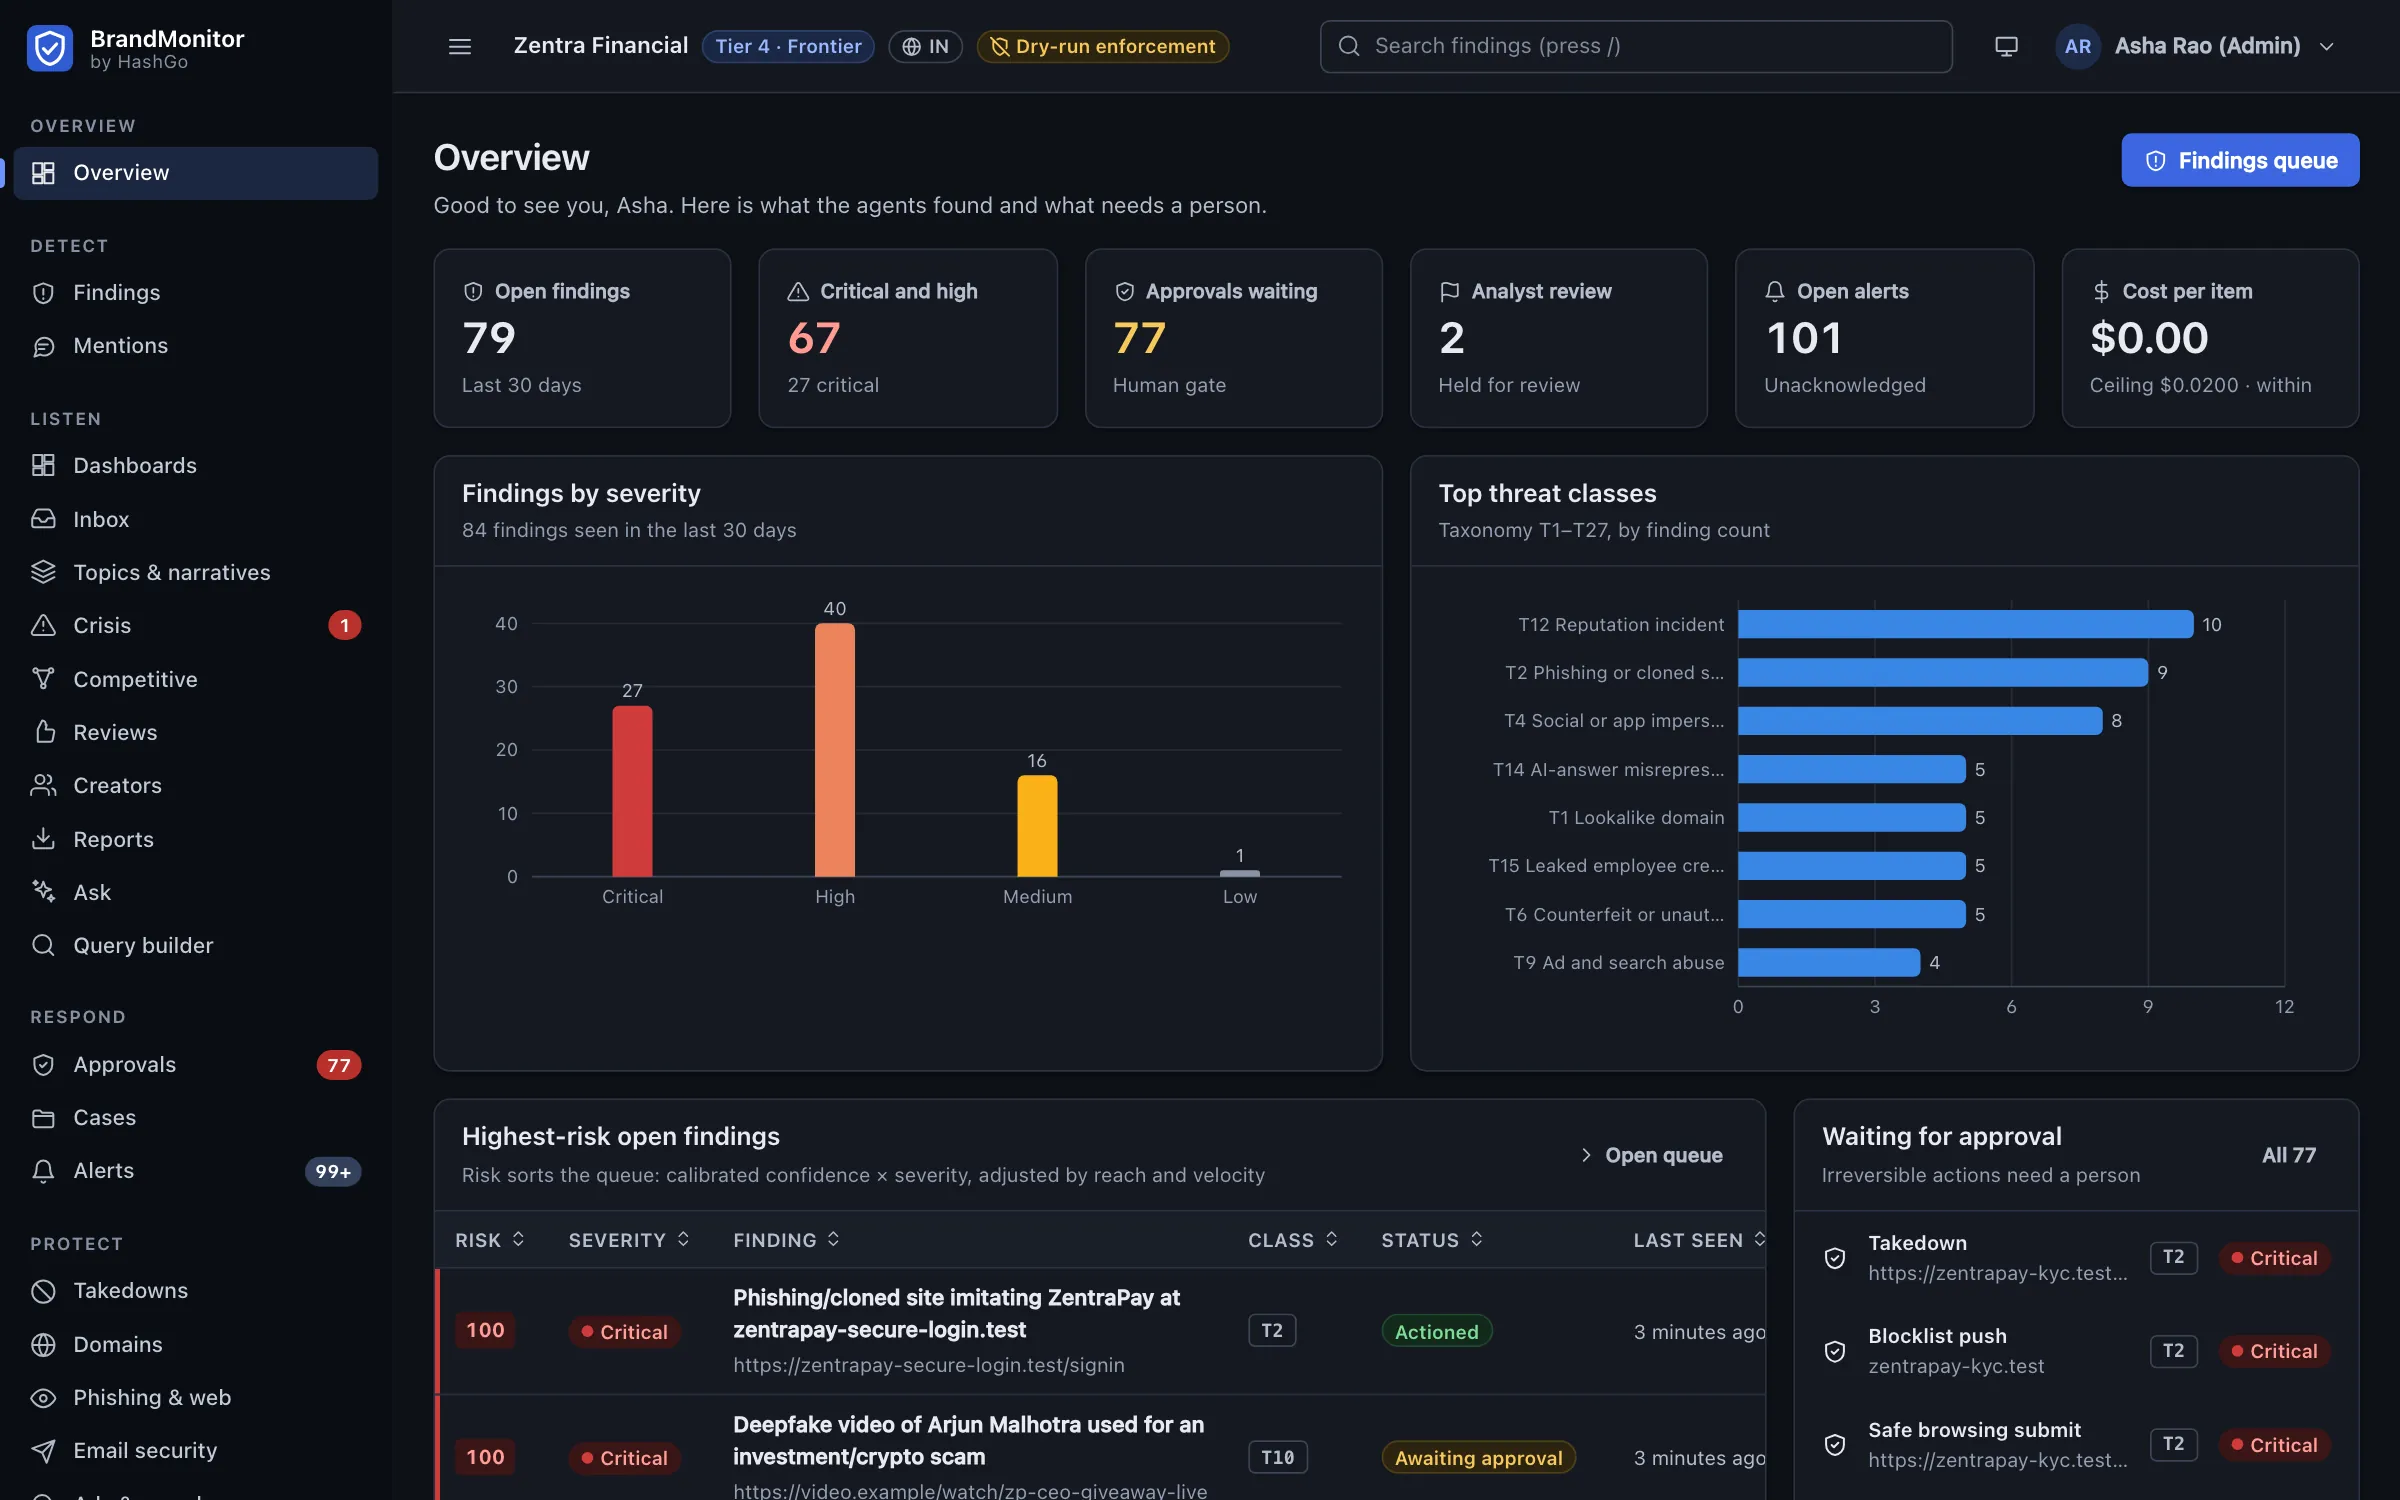
HashGo Brand Monitoring overview with open findings, critical and high counts, approvals waiting, findings by severity, top threat classes and the highest-risk open findings
Overview. Open findings by severity and threat class, the highest-risk items first, and what is waiting for a person.
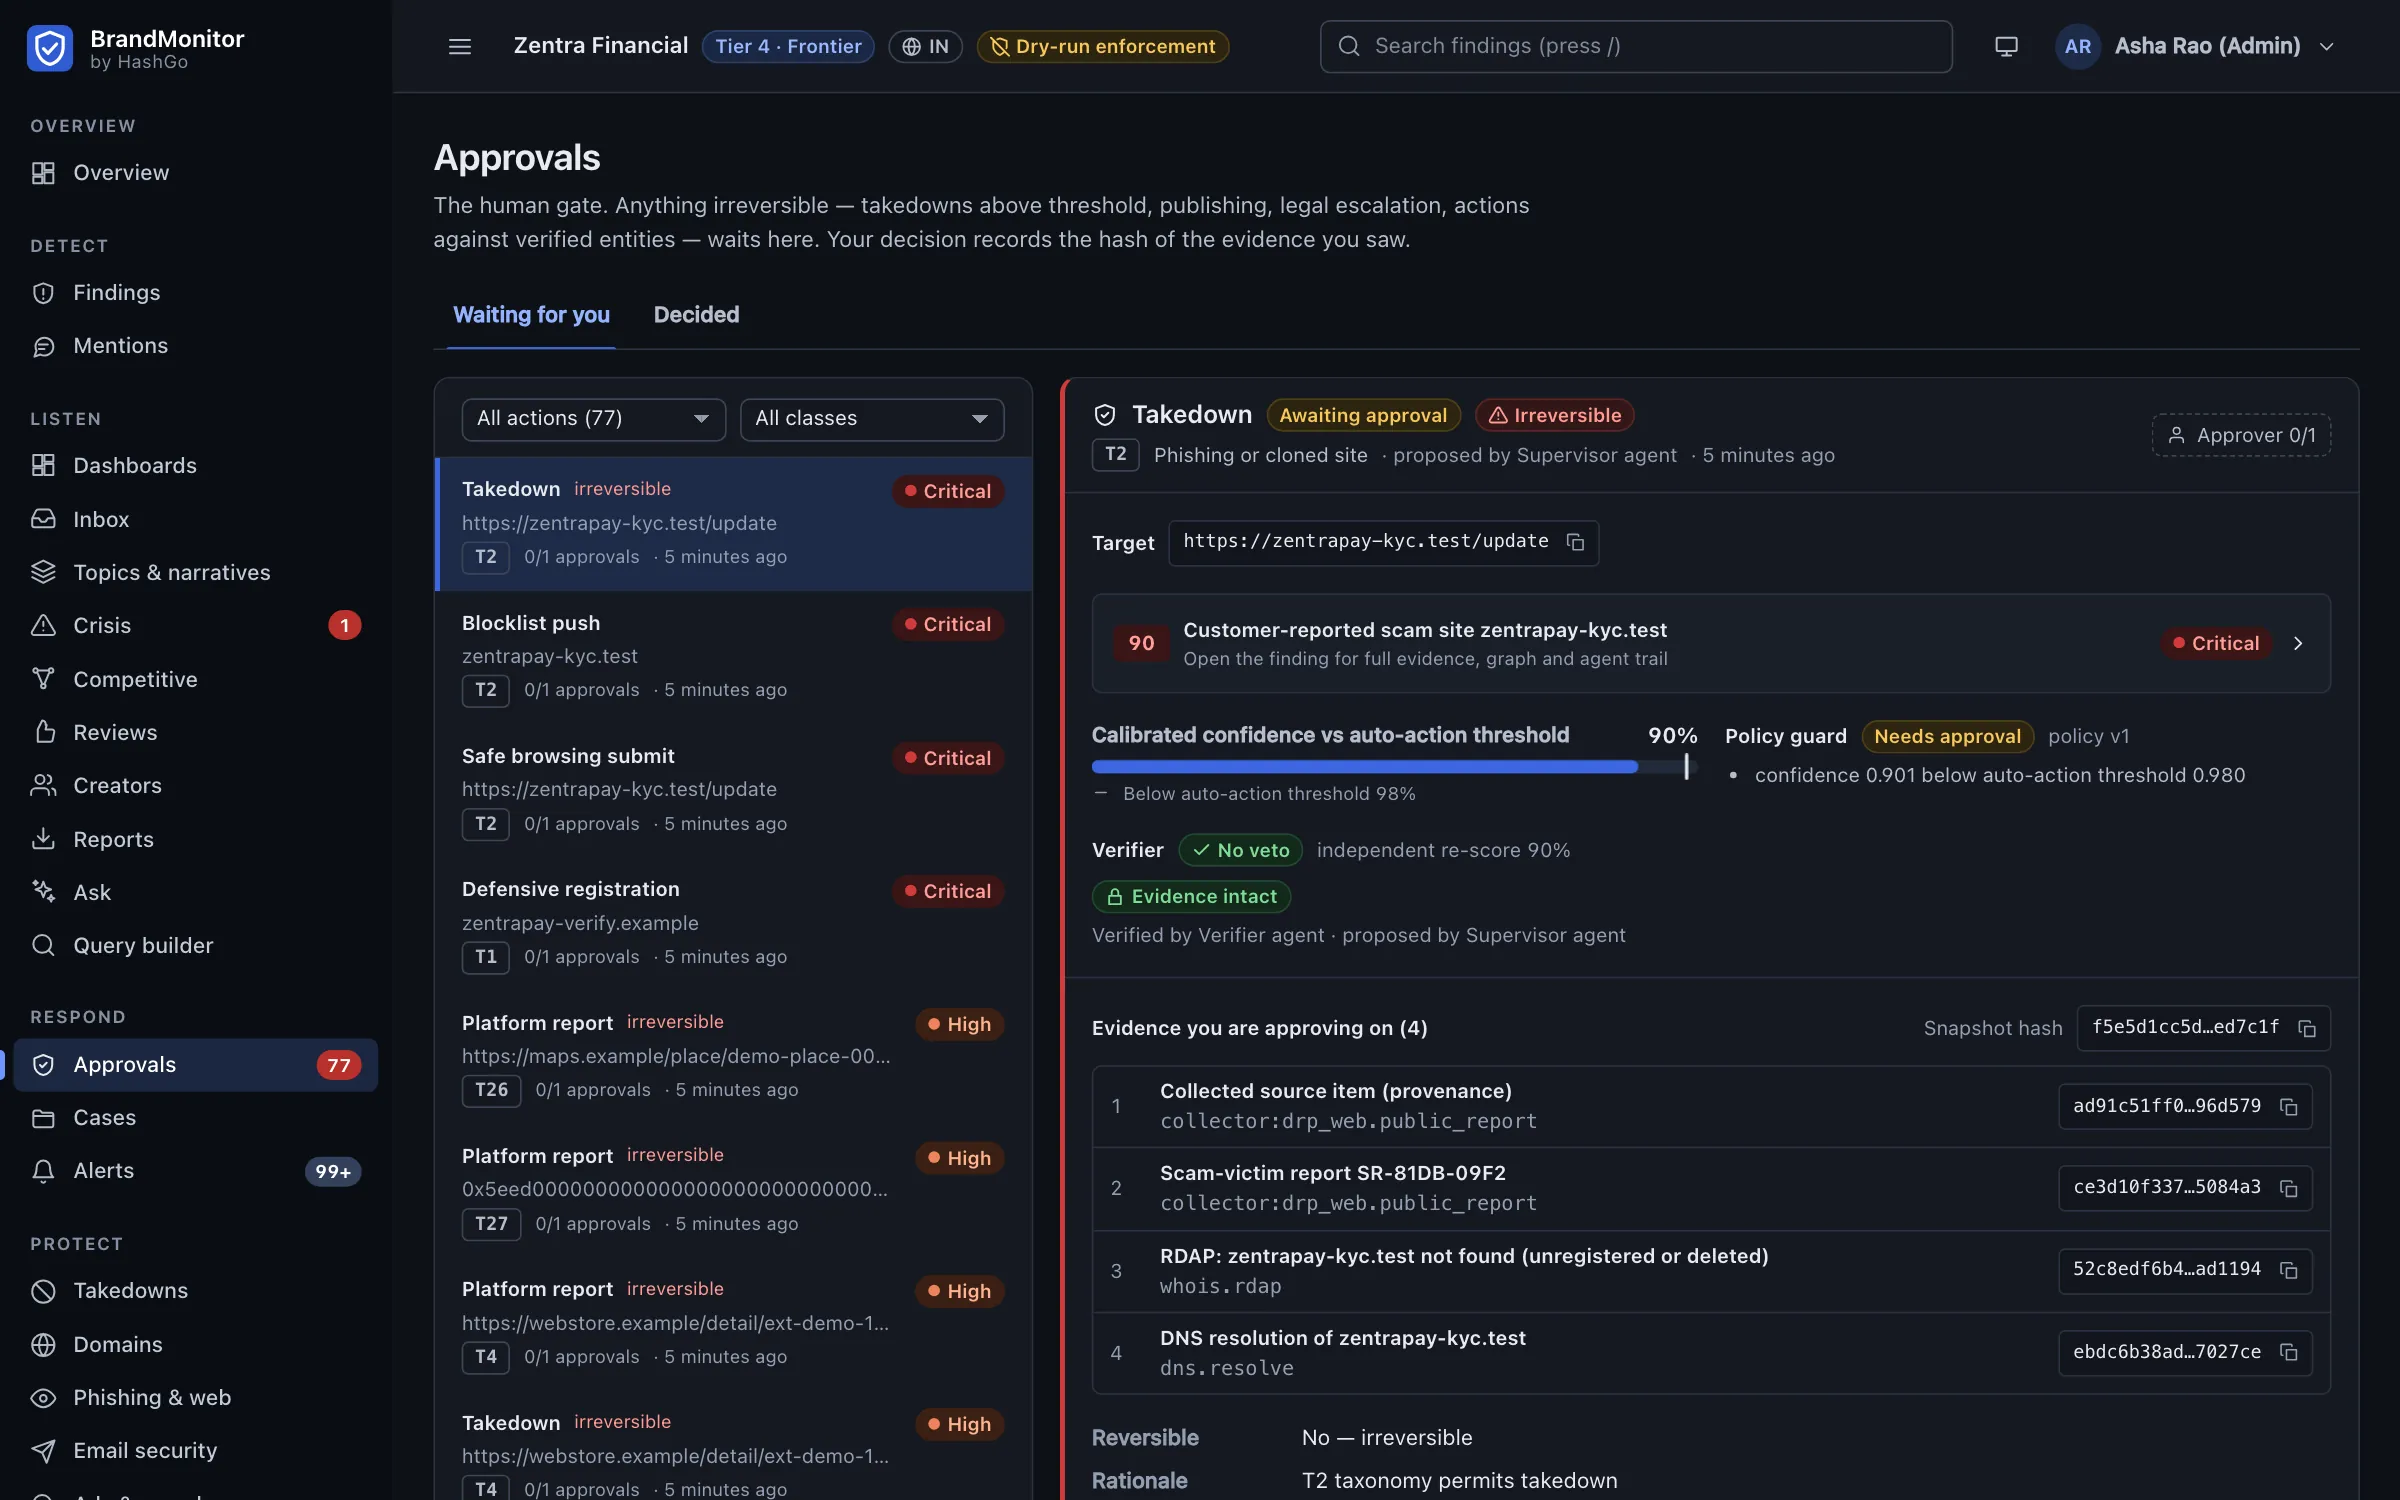
Approval queue with a takedown awaiting approval, calibrated confidence against the auto-action threshold, the policy guard decision, the verifier result and hashed evidence items
Approvals. Irreversible actions wait for a named approver, with the confidence, the policy decision and a hash of every piece of evidence.
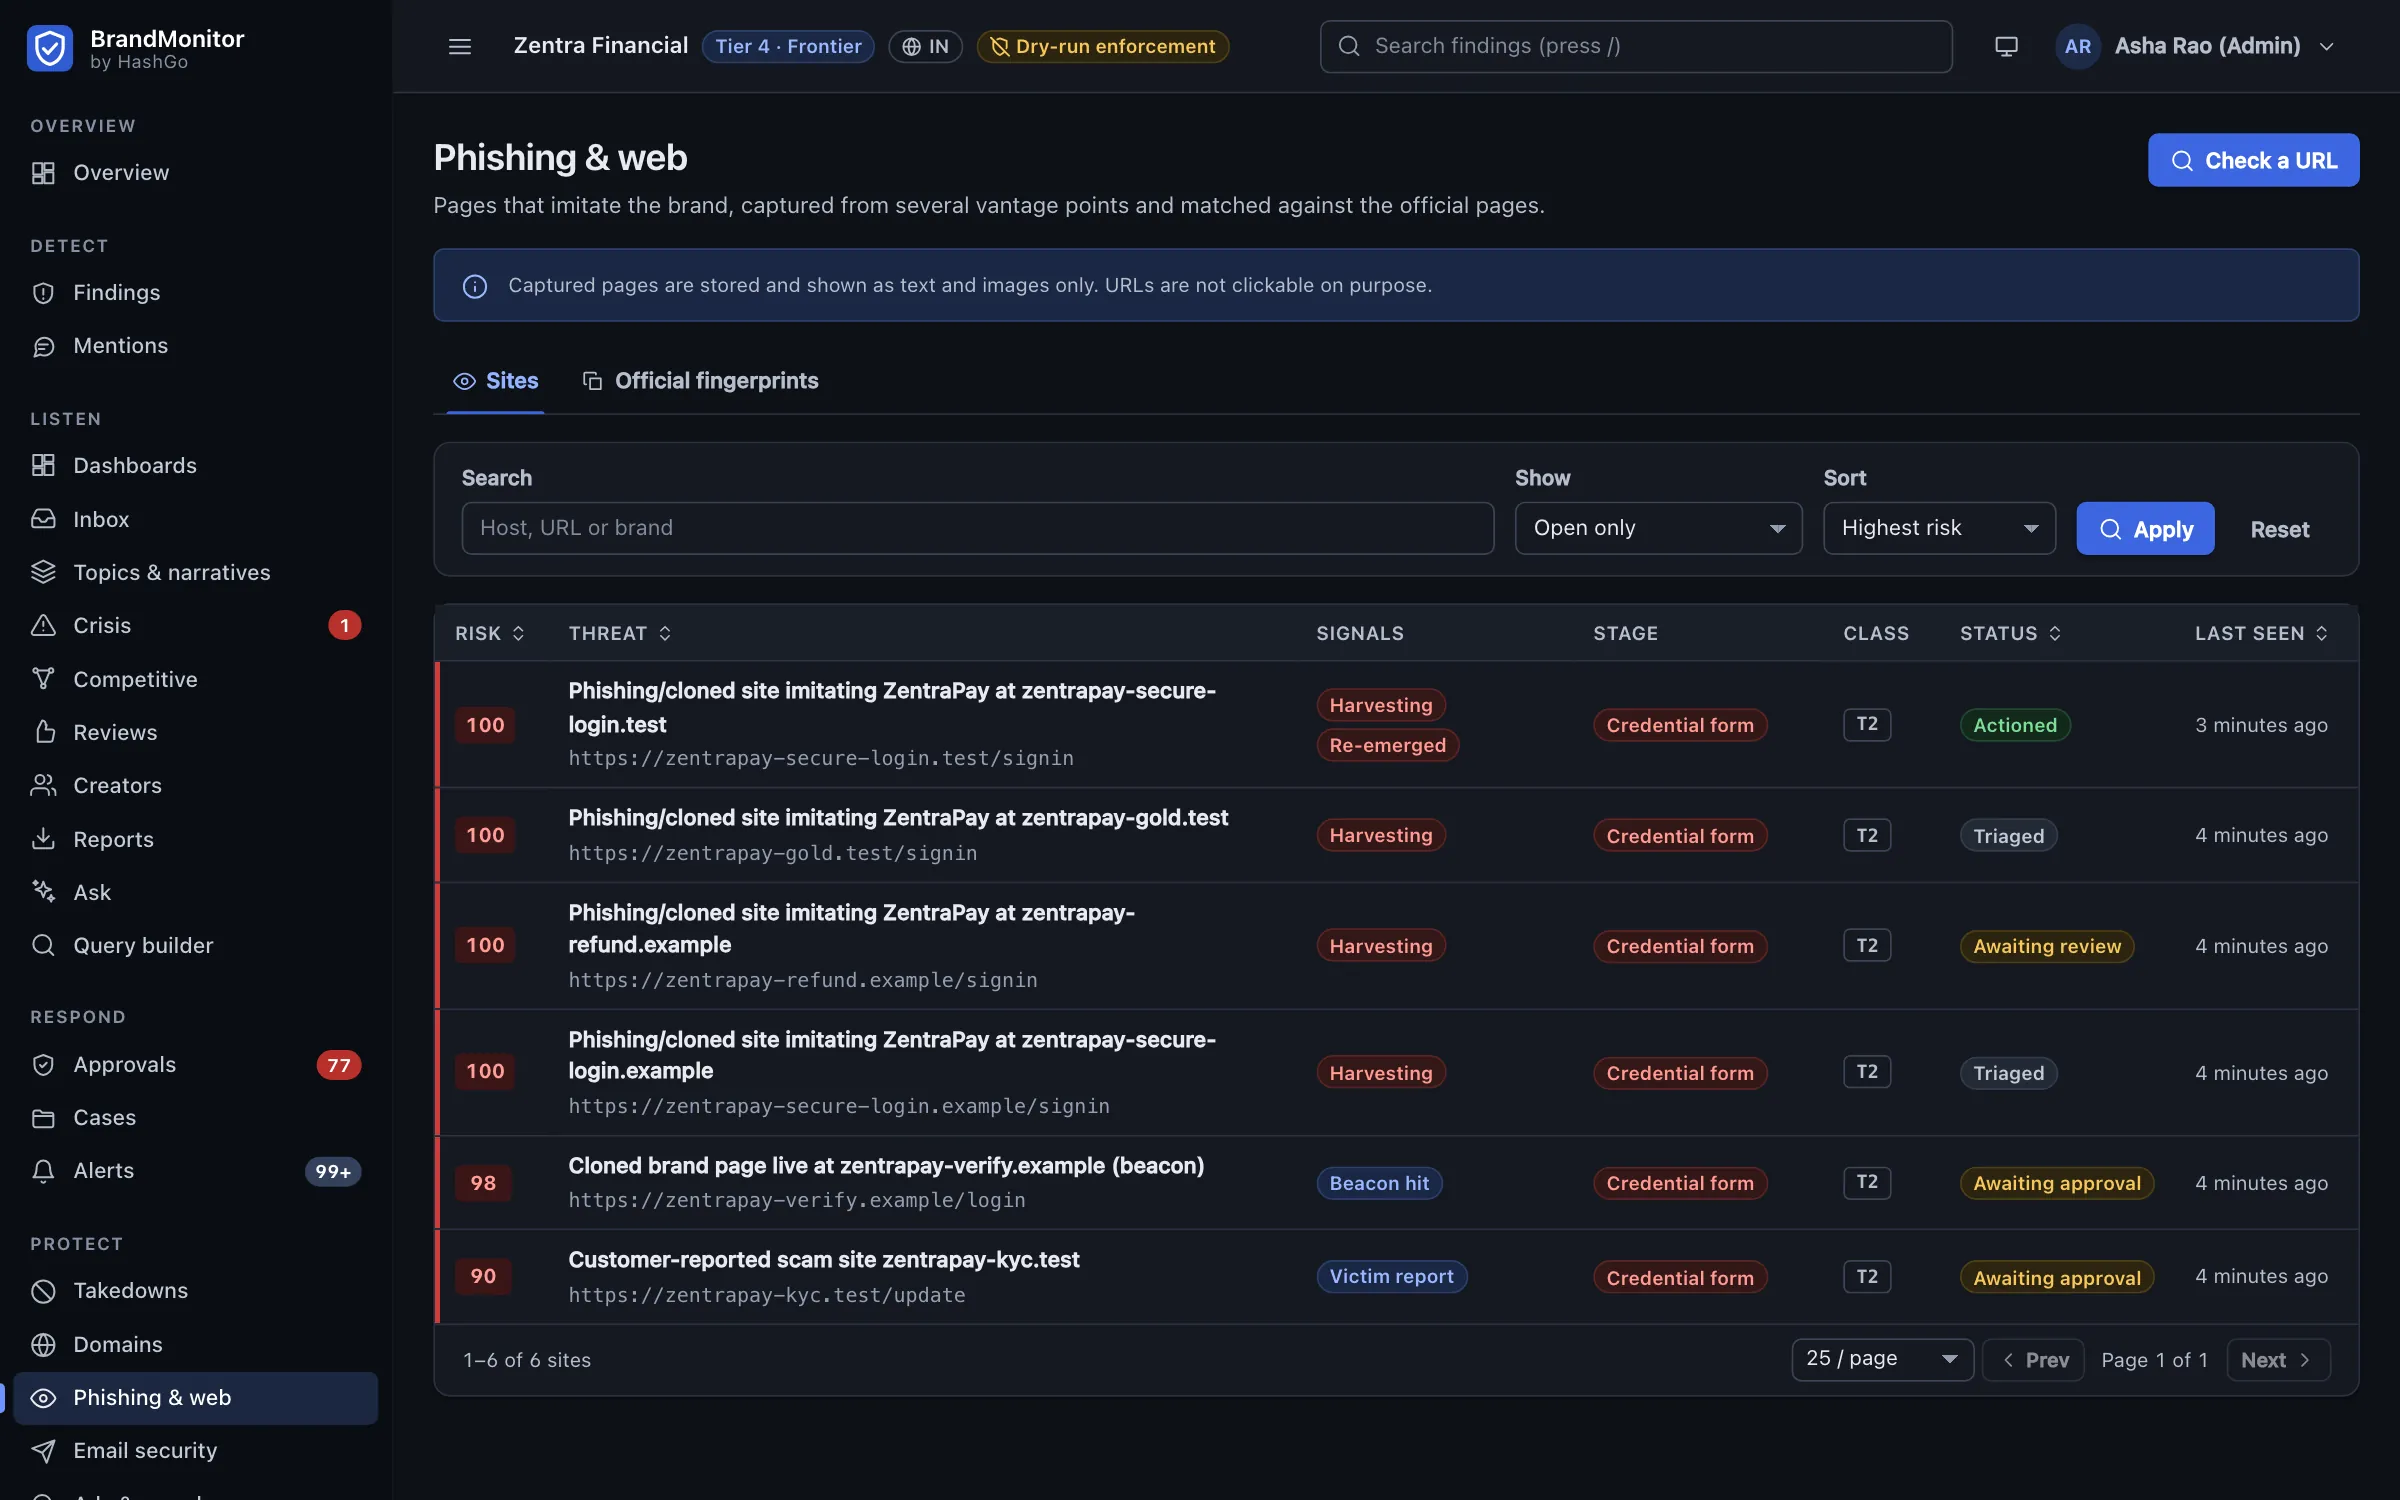
Phishing and web view listing cloned sites ranked by risk, with harvesting and re-emergence signals, the credential-form stage and status
Phishing and web. Cloned pages captured from several vantage points and matched against your official pages.
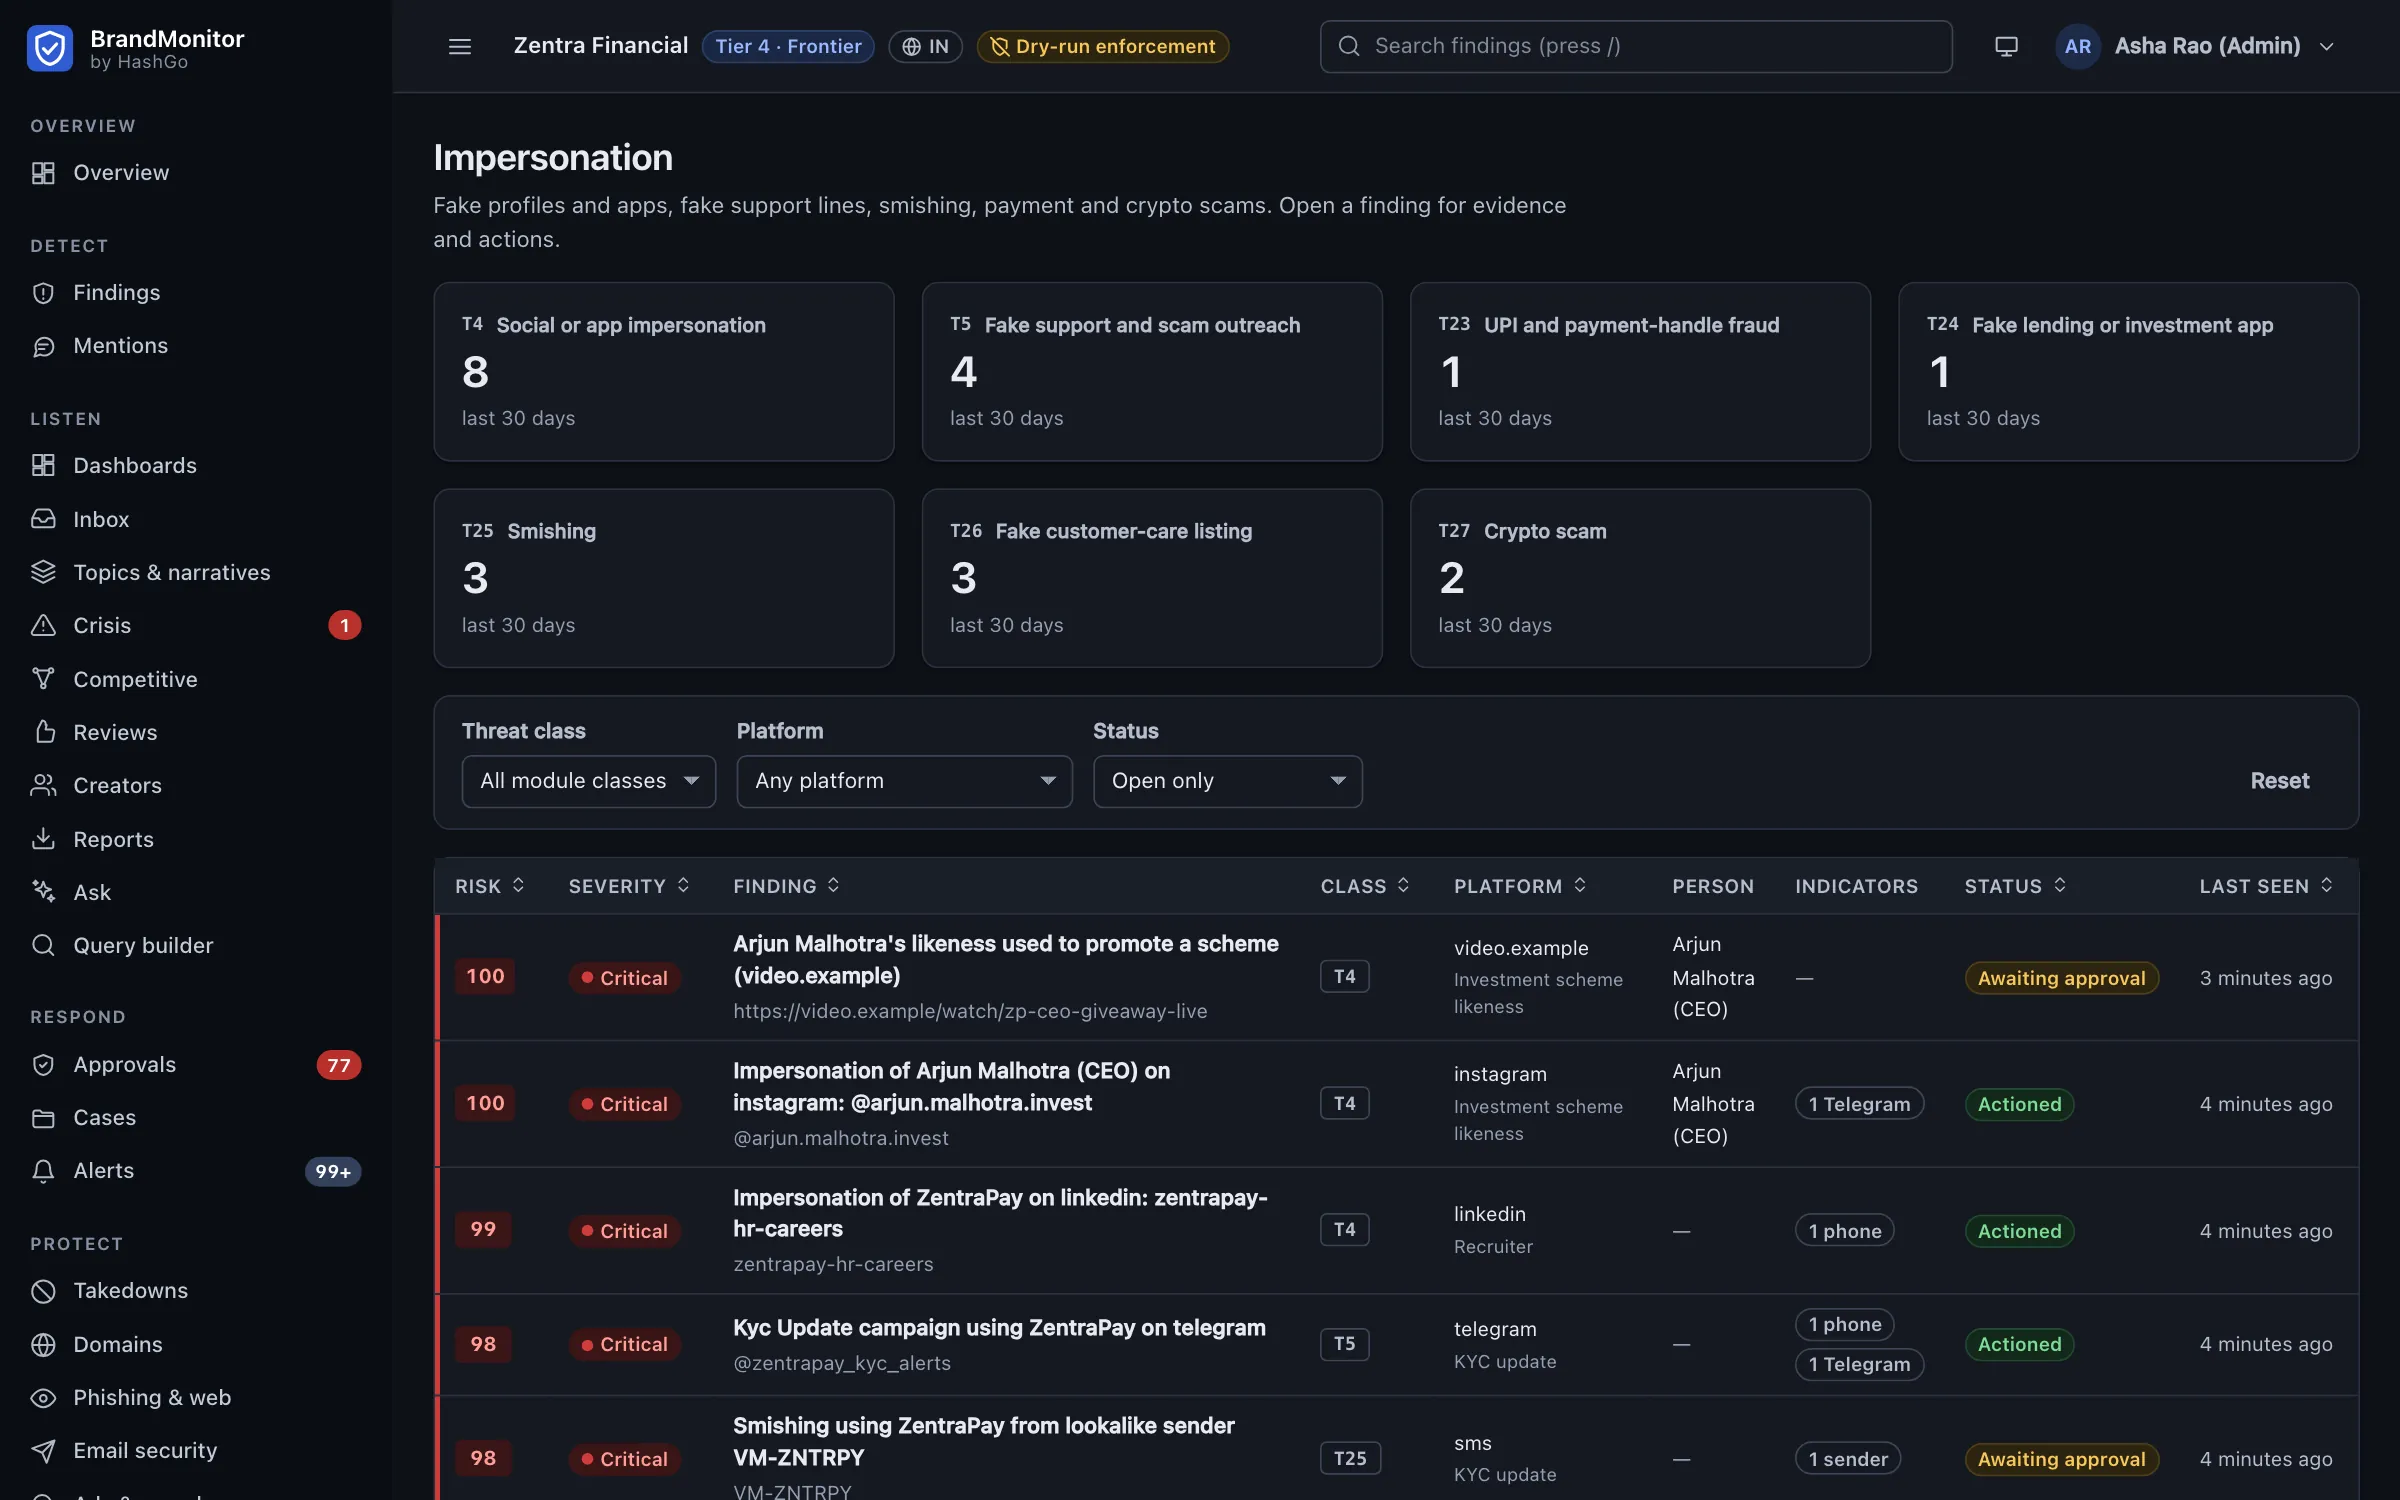
Impersonation view with counts for social and app impersonation, fake support, UPI fraud, fake lending apps, smishing, fake customer-care listings and crypto scams, above a list of findings by platform
Impersonation. Fake profiles, support lines, smishing senders, UPI and crypto scams, by threat class and platform.
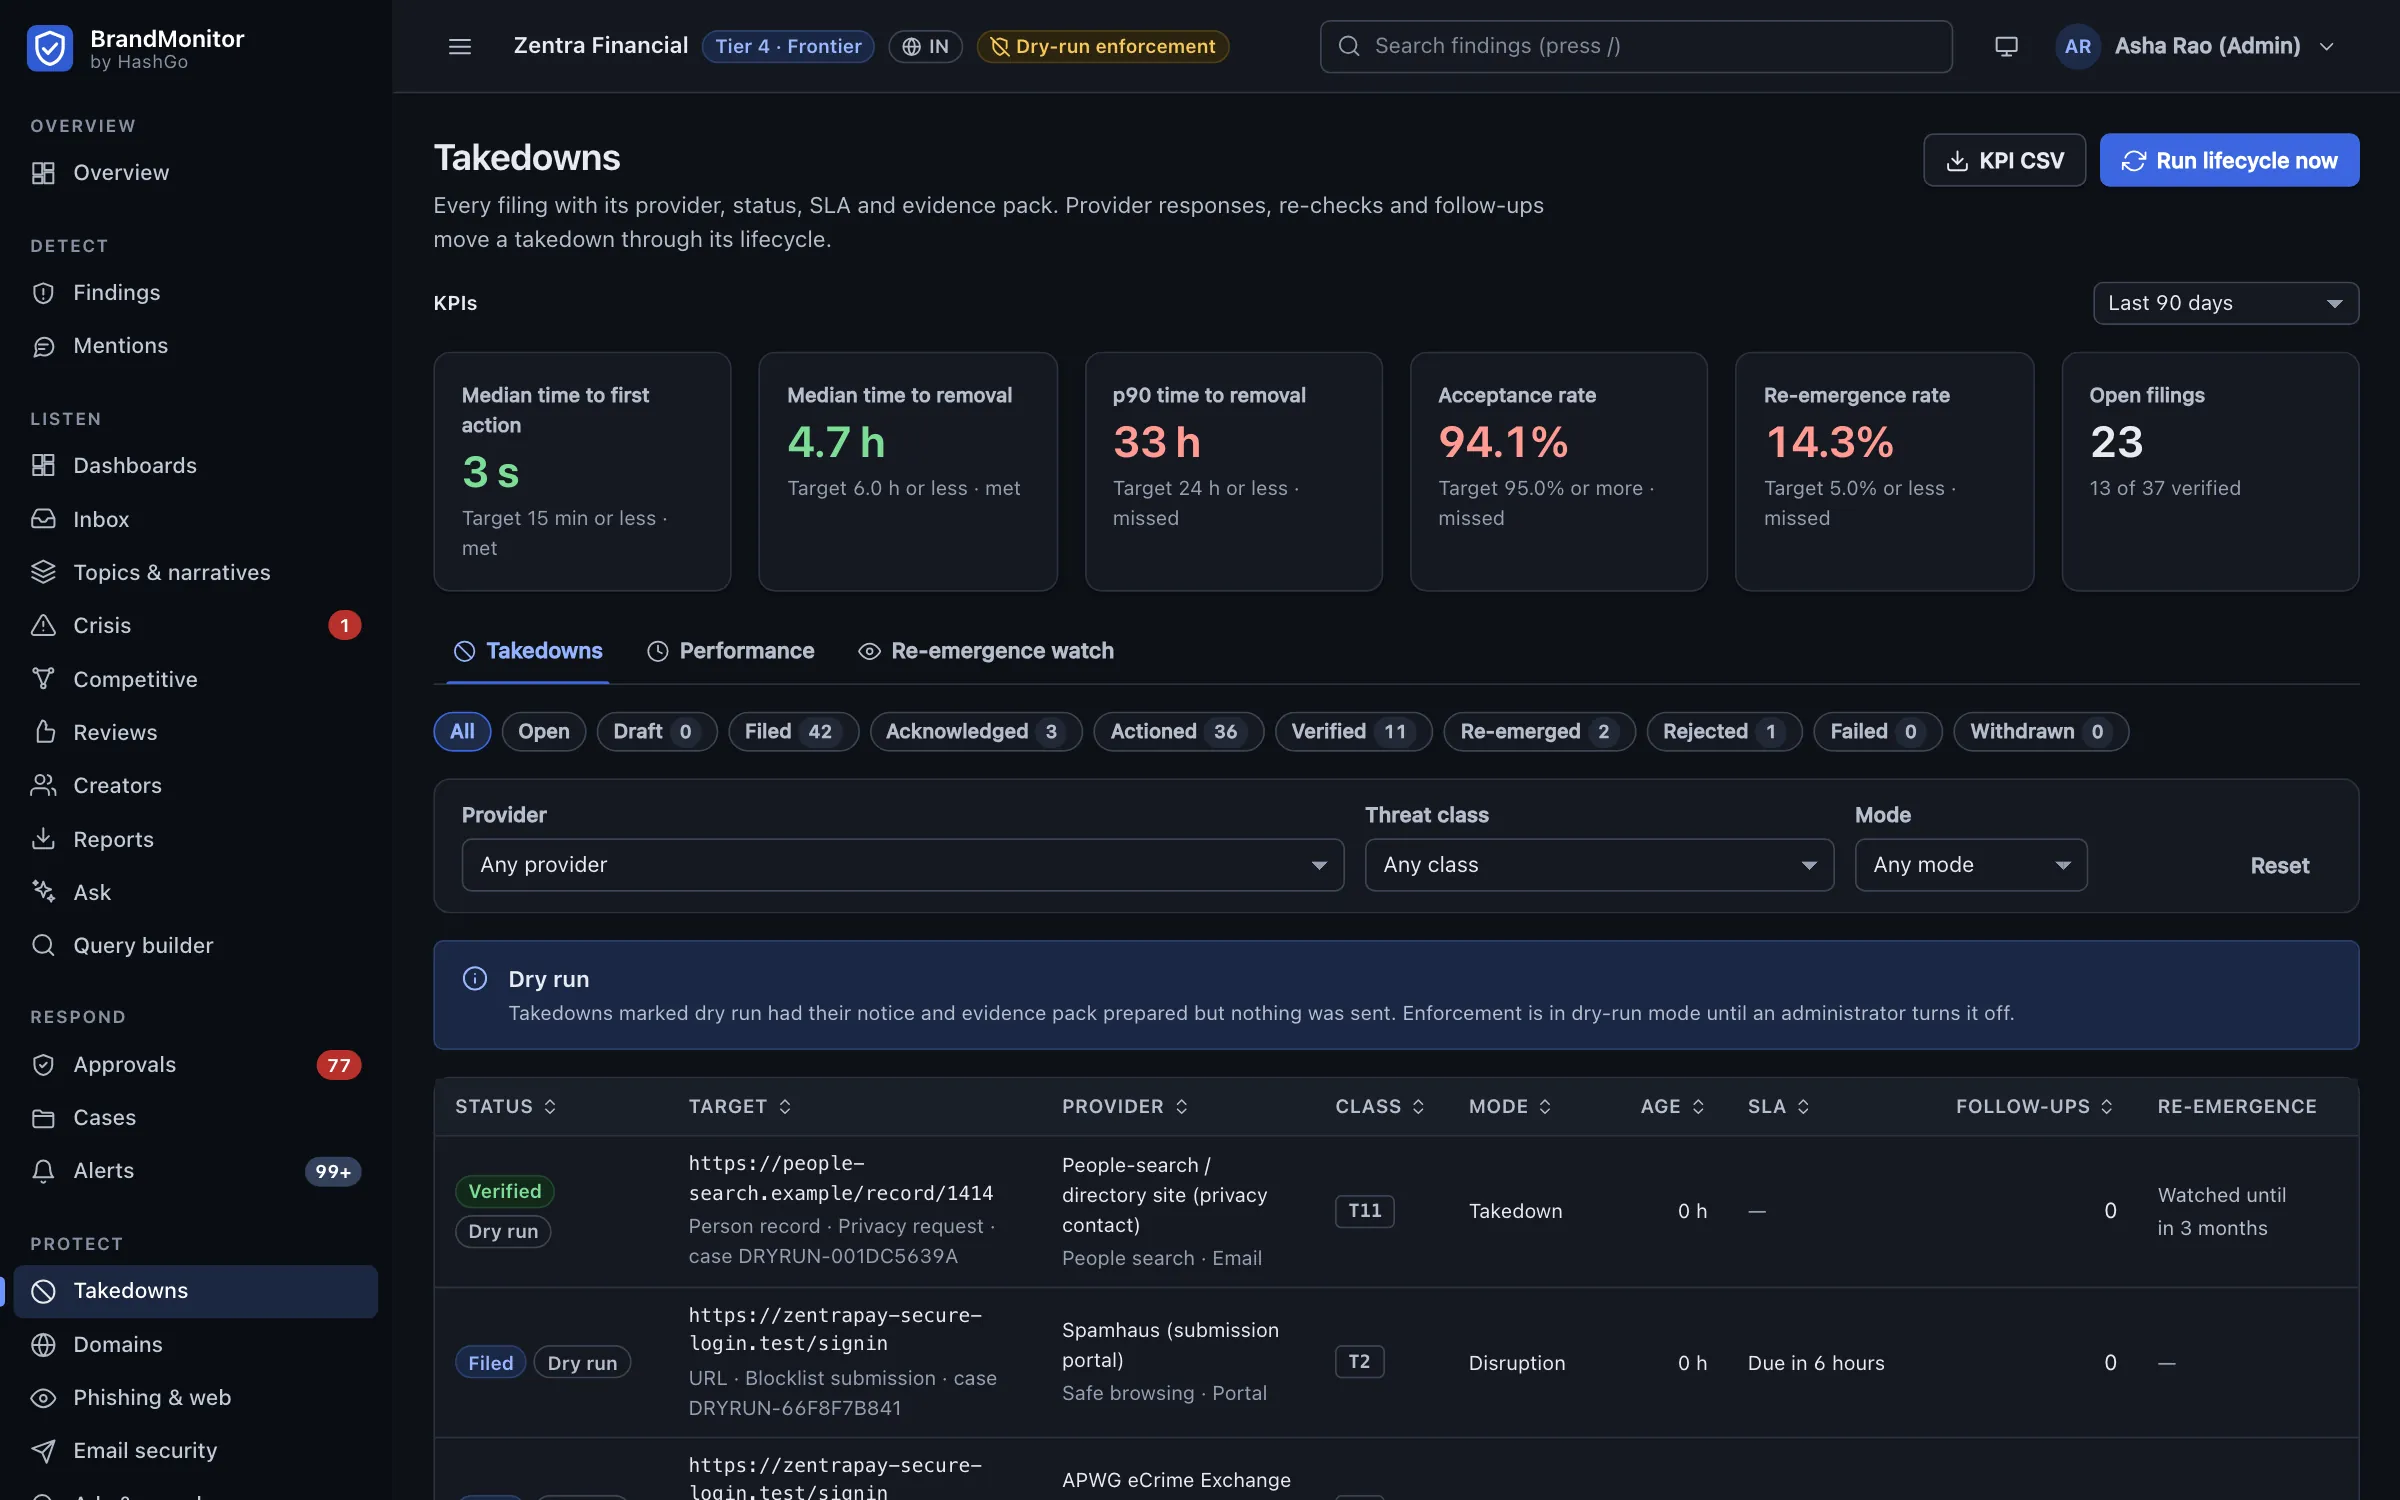
Takedowns view with median time to first action, time to removal, acceptance and re-emergence rates, and each filing with its provider, SLA and follow-ups
Takedowns. Every filing with its provider, SLA and evidence pack, plus time to removal and re-emergence.
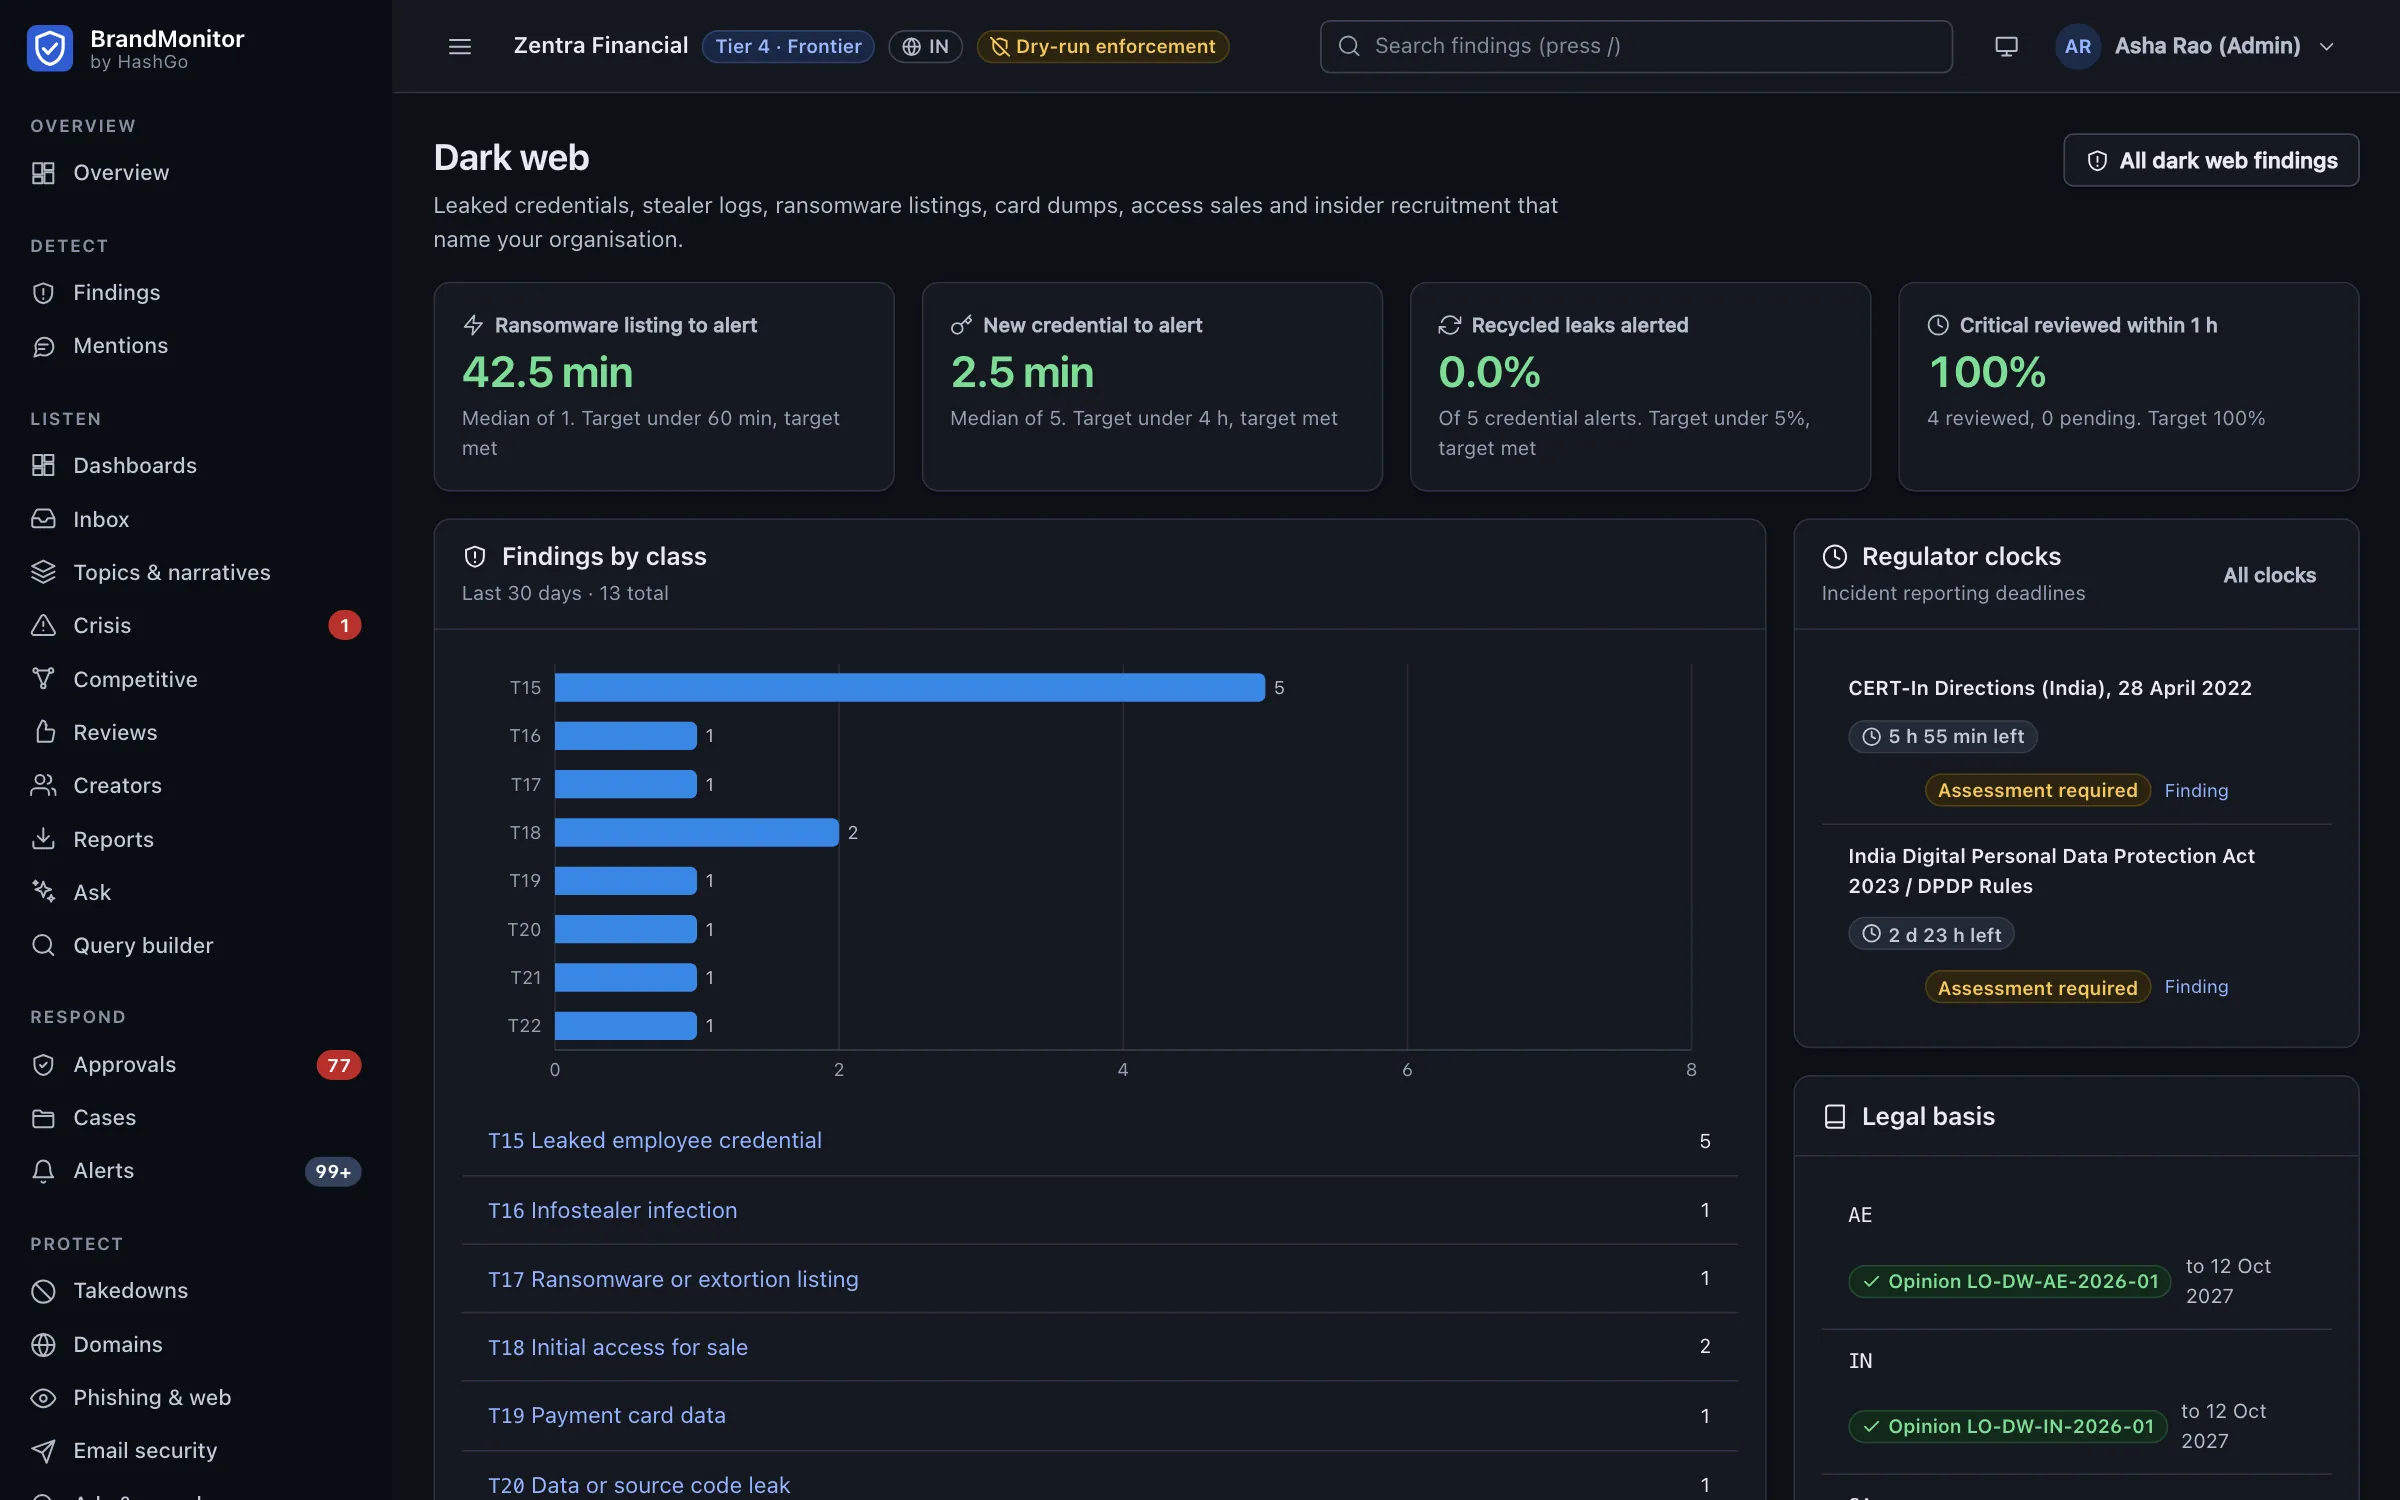
Dark web overview with alert times for ransomware listings and new credentials, findings by class, regulator reporting clocks and the legal basis for collection by region
Dark web. Leaked credentials, stealer logs, ransomware listings and card data, with regulator reporting clocks.
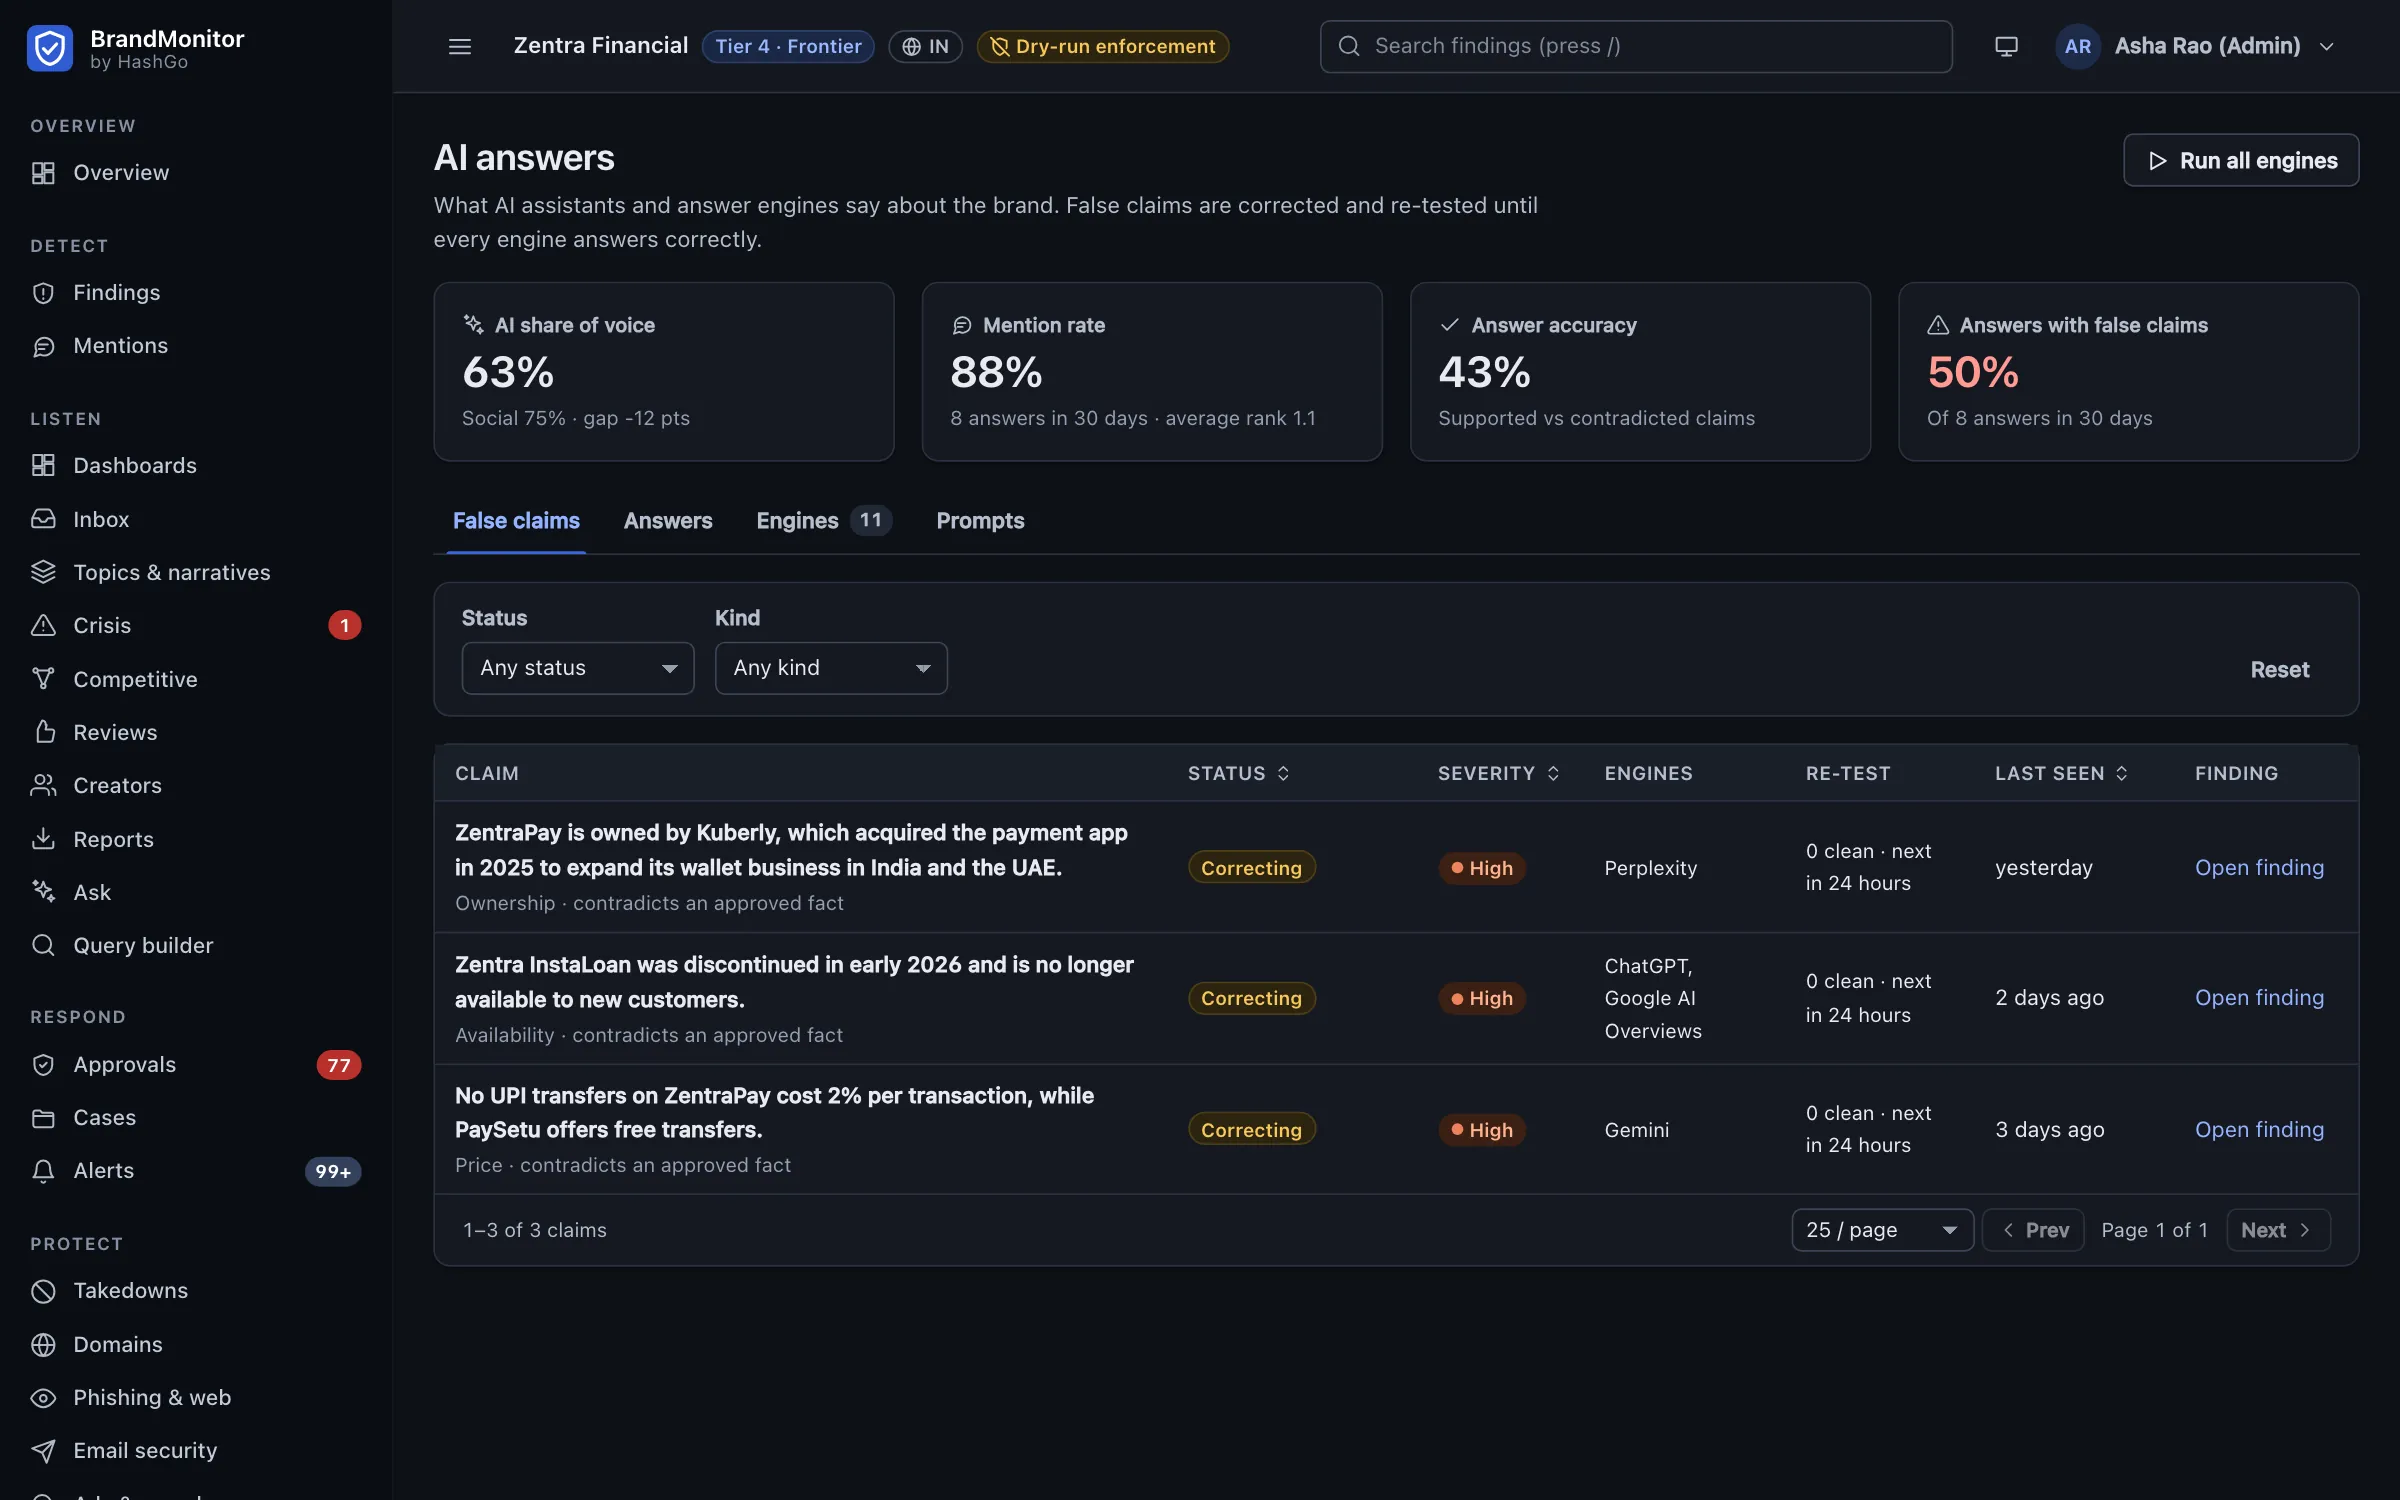
AI answers view with AI share of voice, mention rate, answer accuracy and false claims made by Perplexity, ChatGPT, Google AI Overviews and Gemini, each being corrected and re-tested
AI answers. What AI assistants say about your brand, with false claims corrected and re-tested.

Screens from the live platform with sample data from a fictional company, Zentra Financial. The takedowns shown ran in dry-run mode: the notice and evidence pack were prepared, but nothing was sent.

Capabilities

What Brand Monitoring does.

One finding follows each threat from first sighting to removal, with its source, confidence, risk and evidence attached.

01

Web and domain protection

Catch the lookalike before the phishing email goes out.

  • Lookalike domains from certificate transparency, zone files and permutations
  • Phishing capture with cloaking checks and logo matching
  • Email authentication and DMARC reports
  • Ads and search results that bid on your name
02

Impersonation and counterfeits

Your name, logo and people, used without permission.

  • Fake social profiles, apps and support numbers
  • Marketplace sellers, seller networks and test purchases
  • Executive protection, with the person's consent
  • Deepfake and voice-clone scams
03

Dark web and threat intel

Know when your data or access is for sale.

  • Leaked credentials, stealer logs, card data and ransomware listings
  • Collection in an isolated pool; evidence sealed in a vault
  • STIX/TAXII and MISP feed of your indicators
  • Analyst review with SLAs and regulator reporting clocks
04

Takedowns that close

From evidence to removal, and watched afterwards.

  • Evidence packs built for registrars, hosts and platforms
  • Routing to the right provider or reporting route
  • Follow-ups until removal, then a re-emergence watch
  • Block-list and safe-browsing submissions
05

Listening and AI answers

What people, and AI assistants, say about you.

  • 25 listening sources with sentiment, topics and narratives
  • Crisis detection, reviews, creators and competitive share of voice
  • False claims in AI answers found, corrected and re-tested
  • Questions about your brand answered in plain language
06

Agents with a human gate

Automation where it is safe, a person where it is not.

  • Autonomy set per threat class: automatic, approval or never
  • Calibrated confidence thresholds and an independent verifier
  • Approval chains, separation of duties and evidence hashes
  • Kill switches, budgets and a recorded trail for every agent

How it works

Four steps, start to finish.

01

Add your brand

Domains, handles, apps, executives, products and payment identifiers, in a guided setup.

02

Agents collect and triage

Collectors watch each source; triage scores relevance, confidence and severity, and drops the noise.

03

A person decides

Anything irreversible waits for approval, with the evidence and the reasoning attached.

04

Act and keep watching

Takedowns, block lists and alerts go out, and the agents watch for the threat coming back.

Coverage

What it covers.

Web and domains

  • Lookalike domains
  • Certificate transparency
  • Phishing sites
  • Email and DMARC
  • Ads and search

Social, apps and marketplaces

  • Social media
  • App stores
  • Marketplaces
  • Messaging channels
  • Fake support numbers

Dark web

  • Leaked credentials
  • Stealer logs
  • Ransomware sites
  • Card data
  • Access sales

AI and media

  • ChatGPT
  • Gemini
  • Perplexity
  • Google AI Overviews
  • Deepfakes
  • Voice clones

India and the Gulf

  • UPI and payment-link fraud
  • Smishing sender IDs
  • Fake lending apps
  • CERT-In
  • NCRP
  • NIXI
  • TDRA

Integrations

  • SIEM
  • SOAR
  • ITSM
  • Block lists
  • Chat
  • SSO and SCIM
  • GraphQL
  • MCP

Data handling

Evidence that holds up.

How the platform treats your brand data, the evidence it collects and the actions it takes.

Where your data lives

Each deployment runs in a data-residency cell. The hosted service runs in India; a dedicated cell or an installation in your own cloud is available.

Encryption

Per-tenant envelope encryption with bring-your-own-key, keyed hashing for watch lists, and credentials kept in a vault.

Evidence you can prove

Every finding keeps its provenance and hash-chained evidence, and each approval records the hash of what the approver saw.

AI processing

Detection runs on deterministic models by default. Claude, or an open-weights model in your own cloud, can be switched on per task, with residency-aware routing and cost ceilings.

Dark web, done carefully

Collection runs in an isolated pool with its own credentials and network egress, reads public pages only, and records the legal basis for each region.

Accountability

Every human, agent and API action is written to a hash-chained audit log, with role-based access and just-in-time elevation. Security questions: info@threatxintel.com.

Pricing

Priced per protected brand. Published, not quoted.

Plans are sized by brands, users and takedowns. Start by listening, add protection when you need it, and see every price before you talk to sales.

Prices are per organization per month, billed yearly.

Free POC

Evaluation on your own brand

₹0

$0 · 14 days

  • 1 brand
  • 3 users
  • Lookalike domains, phishing and fake profiles
  • Takedowns prepared in dry-run, never sent
  • PDF findings report
Request a POC

Starter

Marketing teams and agencies

₹14,999/month

$199/month

  • 1 brand
  • 3 users
  • Listening across 25 sources
  • Lookalike domain and phishing alerts
  • DMARC reports
  • 13-month archive
Request access

Growth

Mid-market marketing, PR and CX

₹44,999/month

$599/month

  • 3 brands
  • 10 users
  • Everything in Starter
  • Crisis detection and reviews
  • Fake profiles, apps and support numbers
  • Ads bidding on your name
  • Cases and workflow
Request access

Enterprise

Banks, fintechs, telecoms and large groups

From₹30 lakh/year

From $36,000/year

  • Contracted brands and takedowns
  • Everything in Protect
  • AI answer monitoring
  • Deepfake and voice-clone scams
  • Analyst review with SLAs
  • Customer-managed keys and SCIM
  • 24x7 support and a named manager
Talk to sales
  • A brand is one name your customers recognise, with its domains, social handles, apps, executives and payment identifiers. A sub-brand with its own name counts as a separate brand.
  • A user is anyone who triages findings, approves actions or changes settings. Read-only viewers are free.
  • A takedown is one filing to remove one item: a domain, page, profile, app or listing. Follow-ups, and re-filing the same item if it comes back, are free. Unused takedowns do not carry over.
  • AI is included on every plan within a monthly cost ceiling you set. At the ceiling, detection carries on with deterministic models.
  • INR prices exclude 18% GST; USD prices exclude local taxes.
  • Monthly billing costs 20% more than yearly billing.
Compare every feature by plan
FeatureStarterGrowthProtectEnterprise
Monitoring
Protected brands133Contracted
Users310UnlimitedUnlimited
Listening across 25 sources, with sentiment, topics and narrativesIncludedIncludedIncludedIncluded
Lookalike domains from certificate transparency, zone files and permutationsIncludedIncludedIncludedIncluded
Phishing site detection with cloaking checks and logo matchingIncludedIncludedIncludedIncluded
Email authentication and DMARC reportsIncludedIncludedIncludedIncluded
Searchable archive13 months2 years2 yearsContracted
Crisis detection, reviews, creators and competitive share of voiceNot includedIncludedIncludedIncluded
Fake social profiles, apps and support numbersNot includedIncludedIncludedIncluded
Ads and search results that bid on your nameNot includedIncludedIncludedIncluded
Protection
Marketplace sellers, seller networks and counterfeitsNot includedNot includedIncludedIncluded
Dark web: leaked credentials, stealer logs, card data and ransomware listingsNot includedNot includedIncludedIncluded
Executive protection, with the person's consentNot includedNot included5 peopleContracted
Takedowns with evidence packs, follow-ups and a re-emergence watchNot includedNot included25 a monthContracted
Block-list and safe-browsing submissionsNot includedNot includedIncludedIncluded
UPI and payment-link fraud, smishing sender IDs and fake lending appsNot includedNot includedIncludedIncluded
Reporting routes to CERT-In, NCRP, NIXI and TDRANot includedNot includedIncludedIncluded
AI and media
AI answers: what ChatGPT, Gemini, Perplexity and Google AI Overviews say about youNot includedAdd-onAdd-onIncluded
Deepfake and voice-clone scamsNot includedNot includedNot includedIncluded
Analyst review with SLAs and regulator reporting clocksNot includedNot includedAdd-onIncluded
Agents and workflow
Autonomy per threat class: automatic, approval or neverIncludedIncludedIncludedIncluded
Approval chains, separation of duties and evidence hashesIncludedIncludedIncludedIncluded
Cases, assignments and workflowNot includedIncludedIncludedIncluded
Integrations
Email and chat alertsIncludedIncludedIncludedIncluded
WebhooksNot includedIncludedIncludedIncluded
SIEM, SOAR, ITSM and block listsNot includedNot includedIncludedIncluded
STIX/TAXII and MISP feed of your indicatorsNot includedNot includedIncludedIncluded
GraphQL API and MCP serverNot includedNot includedIncludedIncluded
Security and deployment
Hosted in India, with a hash-chained audit logIncludedIncludedIncludedIncluded
Single sign-onNot includedNot includedIncludedIncluded
SCIM user provisioningNot includedNot includedNot includedIncluded
Customer-managed encryption keysNot includedNot includedNot includedIncluded
Dedicated cell or installation in your own cloudNot includedNot includedNot includedAdd-on
SupportEmail, next business dayEmail, next business dayPriority, business hours IST / GST24x7, named manager, 99.9% uptime SLA

Add-ons and services

Extend any plan.

Add-onIndia (INR)International (USD)What you get
Extra brand on Starter or Growth₹7,999/month$99/monthOne more protected brand
Extra brand on Protect₹39,999/month$499/monthOne more protected brand, with 5 more takedowns a month
Takedown pack (25 takedowns)₹24,999$299Valid for 12 months; used after your monthly allowance
AI answer monitoring, per brand₹19,999/month$249/monthOn Growth or Protect: what AI assistants say about you, with false claims corrected and re-tested
Executive protection, 5 more people₹14,999/month$199/monthOn Protect, with each person's consent
Managed analyst service₹1.5 lakh/month$2,500/monthThreatXIntel analysts triage findings and run takedowns within your policy, business hours IST / GST; 24x7 quoted
Threat intelligence feedFrom ₹6 lakh/yearFrom $7,500/yearSTIX/TAXII and MISP feed sold on its own, on 1-year or 3-year terms (3 years at 15% off)
Marketplace test purchasesQuotedQuotedPurchases that confirm counterfeits before enforcement
Dedicated cell or your own cloud+30% on Enterprise licence + ₹3 lakh one-time+30% on Enterprise licence + $4,000 one-timeA single-tenant data-residency cell, or an installation in your cloud account
Onboarding and reporting-route setupFree on Protect and EnterpriseFree on Protect and EnterpriseGuided setup of brands, sources, approvers and takedown routes

Partners (agencies, MSSPs, consultancies): 30% off list price, rising to 40% at 10 or more client brands, with a multi-client console and white-label reports.

Discounts and terms

Offers, billing and payment.

OfferDiscountApplies to
Launch offer30% off the first yearFirst 20 paying customers who agree to a published case study; ends 31 Dec 2026
Multi-year10% off for 2 years; 15% off for 3 yearsAll paid plans, billed yearly
Startups50% off Starter for the first yearCompanies under 2 years old with fewer than 20 employees
HashGo suite bundle20% off the combined list priceHashGo Brand Monitoring with any other HashGo product

Discounts do not combine.

Billing and payment terms

TermDetail
Free POC14 days on 1 brand, no card required; takedowns are prepared in dry-run and never sent
Billing cycleYearly in advance by default; monthly available at +20%
Adding brands or add-onsBilled pro rata for the rest of the term
Payment in IndiaBank transfer, UPI or card, with a GST tax invoice
International paymentWire transfer or card in USD
Enterprise payment termsNet 30 days from invoice
RenewalPrice increase capped at 7% a year
Billing entityThreatxintel Cyber Labs LLP, Bengaluru, India

Get started

  1. Request a POC at threatxintel.ai/request-access; no card required.
  2. We set up your brand, sources and approvers with you.
  3. Your team signs in at brandmonitor.threatxintel.ai and reviews the first findings.
  4. Switch takedowns from dry-run to live when you are ready.

Sales and Enterprise quotes: info@threatxintel.com

Prices are valid from 26 October 2026 and may change with notice. Existing customers keep their price until renewal.

FAQ

Questions, answered.

Something else? Ask the team.

What does Brand Monitoring watch?

Domains and certificates, phishing sites, social media, app stores, marketplaces, ads, the dark web, and the answers AI assistants give about your brand.

Will it take things down on its own?

Only where you allow it. Each threat class has an autonomy rule: automatic, needs approval, or never. Irreversible actions wait for a person, and enforcement starts in dry-run mode until you switch it on.

How do takedowns work?

The agents build an evidence pack, send it to the right registrar, host, platform or reporting route, follow up until the content is removed, then watch for it to return. Some routes need your platform credentials or a trusted-reporter relationship; we set these up with you during onboarding.

How do you keep false alarms down?

Every finding has a relevance score, a calibrated confidence and a stored reason. Your official assets and verified accounts are protected from action, and an independent verifier re-checks the evidence before anything is filed.

Do you cover India and the Gulf?

Yes: UPI and payment-link fraud, smishing sender IDs, fake lending apps and regional marketplaces, with reporting routes to CERT-In, NCRP, NIXI and TDRA.

Can it send alerts to our SOC?

Yes. Findings and actions flow to your SIEM, SOAR and ticketing tools, chat and webhooks, and are available as a STIX/TAXII feed, through GraphQL and through an MCP server.

What does it cost?

Plans start at ₹14,999 / $199 a month for one brand, billed yearly. Takedowns and dark web monitoring start on Protect at ₹1,49,999 / $1,999 a month. A 14-day POC on your own brand is free. See pricing.

How do we get started?

HashGo Brand Monitoring is live. Request a POC or book a demo; we set up your brand, sources and approvers with you, and your team signs in at brandmonitor.threatxintel.ai.
See who is using your name.

Open the platform, request a POC for your own brand, or book a demo and we will walk you through it.