HashGo · Threat modeling

HashGo Threat Modeling Live

See the attack before it is built.

HashGo Threat Modeling draws your system from code, cloud and design documents, finds the threats your architecture creates, shows the attack paths to your crown jewels, and puts a price on each risk. It updates itself on every pull request.

115explainable threat rules, each showing why it fired
24labelled reference systems re-checked on every release
5 secondsmedian time from repository to first model

Internal measurements, October 2026: five open-source repositories took 3 to 37 seconds from connection to first model, with AI review switched off. Precision and recall from customer pilots will be published here.

Product tour

Inside HashGo Threat Modeling.

What your team sees after sign-in: a model that drew itself, the threats it implies, and the paths and money behind each one. Click any screen to enlarge it.

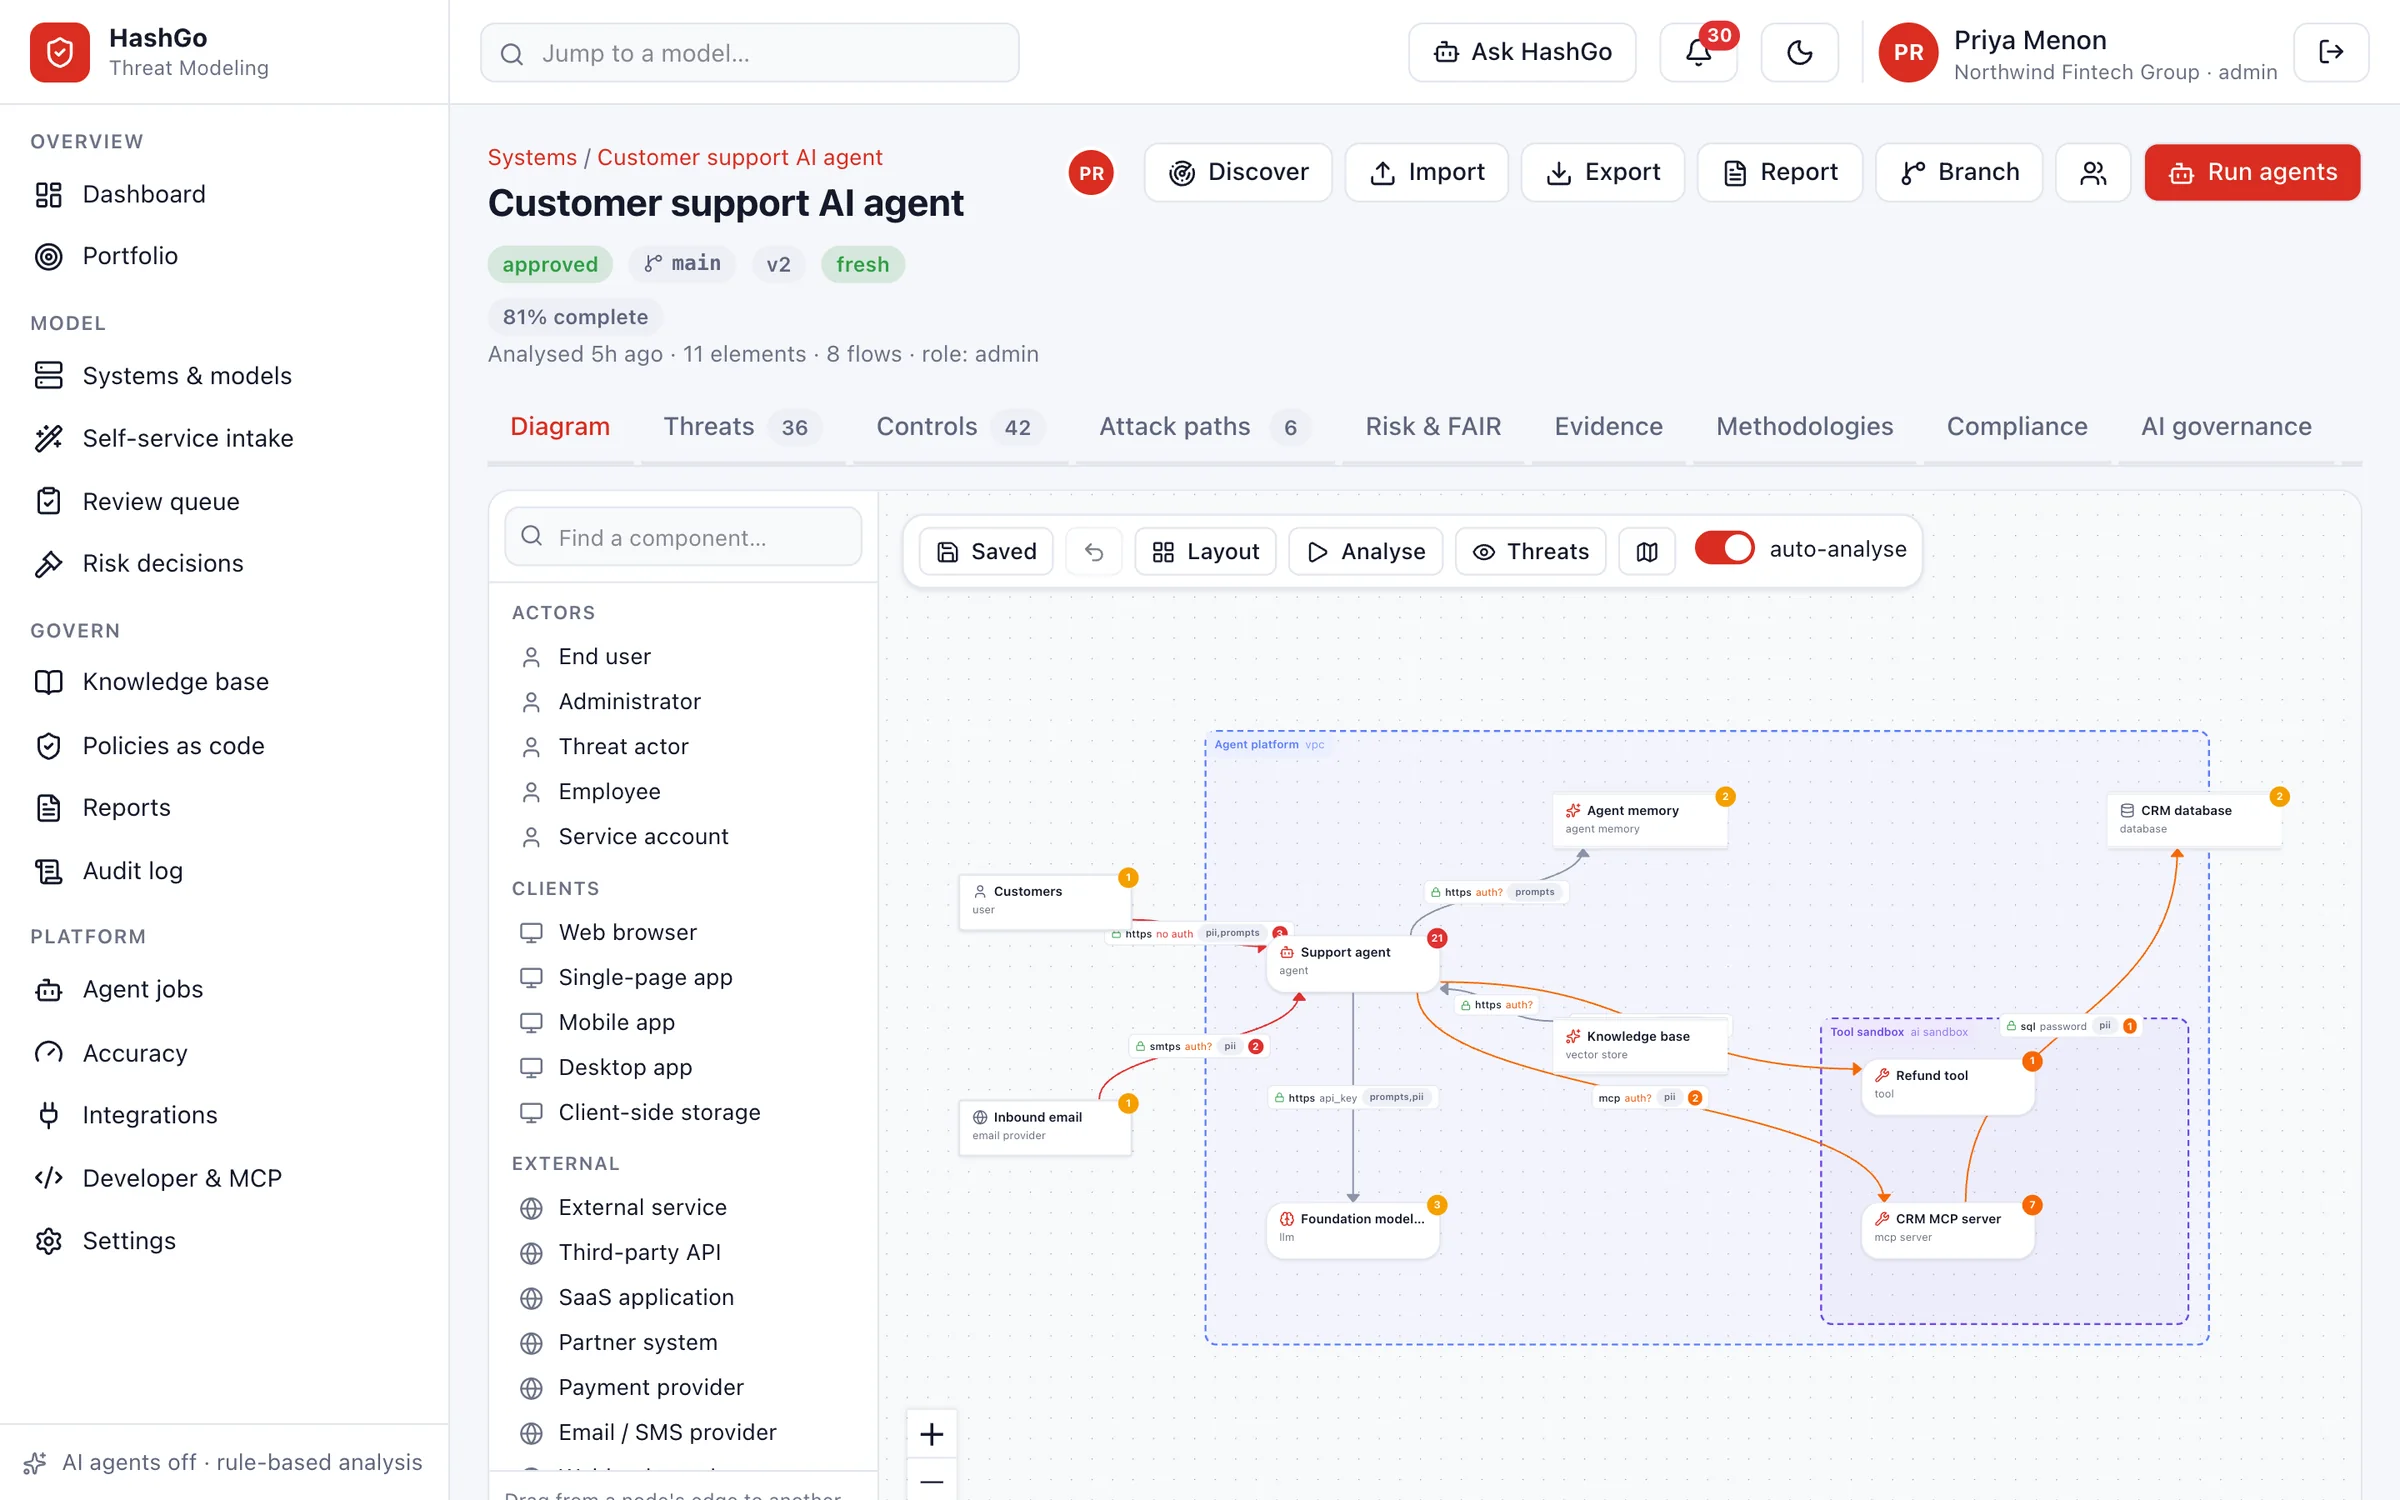
HashGo Threat Modeling diagram of an AI support agent with trust boundaries, data flows labelled with protocol and authentication, and open-threat counts on each component
Diagram. Components, data flows and trust boundaries, drawn by the agents or by hand, with the open threats on every element and flow.
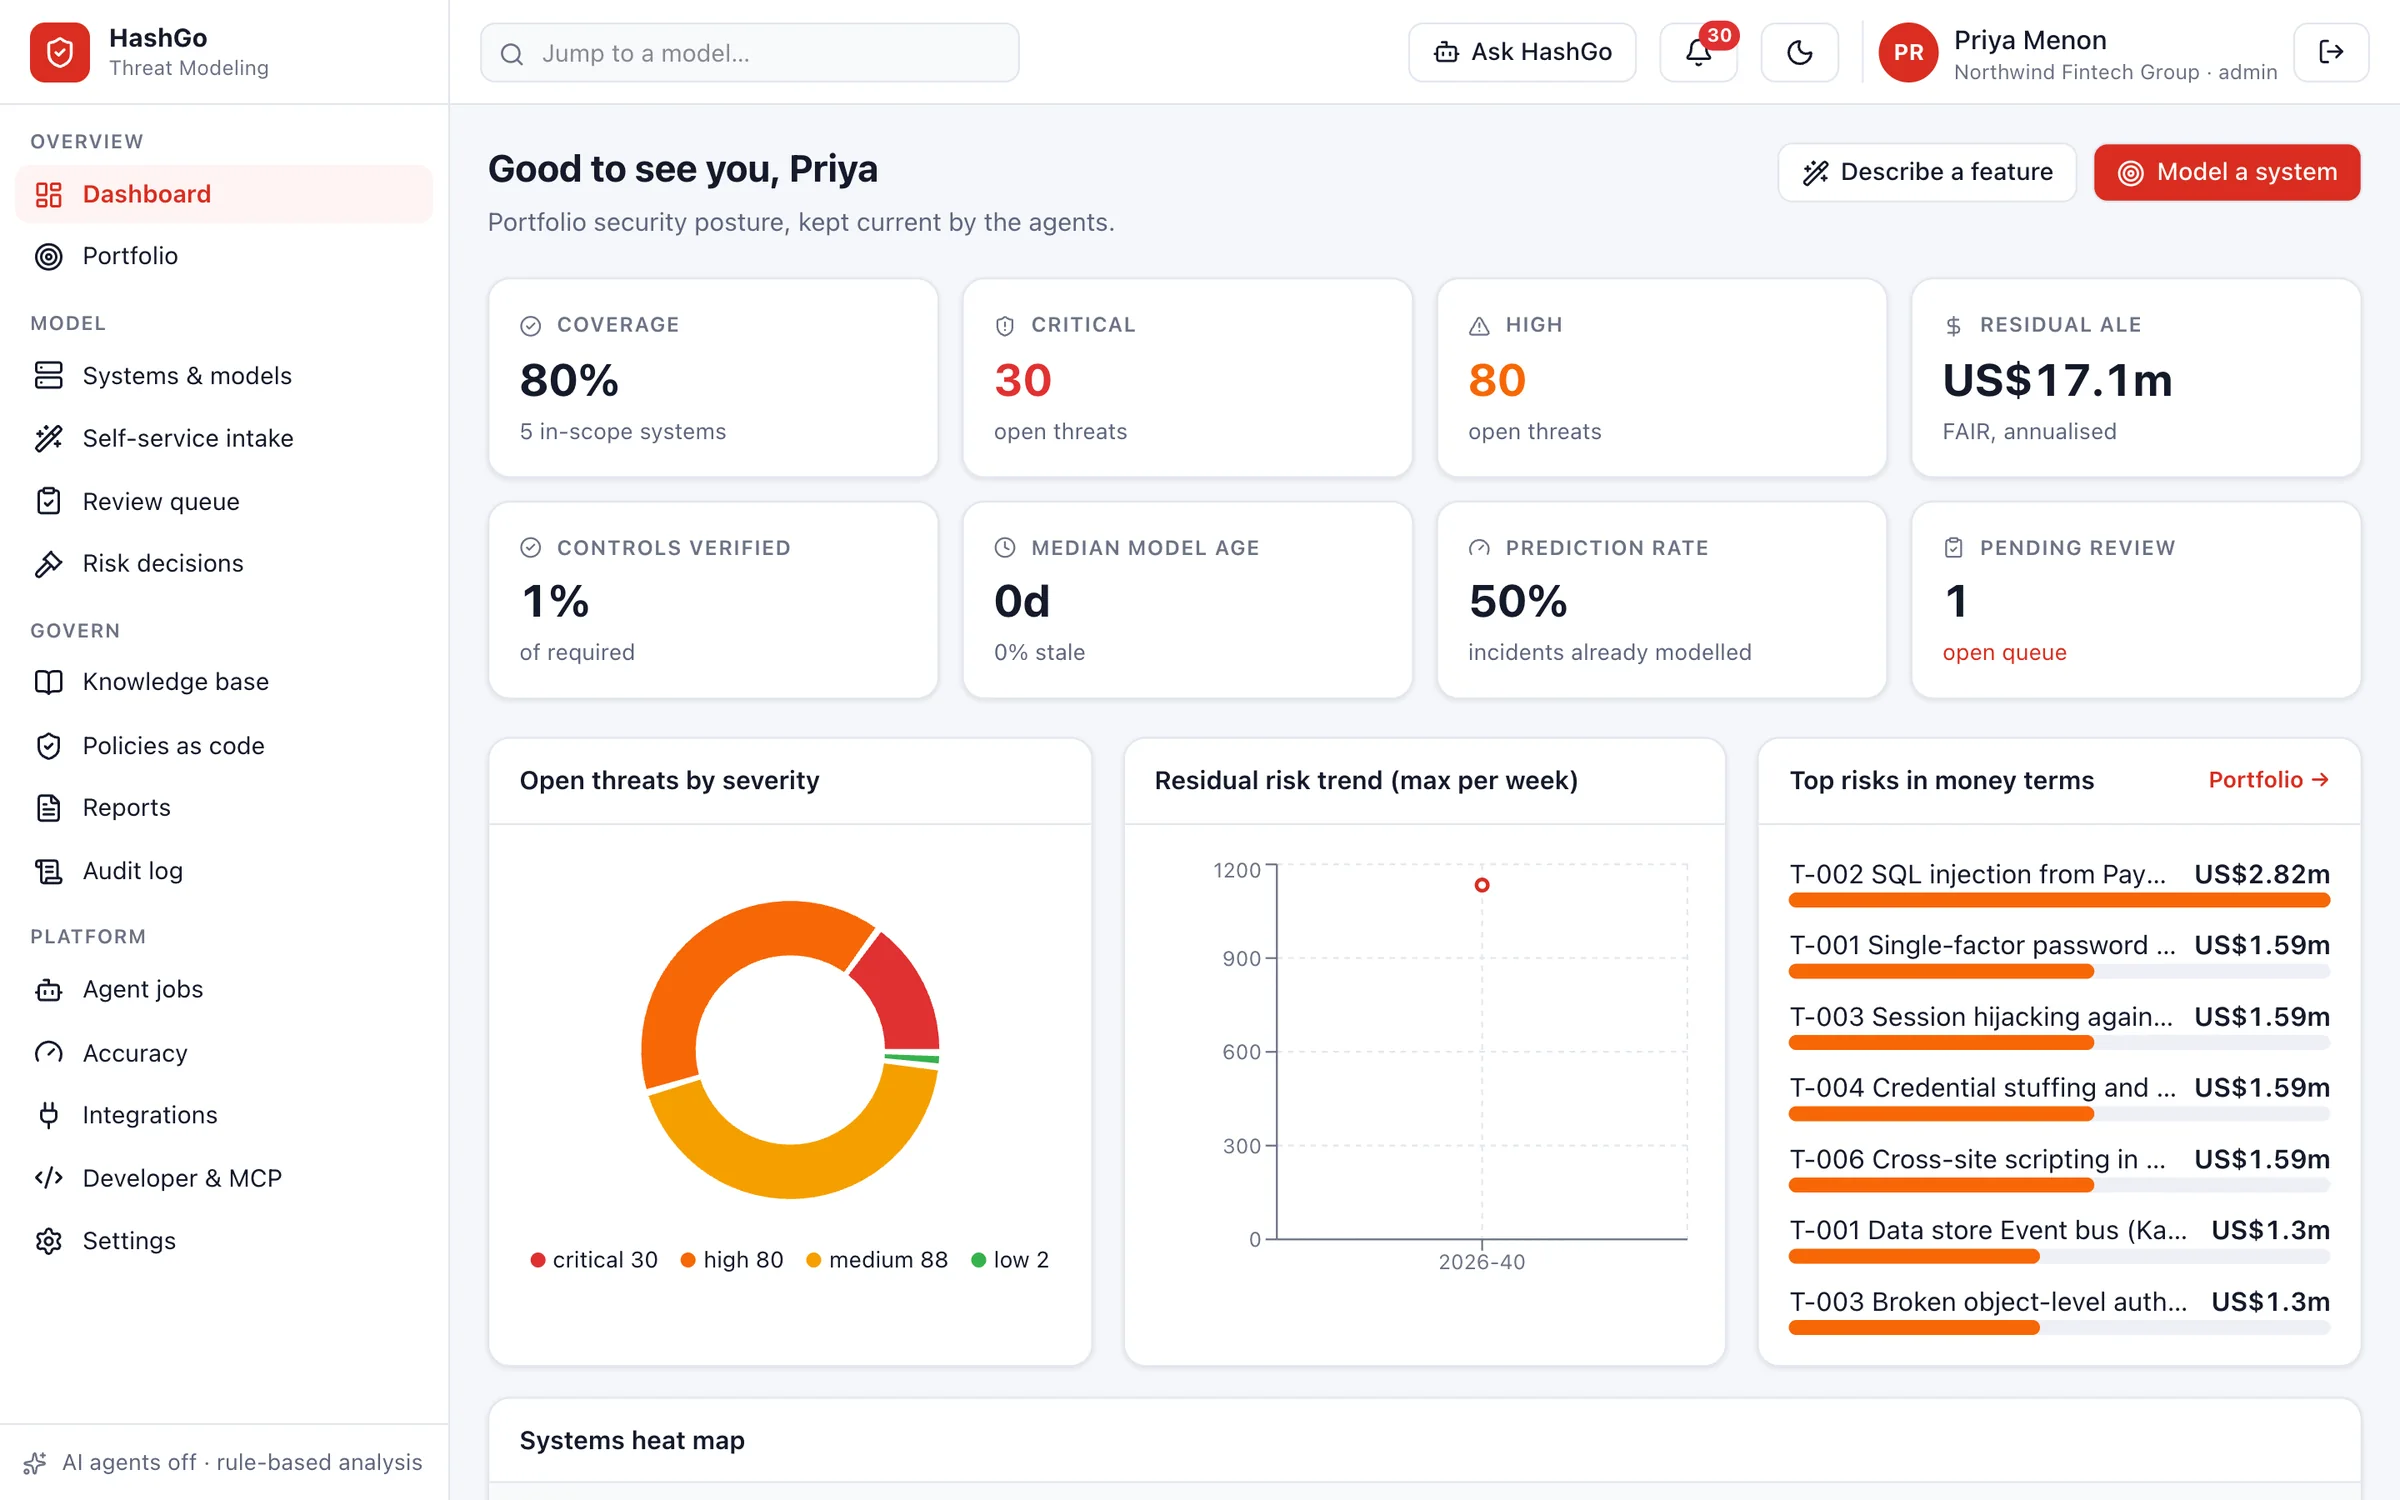
HashGo Threat Modeling portfolio dashboard with coverage, open critical and high threats, annualised loss, prediction rate and top risks in money
Overview. Coverage, freshness, open risk and expected loss across every system.
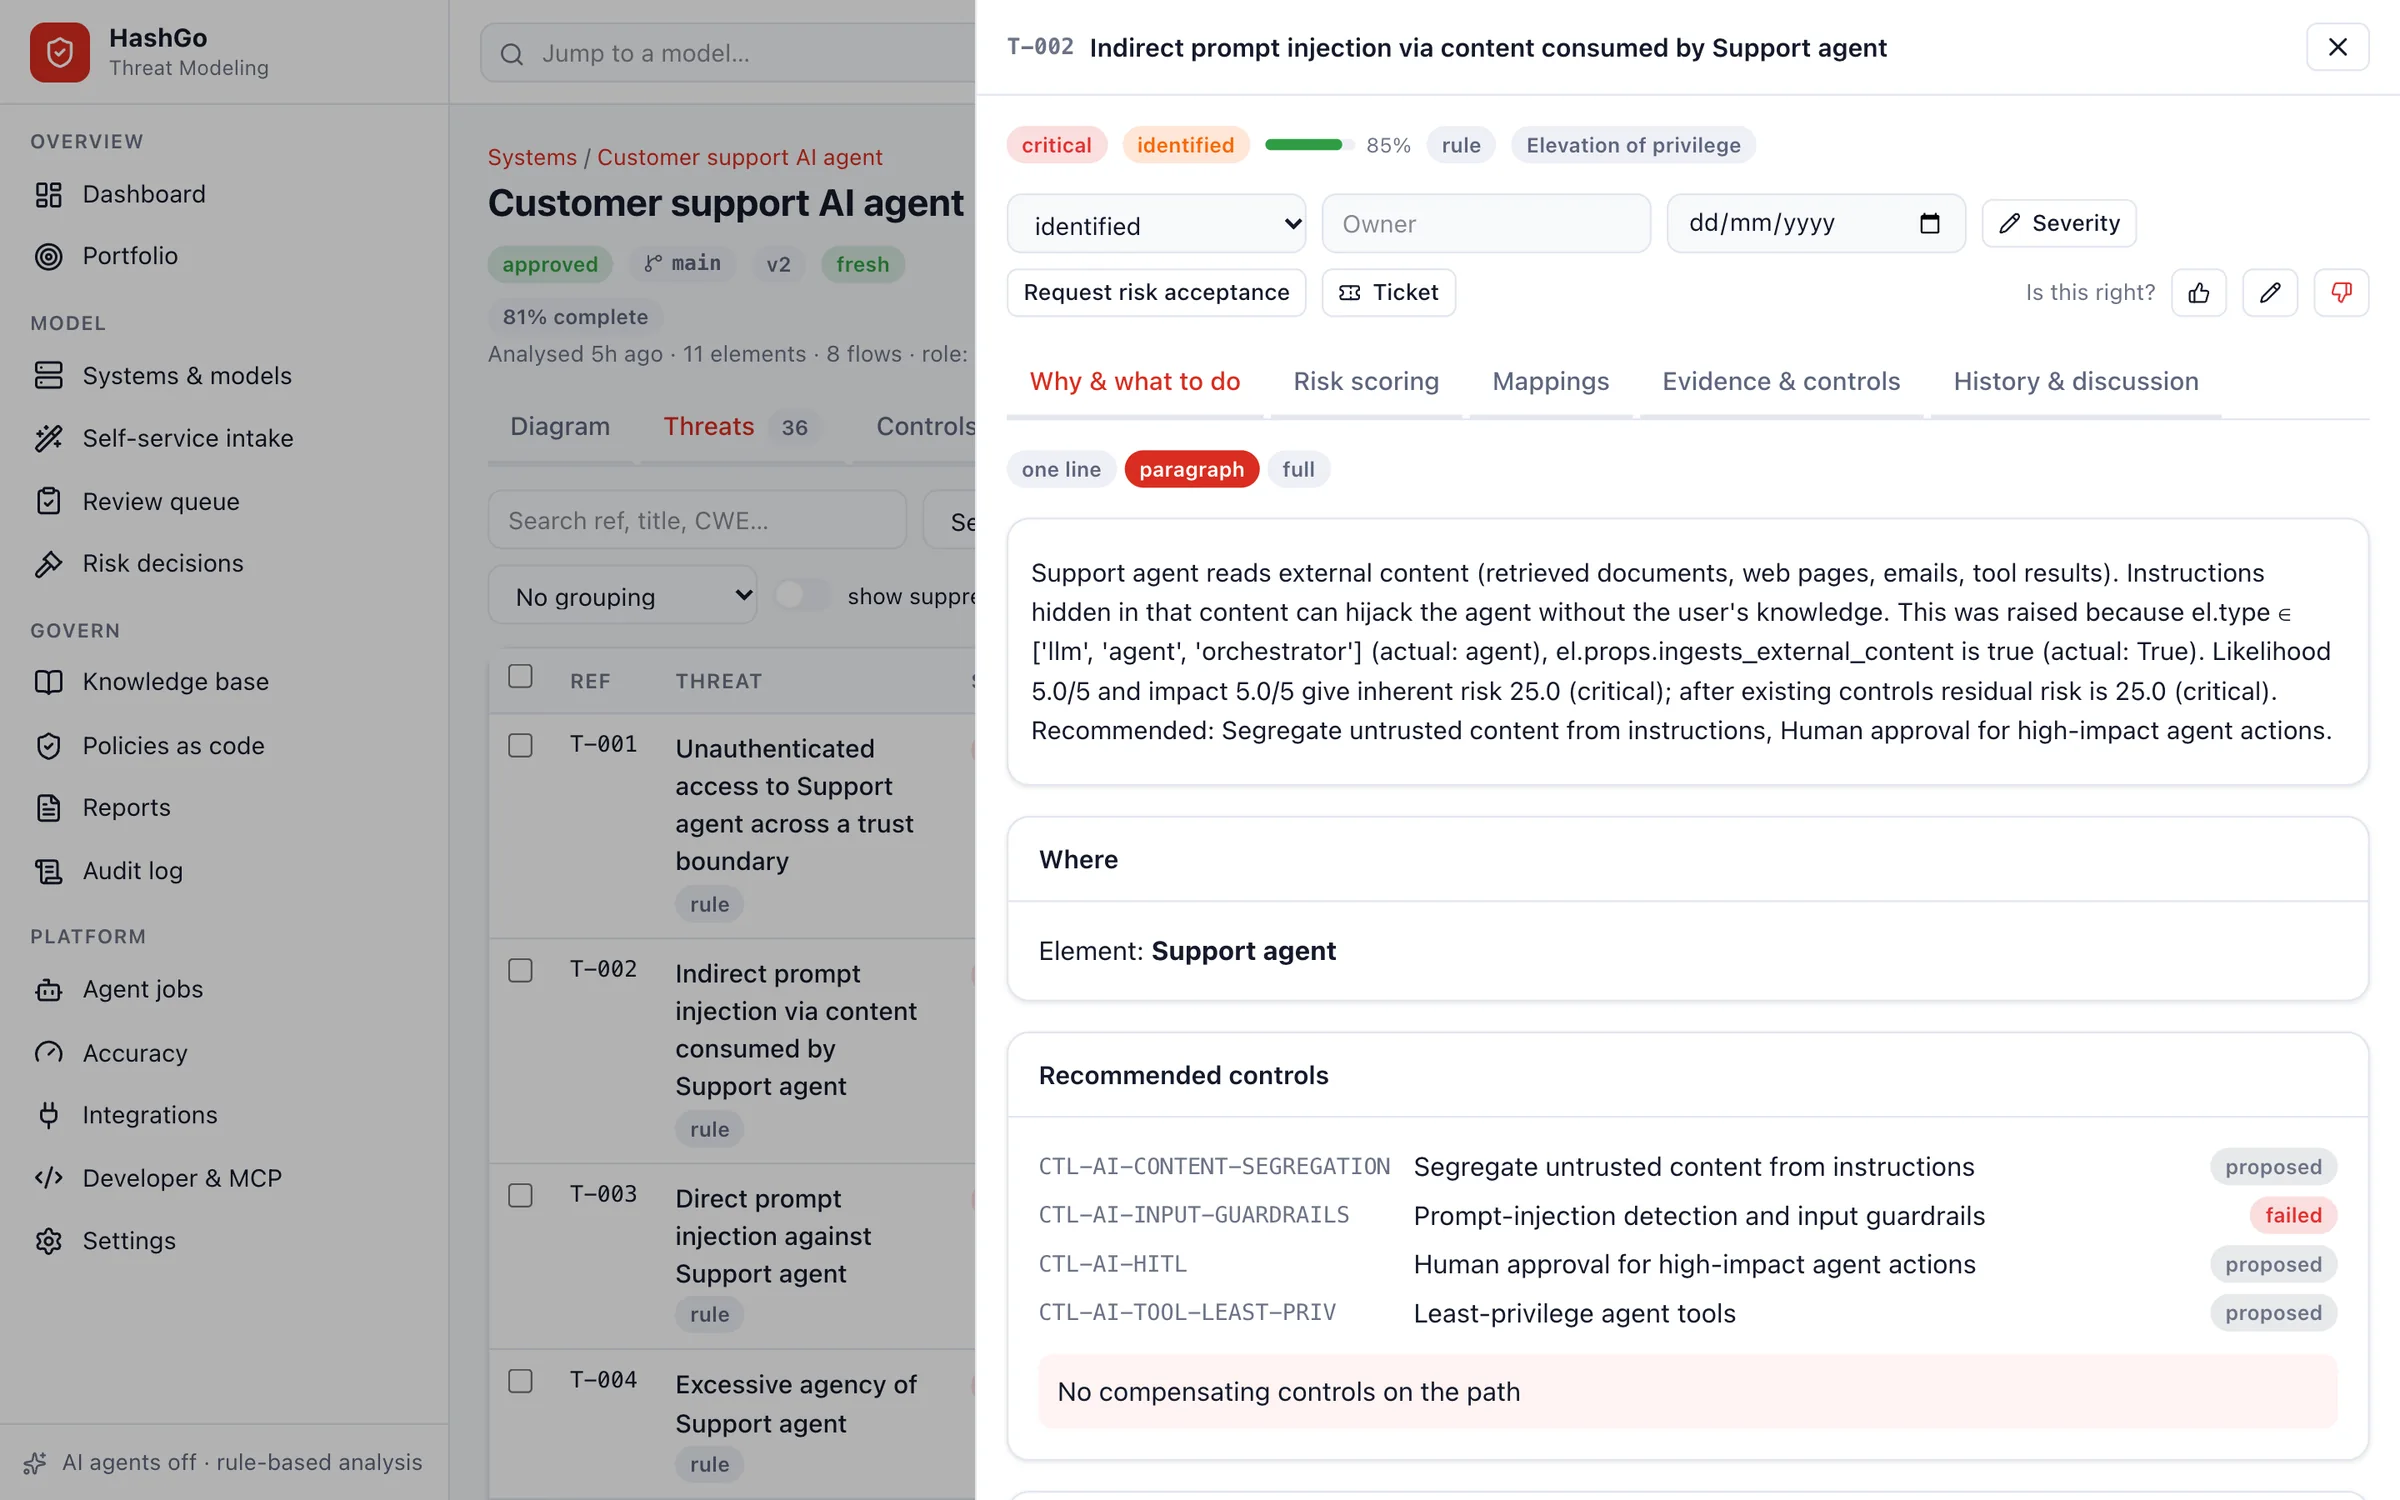
Threat detail for an indirect prompt injection showing the plain-language explanation, affected element and recommended controls with their status
Threats. Why each threat applies, in plain language, with the controls that answer it.
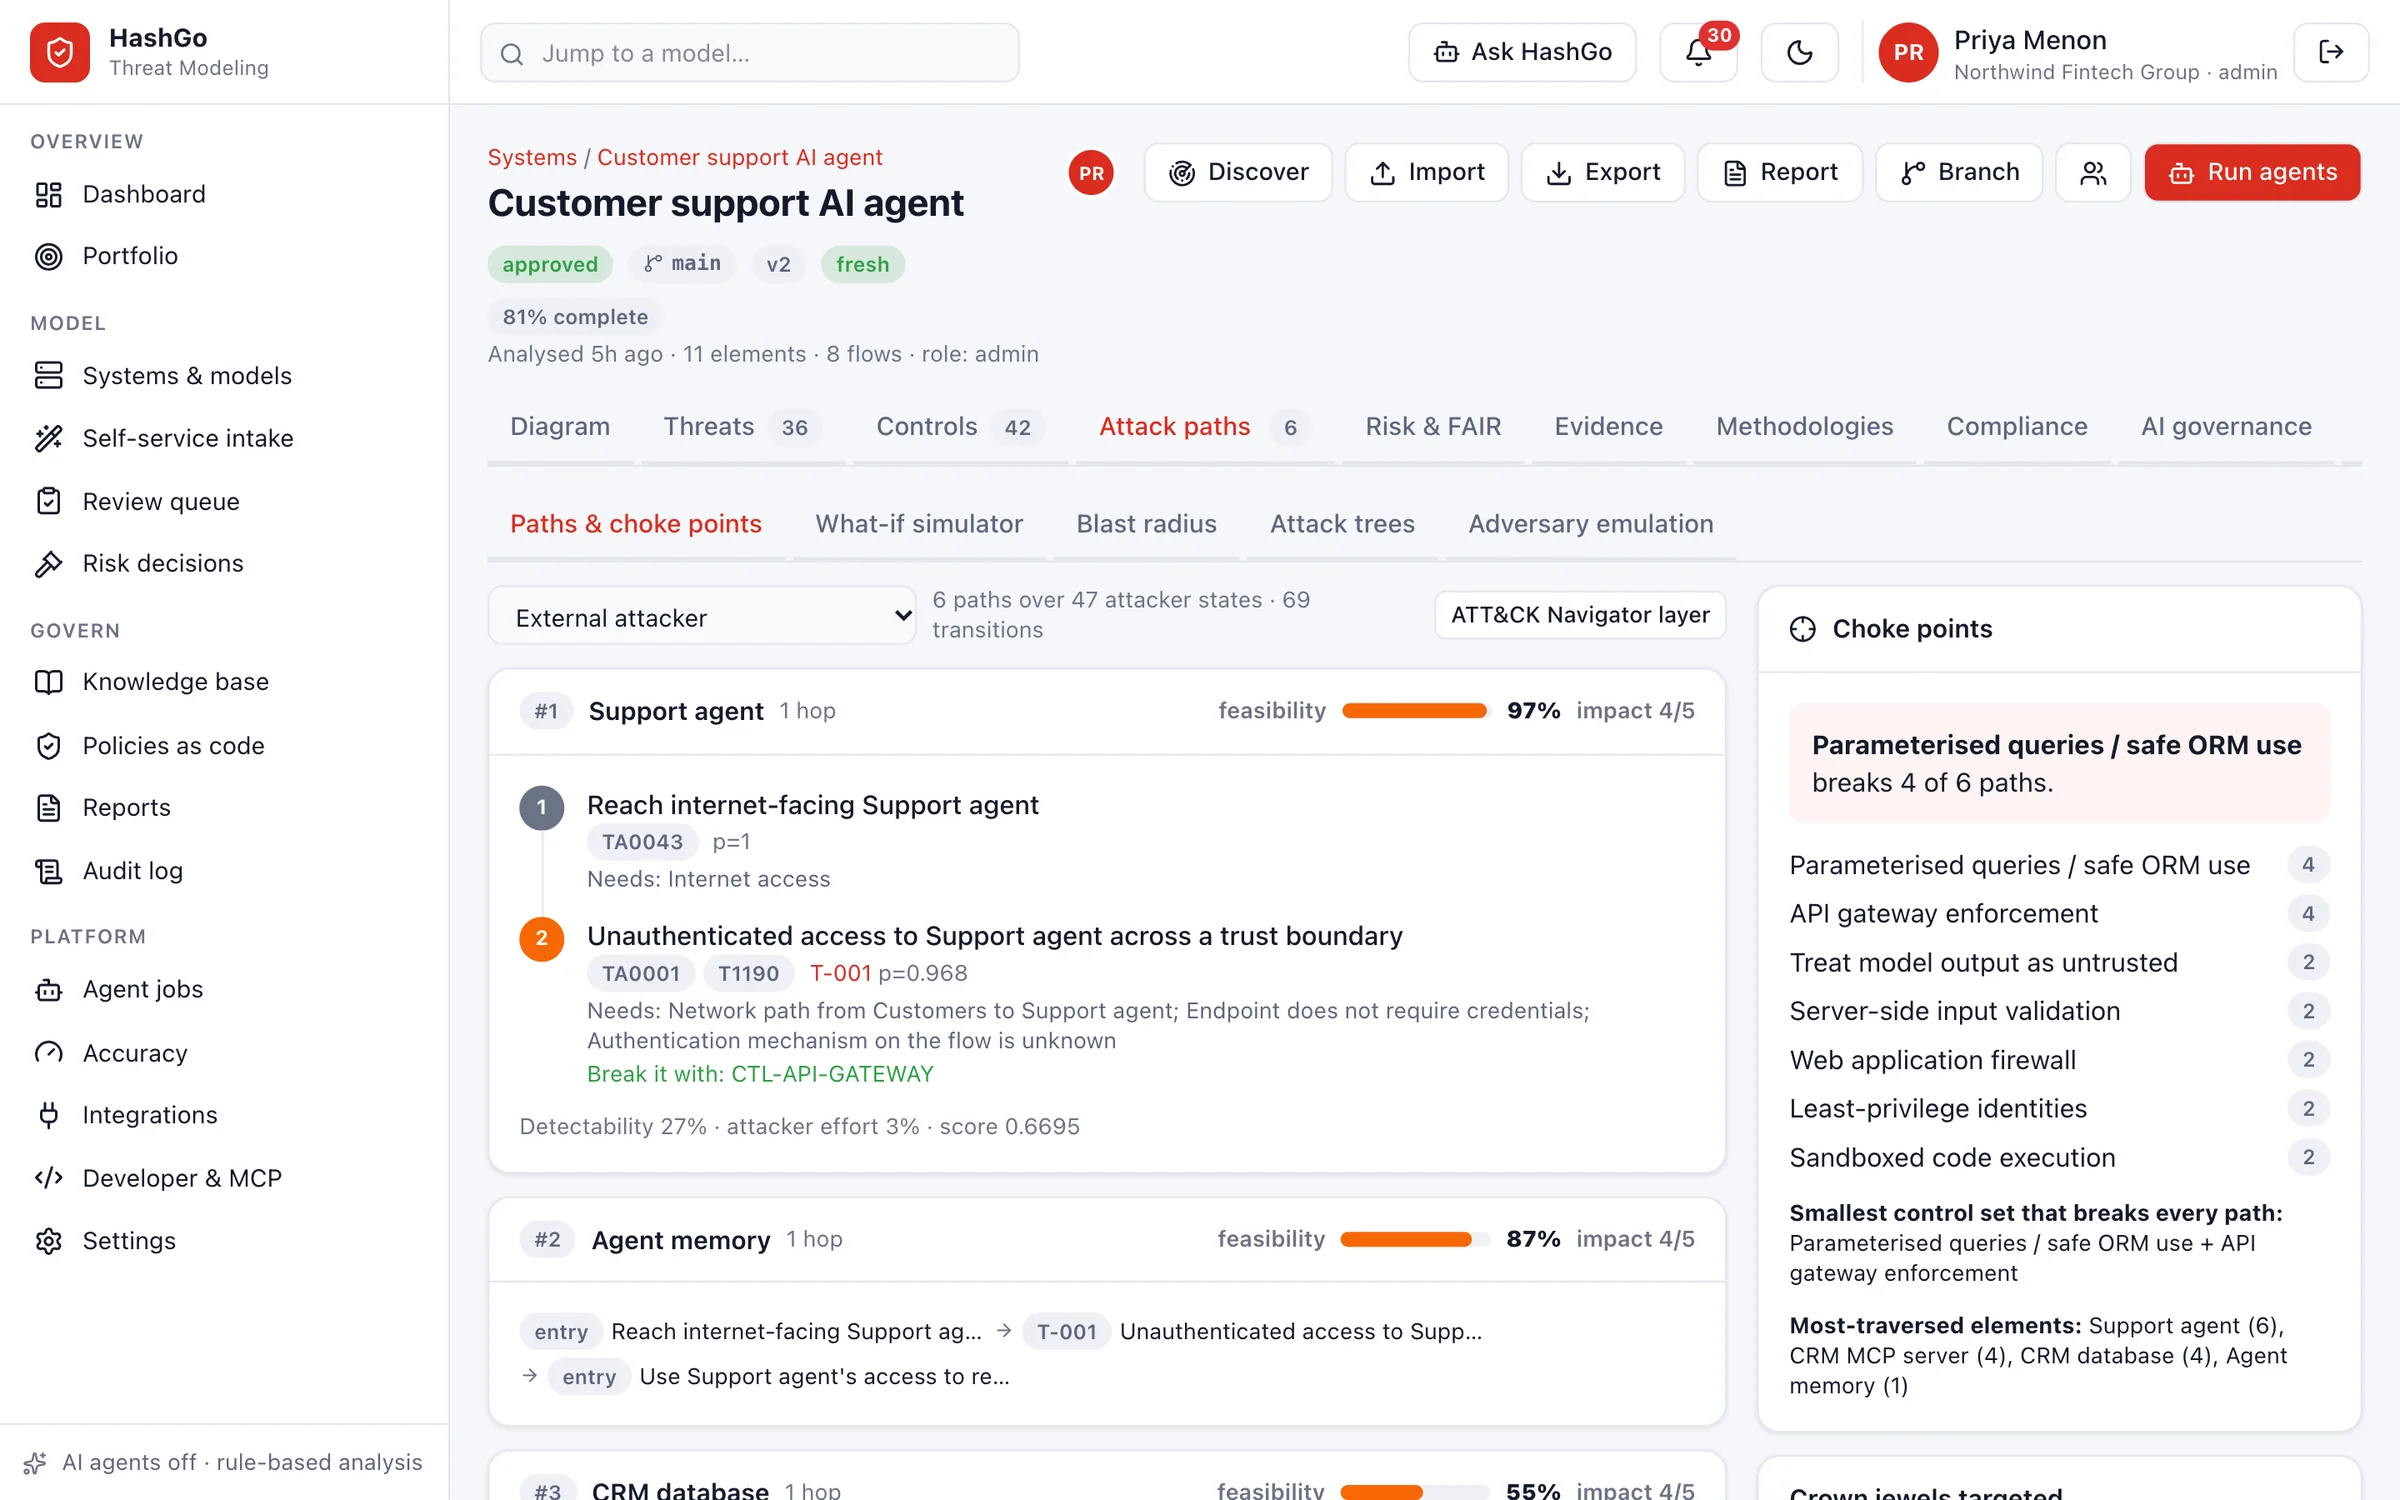
Attack paths ranked by feasibility from an external attacker to crown jewels, with the choke-point controls that break the most paths
Attack paths. Routes to your crown jewels and the control that breaks the most of them.
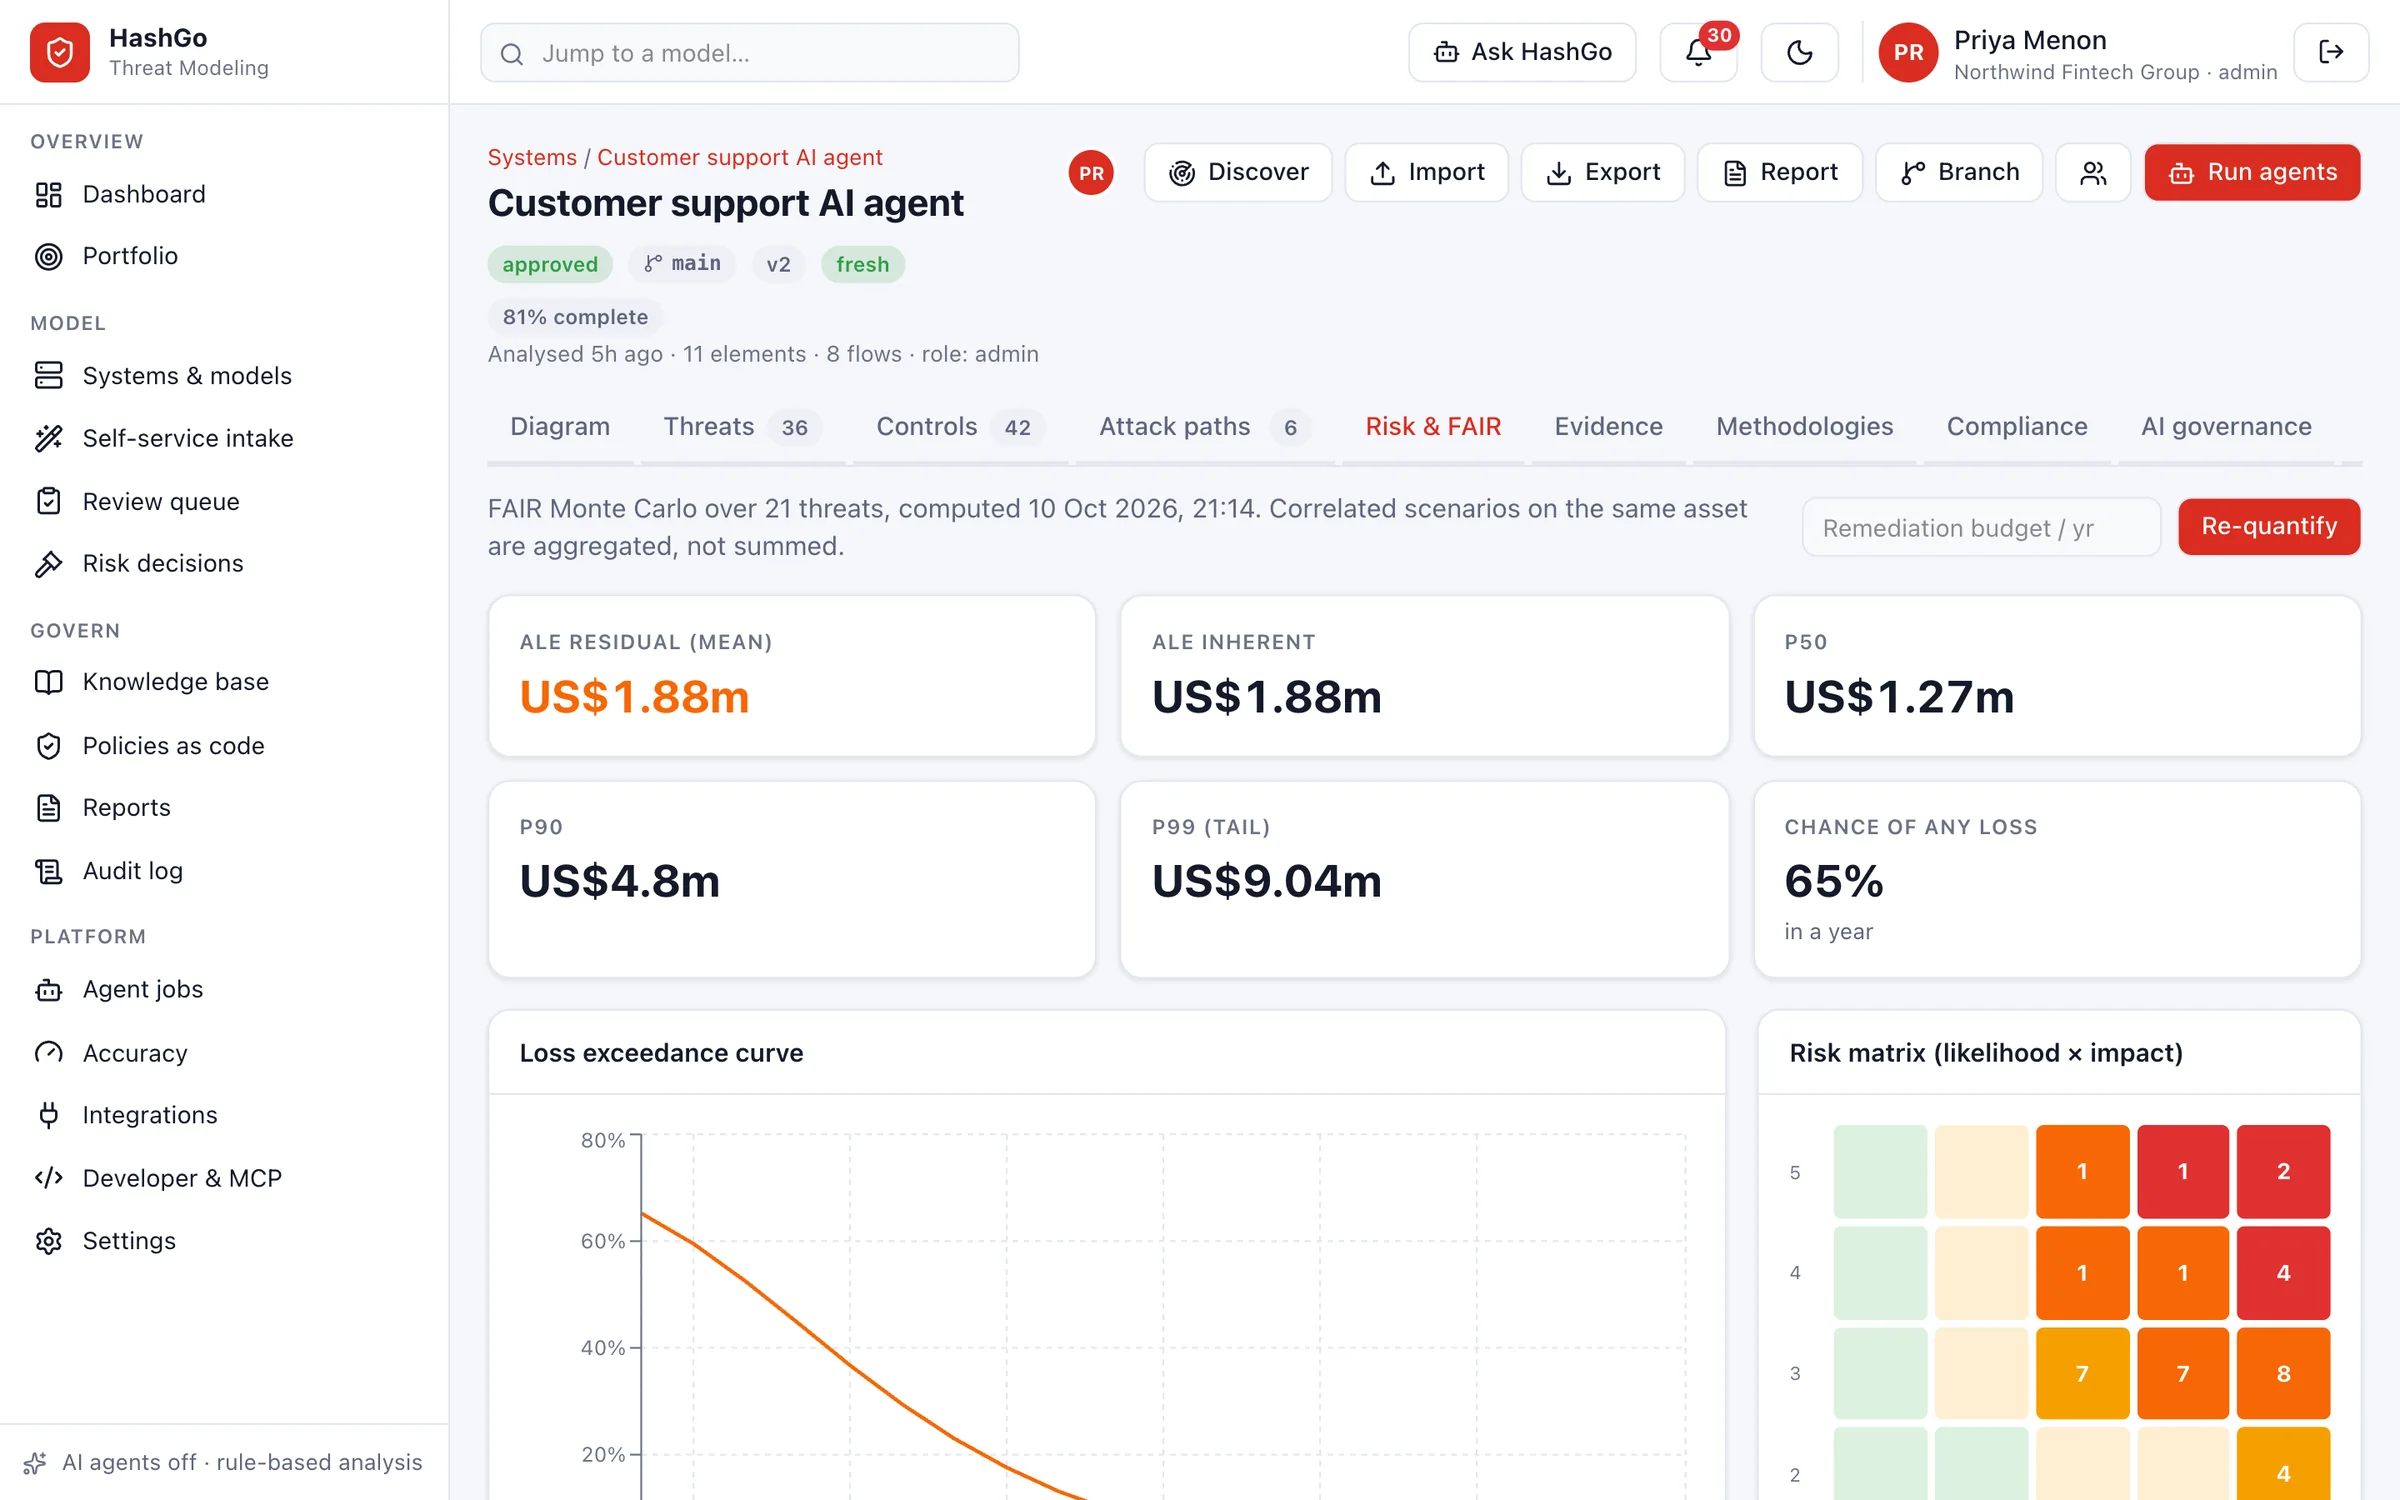
FAIR risk view with annualised loss, P90 and P99 tail loss, a loss exceedance curve and a likelihood by impact risk matrix
Risk in money. FAIR loss estimates, tail risk and a likelihood by impact matrix.
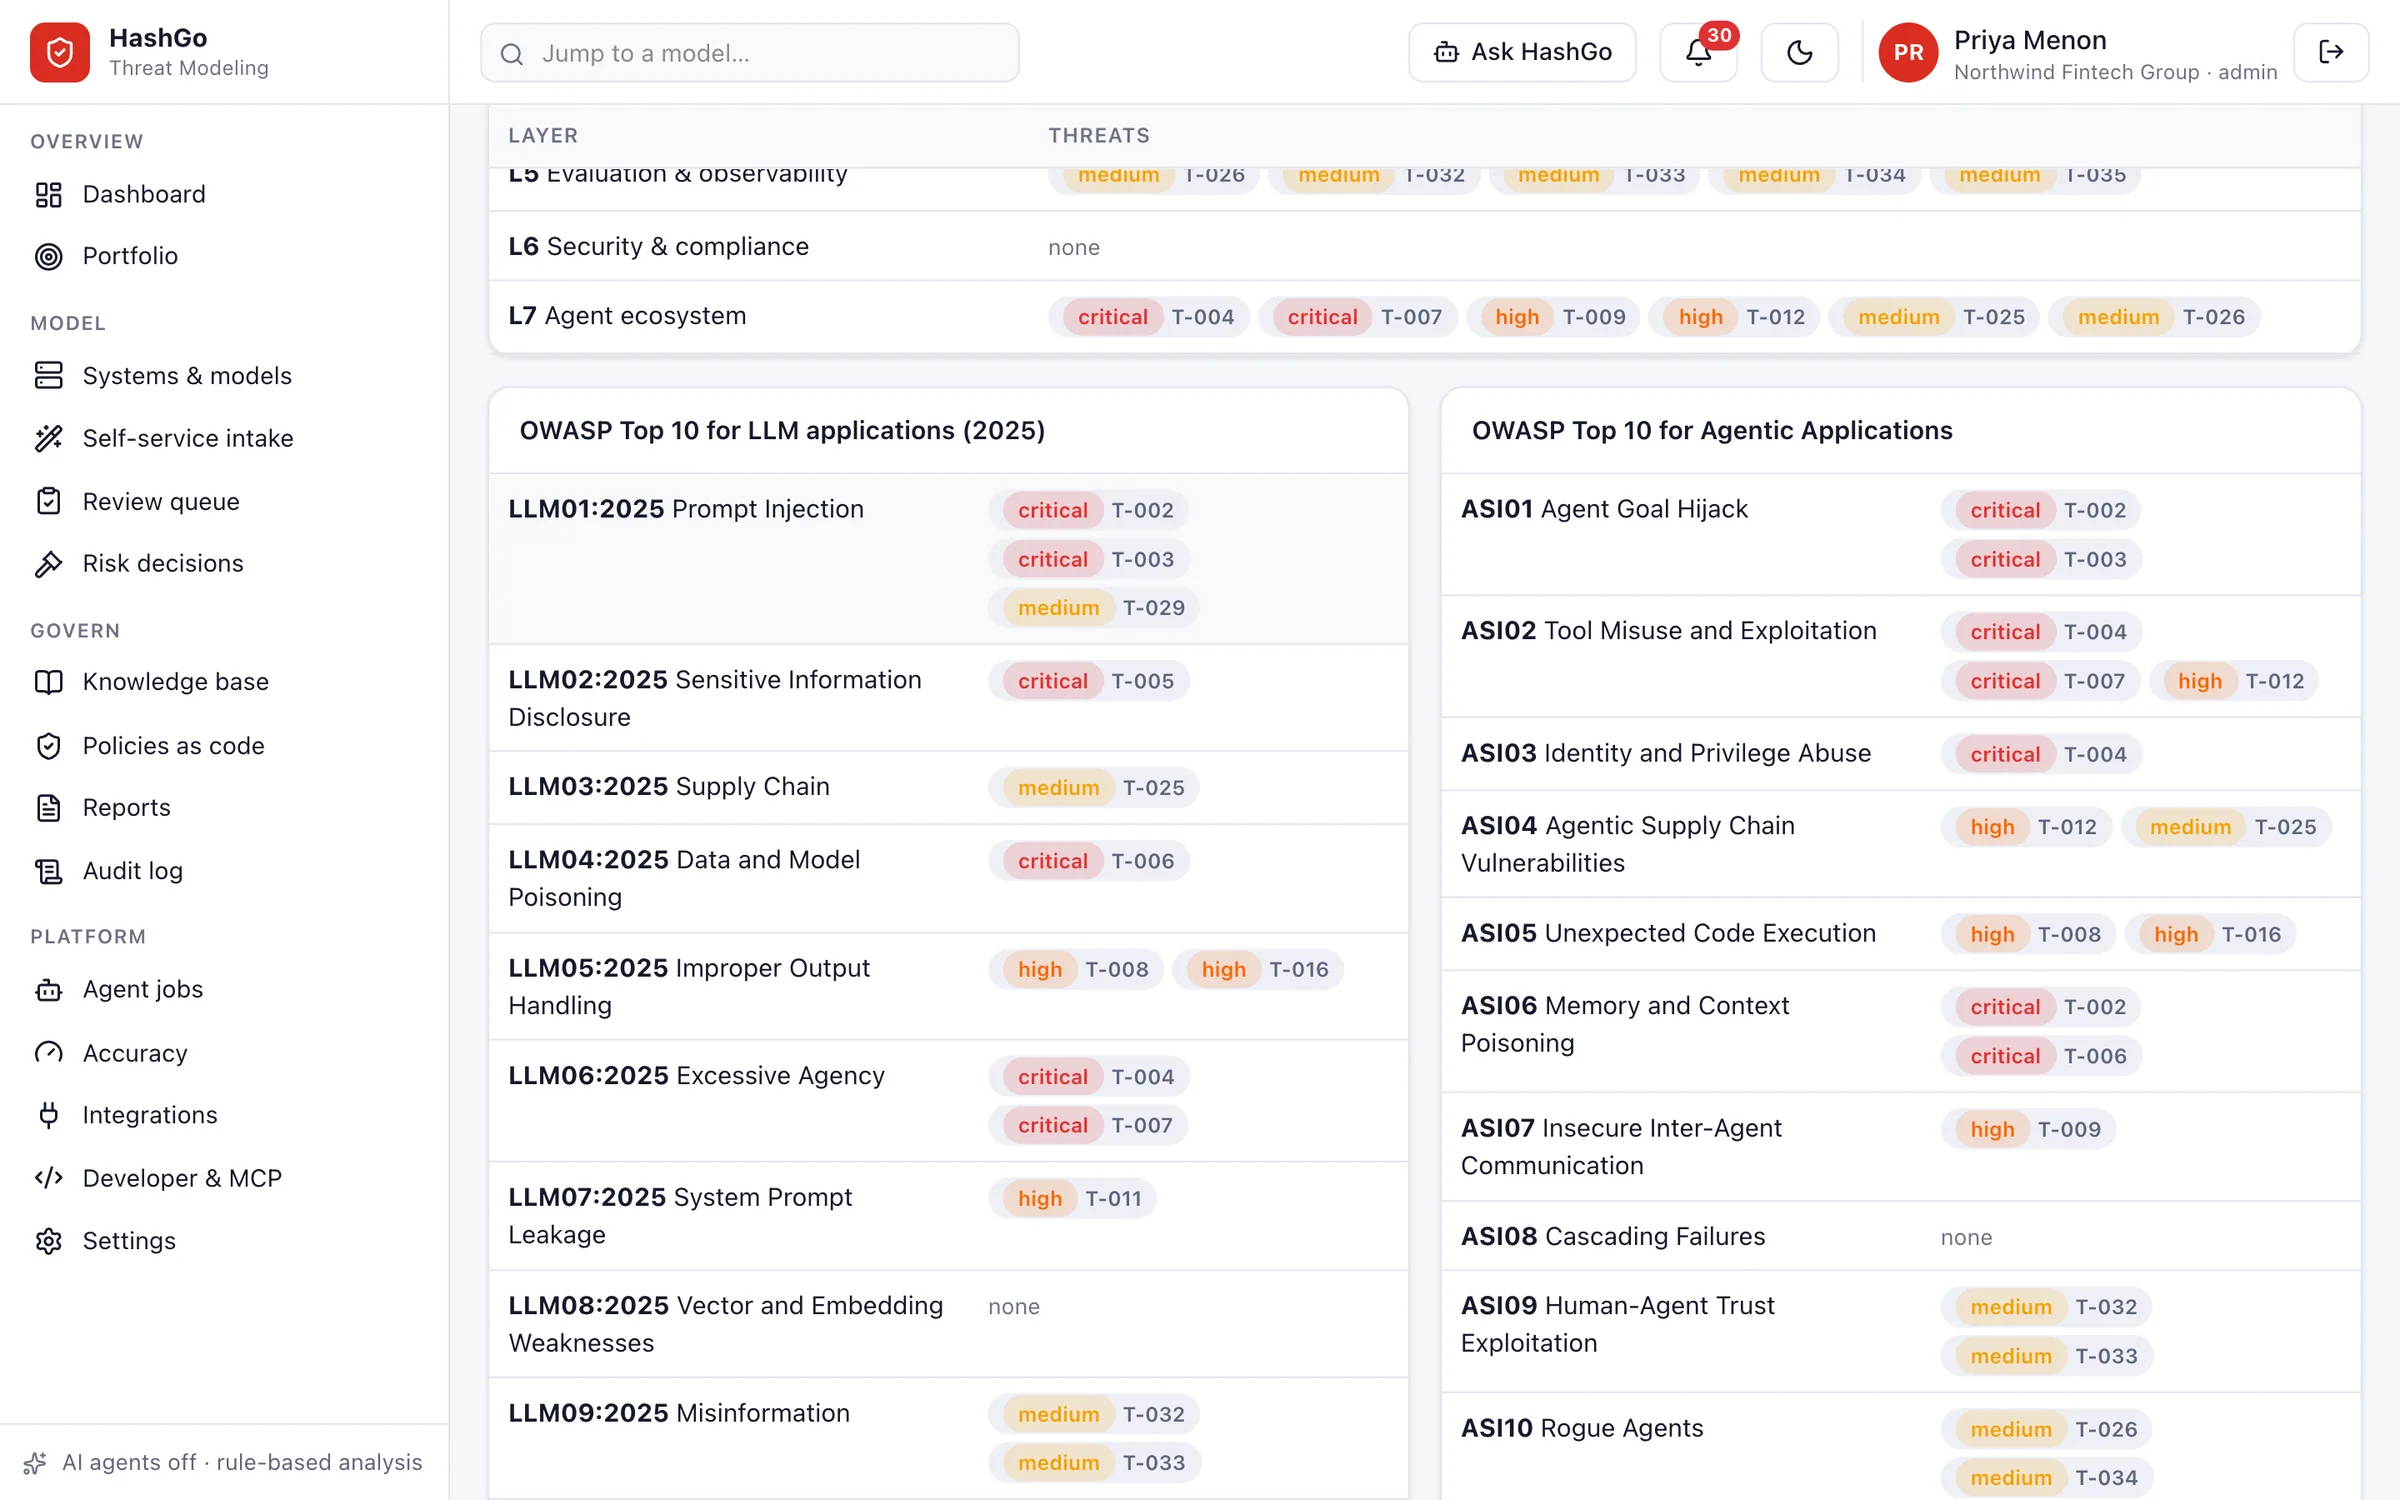
AI threat view mapping threats to the OWASP Top 10 for LLM applications and the OWASP Top 10 for agentic applications
AI and agents. LLM and agentic threats mapped to OWASP and MAESTRO.
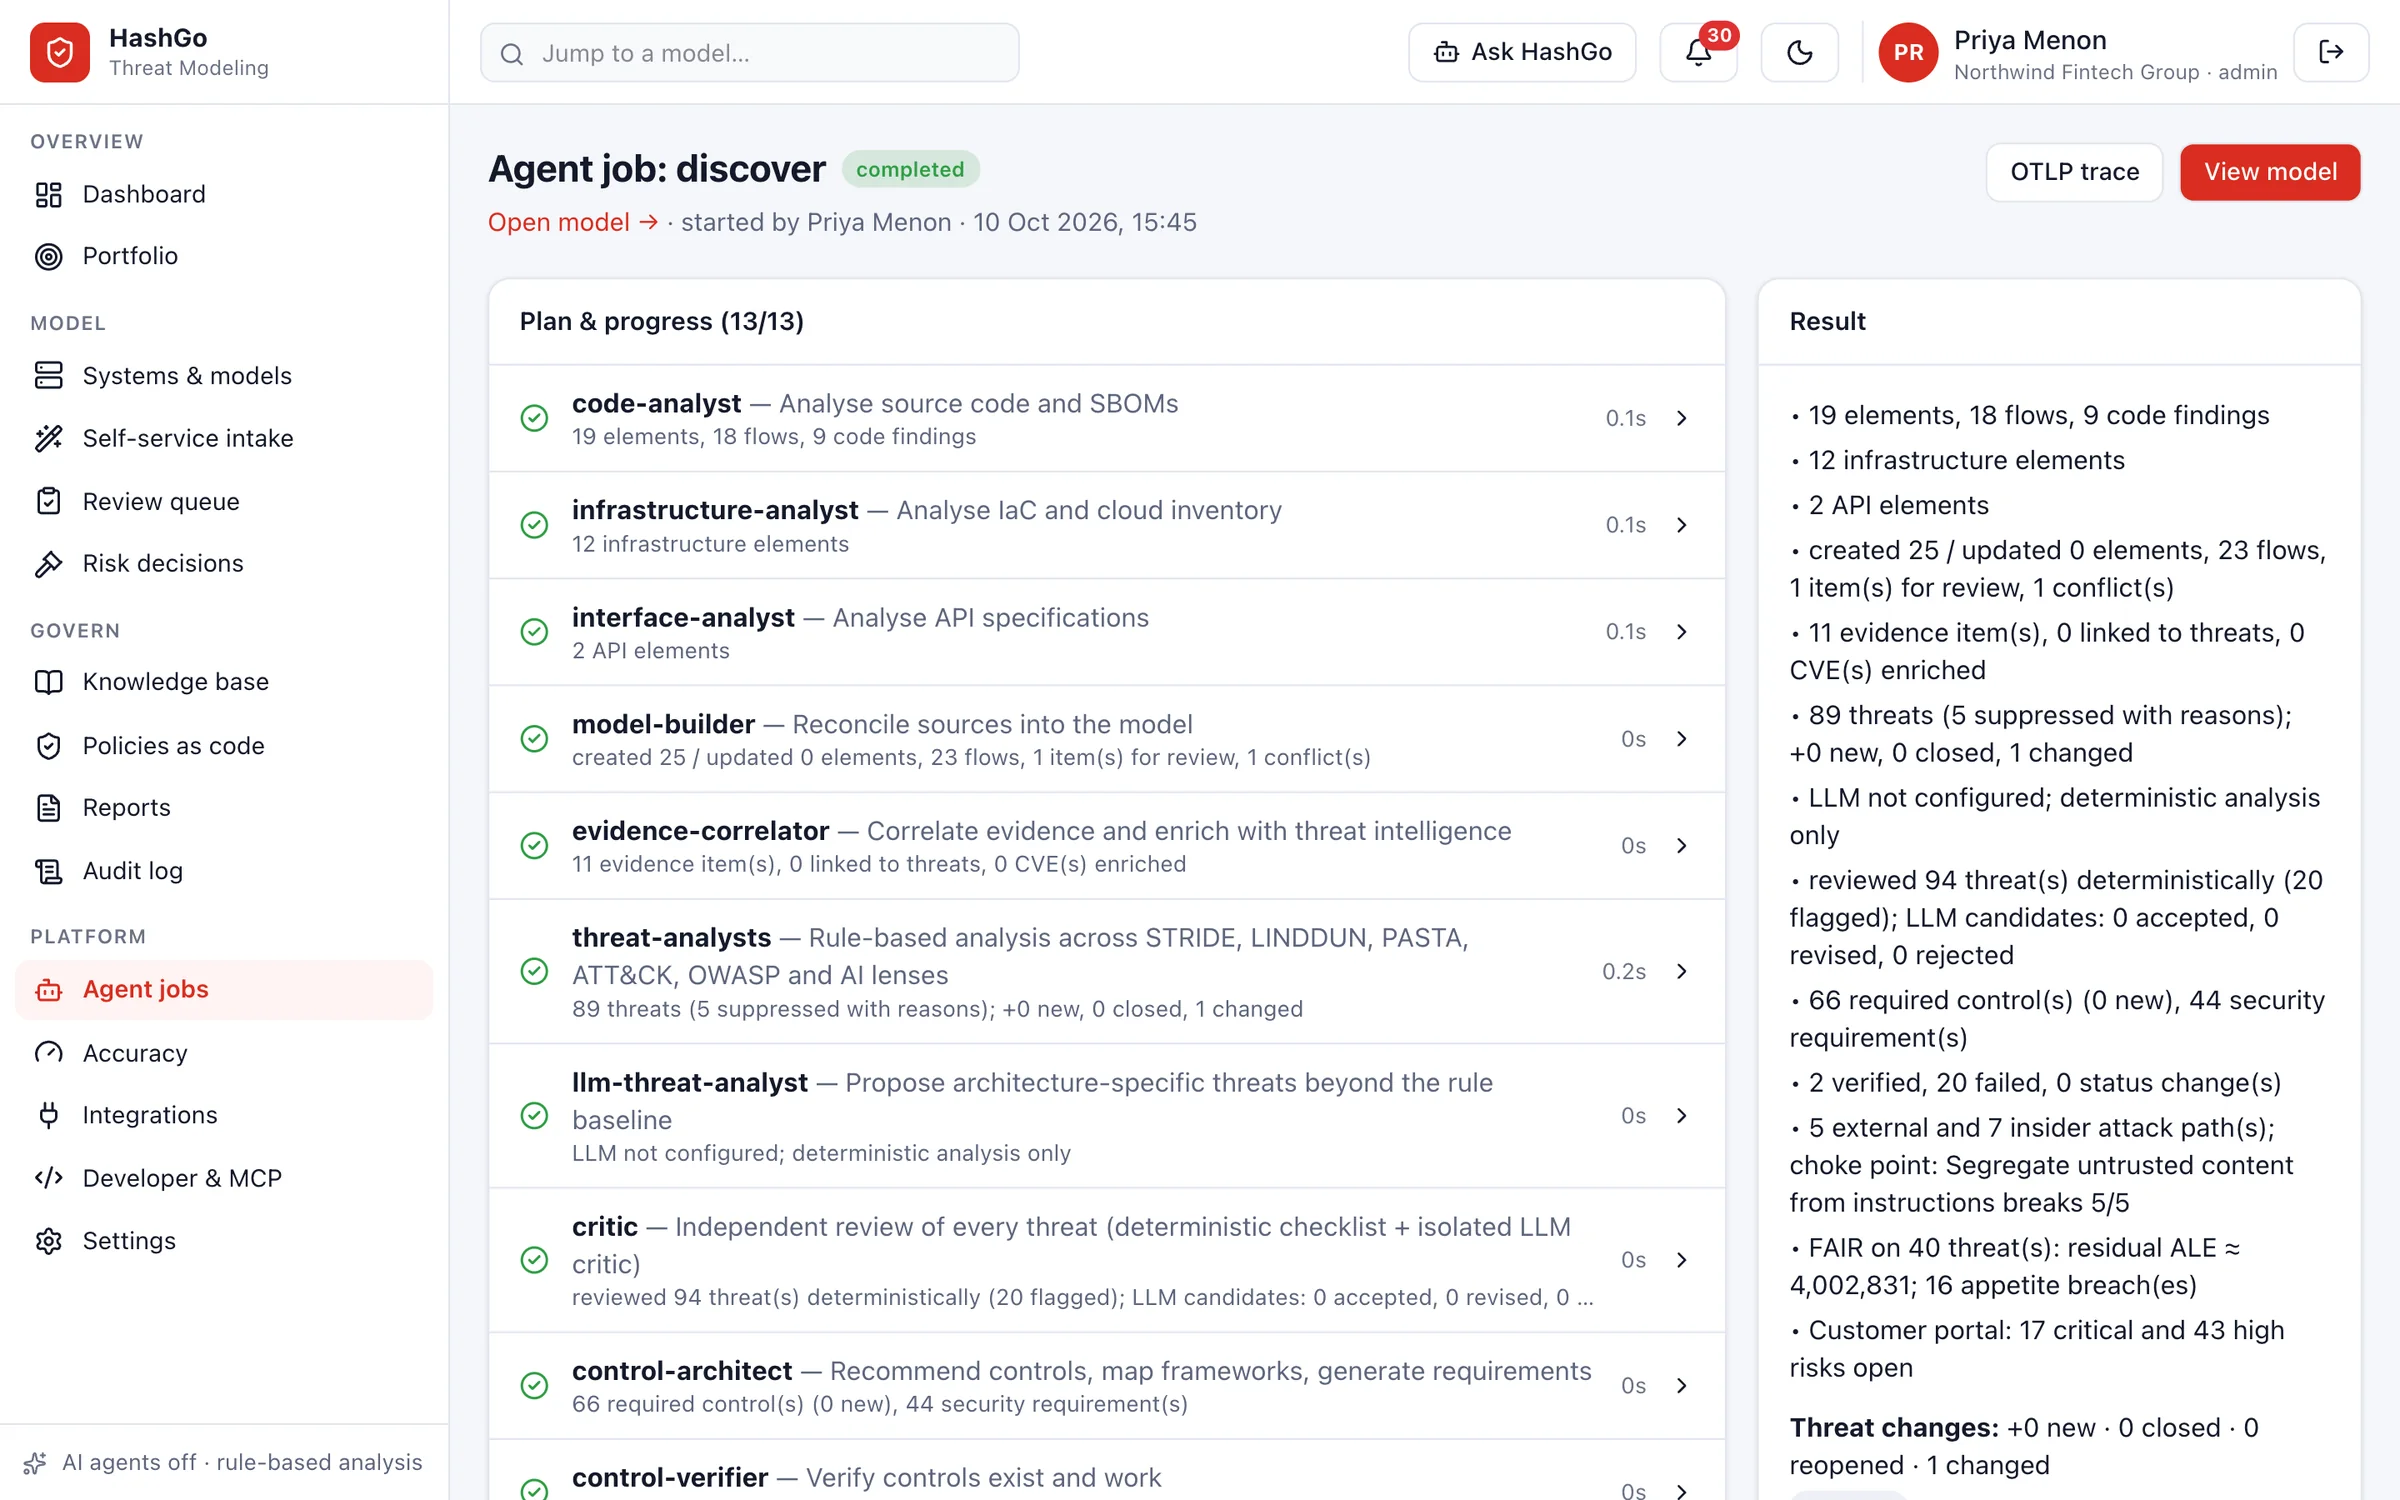
Agent job showing code, infrastructure, interface, threat, critic, control, attack-path and risk agents completing a discovery run
Agents. Every run planned, traced and budgeted, step by step.

Screens from the live platform with sample data from a fictional company. Loss figures use editable FAIR assumptions; your own model uses your revenue, asset values and risk appetite.

Why not use the free tools?

Free tools draw diagrams. HashGo keeps the model for you.

Free tools draw diagrams and list generic threats. HashGo builds and maintains the model for you and tells you what each risk costs.

Microsoft Threat Modeling ToolOWASP Threat DragonHashGo Threat Modeling
Who draws the modelYou, by handYou, by handAI agents from code, cloud and documents; you review
Stays currentManual redrawManual redrawUpdates on every pull request and cloud change
AI and agent threatsNoLimitedOWASP LLM and Agentic Top 10, MAESTRO, ATLAS
Attack pathsNoNoPaths to crown jewels for four attacker profiles
Risk in moneyNoNoFAIR loss estimates and best remediation budget
Developer workflowDesktop appDesktop / web appPR gate, CLI, VS Code, MCP server, ticket sync
Compliance mappingNoNoISO 27001, PCI DSS, SOC 2, DORA, NIS2 and more
Import existing modelsn/an/aYes, from both tools and OTM

Keep your existing models: import them from Microsoft TMT or Threat Dragon in one click.

Capabilities

What Threat Modeling does.

From a blank page to a reviewed, quantified model in minutes, kept current on every pull request.

01

Models that build themselves

Agents read what you already have, and show where each fact came from.

  • Code in 10+ languages, IaC, API specs and SBOMs
  • Live AWS, Azure, GCP and Kubernetes inventory
  • Design documents, diagrams and whiteboard photos
  • Provenance and confidence on every element; conflicts sent for review
02

Threats from your design

Threats that follow from your architecture, each with the reason it applies.

  • 115 explainable rules across STRIDE, LINDDUN and PASTA
  • Mapped to CWE, CAPEC, MITRE ATT&CK and OWASP
  • AI analyst for threats beyond the rules, checked by an independent critic
  • Duplicates merged; non-applicable threats suppressed with a reason
03

Built for AI systems

LLM apps, RAG pipelines, agents and MCP servers modelled as first-class components.

  • OWASP LLM Top 10 and Agentic Top 10, MAESTRO, MITRE ATLAS
  • Prompt injection, excessive agency, tool and memory abuse
  • EU AI Act risk tier, ISO/IEC 42001 and NIST AI RMF
  • Red-team plans for promptfoo, garak and PyRIT
04

Attack paths and money

Know which threats chain into a breach, and what it would cost.

  • Attack paths to crown jewels for four attacker profiles
  • Choke points, blast radius and a what-if simulator
  • FAIR loss quantification with risk appetite and escalation
  • The remediation plan that cuts the most loss per rupee or dollar
05

Continuous, inside delivery

The model changes when the system does, and gates the changes that add risk.

  • Pull-request gate with SARIF and policy-as-code exit codes
  • CLI, VS Code extension and an MCP server for AI coding assistants
  • Drift and freshness tracking; stale models flagged
  • Tickets in Jira, Azure Boards, GitHub, GitLab, Linear or ServiceNow, kept in sync
06

Accuracy you can measure

Every claim the system makes can be checked, corrected and scored.

  • Plain-language explanations at three levels of detail
  • Labelled benchmark suite with precision and recall
  • Confidence calibrated from reviewer feedback
  • Prediction rate against real incidents and pentest findings

How it works

Four steps, start to finish.

01

Connect or describe

Point it at a repository or cloud account, upload documents, or describe a feature in plain language.

02

Agents build and analyse

The model is drawn, threats are found and checked, and paths and loss are computed.

03

Review and decide

Confirm what the agents were unsure about, accept or treat risks, and send work to your tracker.

04

Stay current

Every pull request and cloud change updates the model and is gated by your policies.

Coverage

What it covers.

Methods

  • STRIDE
  • LINDDUN
  • PASTA
  • FAIR
  • CVSS 4.0

Threat knowledge

  • MITRE ATT&CK
  • MITRE ATLAS
  • CWE
  • CAPEC
  • OWASP Top 10 2025
  • OWASP API Top 10

AI and agents

  • OWASP LLM Top 10
  • OWASP Agentic Top 10
  • CSA MAESTRO
  • EU AI Act
  • ISO/IEC 42001
  • NIST AI RMF

Compliance mapping

  • ISO 27001
  • NIST 800-53
  • PCI DSS
  • SOC 2
  • DORA
  • NIS2

Imports and platforms

  • Open Threat Model
  • OWASP Threat Dragon
  • Microsoft Threat Modeling Tool
  • Terraform
  • Kubernetes
  • AWS
  • Azure
  • Google Cloud

Data handling

Your design stays yours.

How the hosted service treats your models, code and documents.

Where your data lives

The hosted service runs in India (Mumbai). Connections use TLS, and API keys and integration credentials are encrypted in the database.

AI processing

AI steps send only the text they need to the model provider configured for your plan. Rule-based analysis, attack paths, risk figures and gates run without AI. On Enterprise, use your own key or a private model.

What we read

Read-only access to repositories and cloud accounts. We never change your code or infrastructure; we only post pull-request comments and update the tickets you connect.

Your choice of deployment

Shared cloud, or on Enterprise a dedicated single-tenant service or an installation inside your own network.

Retention

Uploaded source archives are deleted once discovery finishes unless you choose to keep them. Delete a model at any time, and export everything in Open Threat Model (OTM) format.

Accountability

Every human, agent and API action is written to a tamper-evident, hash-chained audit log. Security questions: info@threatxintel.com.

Threat modeling and the HashGo suite

Design, code and controls, connected.

Threat Modeling decides what could go wrong. SAST checks the code that was written. GRC proves the controls are in place.

HashGo Threat ModelingHashGo SASTHashGo GRC
What it examinesThe architecture: components, data flows, trust boundariesSource code, without running itControls, policies and evidence
When it runsAt design time and on every changeOn pull requests and in CIContinuously, against your frameworks
Typical outputThreats, attack paths, required controls, loss estimatesVulnerabilities proven at the exact lineCompliance status and audit evidence
Works before code existsYesNoYes

Pricing

Priced per modelled system. Unlimited users from Team.

Published prices, a free plan for evaluation, and AI included on every plan.

Prices are per organization per month, billed yearly.

Free

Evaluation and small teams

₹0

$0

  • 3 modelled systems
  • 3 users
  • AI model building
  • STRIDE threats
  • Import from Microsoft TMT, Threat Dragon and OTM
Model a system free

Team

Product and platform teams

₹15,000/month

$199/month

  • 10 modelled systems
  • Unlimited users
  • All methods, AI and agent threats
  • Attack paths
  • Pull-request gate, CLI, VS Code
  • Jira, GitHub and GitLab sync
Request access

Enterprise

Banks, insurers, groups and the public sector

From ₹15 lakh/year

From $25,000/year

  • Unlimited systems
  • Everything in Business
  • Single-tenant or on-premises
  • Regional hosting
  • Custom threat libraries
  • Bring your own AI key
  • Named manager and SLA
Talk to sales
  • A modelled system is one application or service with its own threat model. Versions, branches and archived models are free.
  • INR prices exclude 18% GST; USD prices exclude local taxes.
  • Monthly billing costs 20% more than yearly billing.
Compare every feature by plan
FeatureFreeTeamBusinessEnterprise
Modelling
AI model building from code, IaC, API specs and design documentsIncludedIncludedIncludedIncluded
Import from Microsoft Threat Modeling Tool, OWASP Threat Dragon and Open Threat ModelIncludedIncludedIncludedIncluded
Visual editor, templates, versions and branchesIncludedIncludedIncludedIncluded
Modelled systems31050Unlimited
Users3UnlimitedUnlimitedUnlimited
Self-service intake for product teamsNot includedIncludedIncludedIncluded
Live cloud discovery (AWS, Azure, Google Cloud) and KubernetesNot includedIncludedIncludedIncluded
Analysis
STRIDE threats, each with the reason it appliesIncludedIncludedIncludedIncluded
All methods: LINDDUN, PASTA, MITRE ATT&CK, OWASPNot includedIncludedIncludedIncluded
AI and agent threats: OWASP LLM and Agentic Top 10, MAESTRO, MITRE ATLASNot includedIncludedIncludedIncluded
Attack paths, choke points and what-if simulationNot includedIncludedIncludedIncluded
Risk in money: FAIR loss estimates and best remediation budgetNot includedNot includedIncludedIncluded
Compliance mapping: ISO 27001, PCI DSS, SOC 2, DORA, NIS2; AI governanceNot includedNot includedIncludedIncluded
Custom threat libraries and methodologiesNot includedNot includedNot includedIncluded
Developer workflow
Pull-request gate, CLI and VS CodeNot includedIncludedIncludedIncluded
Jira, GitHub and GitLab syncNot includedIncludedIncludedIncluded
MCP server for AI coding assistantsNot includedNot includedIncludedIncluded
ServiceNow and Azure BoardsNot includedNot includedIncludedIncluded
Full REST APINot includedNot includedIncludedIncluded
AI
AI agents included (full analyses per system per month)555Contracted
Bring your own AI key or a private modelNot includedNot includedNot includedIncluded
Security and deployment
Tamper-evident audit logNot includedNot includedIncludedIncluded
Single sign-on (OIDC) and SCIM provisioningNot includedNot includedIncludedIncluded
Single-tenant or on-premises; regional hostingNot includedNot includedNot includedIncluded
SupportCommunityEmail, next business dayPriority, business hours IST / GSTNamed manager and SLA

AI usage

AI included on every plan.

Eighteen agents take part in a full analysis. The allowance below keeps costs predictable; rule-based analysis never stops.

PlanAI allowanceWhen the allowance is used up
Free, Team and Business5 full AI analyses per system per month: an analysis, a discovery run, a self-service intake or a diagram importRule-based analysis, attack paths, risk figures and gates keep running; the allowance resets on the 1st
Pull-request checksIncremental and rule-based, so they do not countNot affected
EnterpriseBring your own key (Anthropic, Amazon Bedrock, Google Vertex AI) or a private modelNo allowance; your provider bills you directly

Add-ons and services

Extend any plan.

Add-onIndia (INR)International (USD)
Extra system on Team₹1,800 / month$25 / month
Extra system on Business₹1,100 / month$15 / month
Expert-led threat modeling workshop (per system)₹75,000$1,000
Architecture security review by ThreatXIntelQuotedQuoted
HashGo suite bundle: Threat Modeling with SAST or GRC20% off20% off

Offers and billing

TermDetail
Launch offer30% off the first year for the first 20 customers
Billing cycleYearly in advance by default; monthly available at +20%
Adding systemsExtra systems are billed pro rata for the rest of the term
Payment in IndiaBank transfer, UPI or card, with a GST tax invoice
International paymentWire transfer or card in USD
Enterprise payment termsNet 30 days from invoice
Billing entityThreatxintel Cyber Labs LLP, Bengaluru, India

Prices are valid from 10 October 2026 and may change with notice. Existing customers keep their price until renewal.

FAQ

Questions, answered.

Something else? Ask the team.

Do I need to give you my source code?

No. You can start from a design document, a diagram or a plain-language description. Code and cloud access make the model more accurate.

Will it replace my security architects?

No. It does the drafting and keeps the model current; your team reviews what the agents were unsure about and makes the risk decisions.

Can it gate releases?

Yes. Pull requests that add unacceptable risk can fail the build through policy-as-code, with SARIF results in GitHub, GitLab or Azure DevOps.

How accurate is it?

Every threat shows why it applies and how confident the agents are, and anything uncertain goes to a review queue. Every release is checked against a labelled benchmark of 24 reference systems; precision and recall measured in customer pilots will be published on this page.

How long does a first model take?

In our internal test of five open-source repositories, the median was 5 seconds from connecting the repository to the first model, and the largest took 37 seconds. AI review runs after the first model is drafted.

What does it cost?

Free for up to 3 systems; paid plans from ₹15,000 / $199 a month. See pricing.

Does it work with HashGo SAST?

Yes. Threat Modeling says what could go wrong in the design; SAST proves what is actually exploitable in the code; findings link to the same threats.

Where is my data stored?

The hosted service runs in India (Mumbai). Enterprise customers can choose a dedicated single-tenant service or an installation inside their own network. See data handling.

What happens when we use up the AI allowance?

Rule-based analysis, attack paths, risk figures and the pull-request gate keep working. AI steps resume when the allowance resets on the 1st of the month.
Start free: 3 models, no card.

Connect a repository or describe a system, and see its threats, attack paths and risk in minutes.